Tag Archives: CIA

When we are merely given a paragraph

It happens, we get offered a paragraph and for some reason we wake up, we think: ‘That’s nice! Tell me more!‘ It can be for the strangest and least connected reasons out there. No matter that the push or the reason, we only get that one paragraph and are left hanging. That feeling came right off the bat when ABC gave me ‘ASIO warns of ‘hostile intelligence services’ using social media in annual report‘ (at https://www.abc.net.au/news/2019-10-17/asio-warns-of-hostile-intelligence-services-on-social-media/11609726) a day ago. Now, let’s be fair, ASIO is not really the one to play games of open communication, as its employees and governing staff were educated by the people of Sneaky, Peeping and Backstabbing incorporated, they have other markers to work with. As such as I was fed ““hostile intelligence services” using social media to target people across business and government“, which basically is a continuation (to some degree) of the quote we saw at ABC in July 2017 when we were given “help Australian security agencies get access to encrypted messages from suspected terrorists and other criminals“, in itself not an issue one would think, and there is exactly the problem, one did not think. I made references to private chat groups in Social media and extremism before 2016, just nice to know that someone gets around and wakes up every now and then. Or as I would phrase it as ‘What else is new?‘, Yet as Jade MacMillan takes us by the hand in this ABC article, we see: “A report in the New York Times earlier this year claimed China was using LinkedIn to try to recruit foreign spies“, again we go with the ‘What else is new?‘. There is nothing new under the sun as MI-6, CIA, DGSE and optionally ASIS have been using that very same tool to get information. The honey traps, the enticement parties and the stage where you are a winner, the tricks are as old as the very first sign stating: ‘Authorised Personally Only‘. In this the larger issue is avoided, you see financial entrepreneurs have been using these paths to gain information on how to find people with debts and some of them have (allegedly) been reporting those people to international whisper divisions, so that a deal could be struck. So whilst some look for foreign agents, they all ignore the debt collectors mining every bit of social media to gain a momentary advantage to collect on one debt and gain another bonus, and those people will always look for investors, especially investors that have a fluidic opinion of ethics and how to be working towards rewards.

It all comes across as silly and as mindless as “Attorney-General George Brandis said encryption was potentially the “greatest degradation of intelligence and law enforcement capability” in a lifetime“, he could not put gamers in a proper dimensional view, so why would he get this right? It is an easy enough question and there is a link. There was a reason why Facebook suspended and ended all group chat options (there were a few actually), they were off course way late, now that Lone wolves and others have found new means to get this started, they need to be more careful, but the state remains. Mining is the only way to do this and you need resources for that, as well as proper staff who comprehend data and not let some silly deep learning algorithm fix it. For example, consider that a facilitator created an auto fill chat system; it has 250,000 lines an hour, whilst the system has one anchor word, a word you can select. So as we see the chat go through, we make no sense on it, yet the users have set the word ‘الدراجين’ (meaning ‘riders’) even as the initial part makes no sense

WE now get:

يتيح للجميع وقتا طيبا والحزب

الهذيان الكبير في واحة في منتصف الليل

جميع الدراجين سباق اليوم

معلومات السباق في اللعبة

تسجيل جميع الدراجين بعد صلاة الفجر

يجب أن المؤمنين اقتبس مرور البقر

جميع الدراجين يعرفون أن السيارة مائة مؤهلة


Even in this setting the programming cannot make sense, and unless you knew that ‘riders’ was the operative word good luck in finding what comes next. a system like this has been in place for years, now there are dedicated programs, yet in the past there were 4-6 in a group of 100, so those 4 guest gamers would not be noticed and by the time someone woke up, it was already too late, the meeting was over and more secure conversations had taken place, this system worked global and now that Facebook chat groups are a thing of the past other means are used for all kinds of groups to find a way to pass a message along.

We get it, the employees of Sneaky, Peeping and Backstabbing incorporated are not supposed to put it in the open, yet the annual report seemingly ignores one part. Instead of having a dozen systems creating a small solution, we need to find the agencies actually working together to avert “ASIO has limited scope to redirect internal resources to address the increasing gap between demand for our counterespionage and foreign interference advice and our ability to furnish this assistance” and partially find a solution that will take care of the extremists, the organised crackpots and the corporate facilitators, if you do not consider the third group to be important, then you have remained asleep for far too long at the wheel.

So when I mentioned Brandis (never the sharpest tool in my personal opinion) we might consider the 2017 event and the quote: “If the laws are passed and technology companies comply, they could help with investigations into paedophile networks, major organised crime or terrorism”, the man is transparent as glass as he hid in the past behind ‘violent gamers’ and now he uses ‘paedophile networks’. Yet the larger issue not seen here are financial services, there is no oversight and there is no telling what an approached debt collector could find out without setting of ANY red flags. And that is with the players who are on the up and up and playing a proper game taking all the proper guidelines and consumer protection laws as noticed and complied with, this wild west group has a truckload of groups all willing to do what it takes to get the score and a foreign player is a stakeholder in finding needs. That group has been able to remain off the books for at least 2 years. They all seemingly forgot that places like Experian, Equifax, Dun & Bradstreet, have their own customer base and who checked out those credentials?

Yes, we can agree that the entire matter is too large for ASIO to deal with, but there is also the flaw that the scope of what they face is not dimensionalised in the proper fashion, it is openly misrepresented and that is optionally acceptable, as long as they know what they face in-house.

And it is not a rocket science deal; the FBI, MI5, BRGE, AIVD, MAD (yes that is the acronym for the German Intelligence Services) and the FSB all deal with these issues. OK, these players will not be calling the FSB but you get the idea. There are players that are about data and proper intelligence mining (Palantir Technologies), yet the field needs to widen but in another direction. If this is Business Intelligence then Palantir is SAS, whilst we need a more IBM statistics and IBM Modeller based solution rolled out, we do not need a solution that fits all, we need to feed clusters of investigators with power tools that allow them to surf data and mine activities to a much larger degree. We need to set server milestones with collected raw data that different clusters can attack. The intelligence branches have wanted to do it the wrong way around for too long (often pressured by wannabe politicians), what we need is a treasure trove of data that all players can have a go at and actually report findings. We create almost 3 Exabyte of data every day, and we need to find 1% of 1% in that, whilst all this happens before 5G, it is about to become 20 times worse and they cannot even handle what is out there now.

All whilst we know that the 1% of 1% remains a group of 98% which is merely misdemeanours playing around, as such we need to change the premise towards collected data, that is what we face at present so the entire matter of “greater awareness among our stakeholders of that threat — has increased demand for our advice and support”, which is misrepresentation in its own right. The stakeholders have their own needs and their own game to play. Consider the IP needs of Telstra (Australia), the Inside protection and mandates of Novartis (Pharmaceuticals), Insider trading on HSBC (Banking) and their needs are their financial protection needs and in this fearless leader Duncan Lewis (ASIO) has to optionally look out for the needs of Telstra (as some claim that hat Telstra needs, Australia needs) whilst hunting those wanting to harm Australians, in this the Stakeholders are more about the revenue and debatable a source of good (they allegedly merely want their bonus safe), as such we should optionally wonder about the needs of the stakeholders and the difference about their claim and their needs.

So whilst we see another batch of mobile swipe and pay solutions being rolled out whilst there are a few concerns on how that data is processed all over the world, we forget that those out to harm national needs are also out looking into all those apps and finding out that for the largest extent the IMEI number of any smartphone is a much easier anchor to work with and mapping the usage also gives a larger content on data and where the target might be, yet most forgot about how the old is still beneath the new, did they not? So even as we consider the title ‘ASIO warns of ‘hostile intelligence services’ using social media in annual report‘, we need to consider that ‘hostile intelligence services‘ is merely part of a much larger problem and that those services use all kinds of methods that the local knights of the round facilitating table (FBI, MI5, BRGE, AIVD, and MAD) are still not looking at (as far as I can tell).

In all this we were merely given a paragraph and whilst people wonder how to find resources, the matter on how to properly apply those resources so that they can have an impact was left off the table, and that was actually the delicious cream that should have graced the Strawberries, or are those Blackberries? I’ll let you work on that little last line conundrum yourself this weekend.

So have a nice day and let’s not forget that the weekend ends in 48 hours! #JustSaying


Leave a comment

Filed under IT, Media, Military, Politics, Science

It started with a meme

Yes, I ignored the impeachment news for the longest of time, until the act is there, there is no impeachment. Just for the numbers people, this would be the 5th presidential path to impeachment, John Tyler (10) got his overturned 127-83, Richard Nixon (37) resigned before proceedings began and we got Andrew Johnson (17) and Bill Clinton (42) who both did impeached, by the way, I will forever have issues with a girl who keeps a sperm covered dress out of the laundry unless it was intentional the fact that she intentionally kept it for 9 months, and that is all I have to say on that subject. Now we get to the 45th President Donald Trump. When we look beyond the ‘grabbed her by the pussy‘ issues, we see a stage of bad decisions again and again, oh and I am a Republican at heart, so I am not giving you democratic rhetoric.

The first one is his inability to use social media correctly, even if we ignore the grammar issues on covfefe (aka coffee), we see the foundation of a person who apparently states his own frame of mind in all the wrong ways. In addition to this we see his choices on what to tweet, GQ magazine gave us in addition ‘The CIA Reportedly Pulled Its Top Spy From Russia Because Trump Can’t Keep His Mouth Shut‘ (at https://www.gq.com/story/cia-pulled-russia-spy-because-trump), this is actually the very first moment when impeachment became a reality, when an elected official cannot keep proper national security in line, the entire presidency becomes an issue and doubly so when the transgressor of national security is the President himself. Even if he did not do it, the stage of ‘is it more likely than not‘ has been met and for national security that is enough.

Musical chairs with clowns and politicians

The meme did not strike a chord because of John Oliver, even if he is a well-deserved comedian with a critical side towards politics. It was Jon Steward with the 9/11 Victim Compensation Fund bill (at https://www.usatoday.com/story/news/politics/2019/07/29/trump-sign-9-11-victim-compensation-fund-bill-first-responders/1835550001/), where he addressed a nearly empty congress. The idea that congress would not be there to give support to a bill where firefighters knowingly met certain doom is just beyond acceptable, from my point of view; those who were not there should be named and shamed for years to come. It must be mentioned that President Trump signed it into law and that might be the best thing he has done in his presidency.

The impeachment process continues as I get only an hour ago: “House investigators heard from Fiona Hill, the White House’s former top Russia adviser“, the Washington Post also gave us: “Trump renewed his call to unmask the whistleblower whose complaint sparked the impeachment inquiry“, the fact is not that he wants to know the whistle blower, it will be about the materials that the whistle blowers (plural) are bringing. The additional fact that we get: “Gordon Sondland, the U.S. ambassador to the European Union, who is scheduled to appear Thursday under subpoena” that the mess is a lot larger, the mess that hits the media is not a mess that we could avoid, the issue is that this mess should not have existed in the first place. The call from the democrat from Massachusetts is not to be taken lightly: “Rep. Jim McGovern (D-Mass.) shared a link to an article about Cheney’s comments. He argued that within the past week, Trump has “endangered our troops,” “allowed ISIS to regroup,” “abandoned our allies” and “empowered” the leaders of Russia and Syria. McGovern used another name for the Islamic State“, basically his own fat tweeting fingers got him into this mess. The foundation of what a fashion magazine brings (GQ) is the cornerstone for a much larger issue, the fact that the president of the United States of America is the national security issue is something America has (as far as I can tell) never faced before.

It all comes to blows with “Republicans have seized on a ruling that Rep. Matt Gaetz (R-Fla.) cannot participate in Monday’s deposition of Hill as they continue to argue the process should be open to the public“, for those in the dark, watch the movie called the Post, this is a direct stage where Republicans wanted things out of the media, there the issue was: “With help from editor Ben Bradlee, Graham races to catch up with The New York Times to expose a massive cover-up of government secrets that spans three decades and four U.S. presidents“, the Pentagon papers showed levels of folly never before imagined, and there was a need to go public, however, the Pentagon papers was about a stage 4 years after the war, in the end proving that the Johnson Administration “systematically lied, not only to the public but also to Congress” source NY Times. this time it is different, these are events now playing out, even as the Russian news got out AFTER the agent was safe, the fact that the president is part of a national security danger is just too unacceptable and before this goes to the public, the sources must be heard and vetted behind closed doors, I fully agree and I see the wisdom in that, even if the current president and the current administration does not.

I believe this administration made massive errors in the US China trade wars, and even more errors in the entire Huawei ban, the most visible one is that no evidence was ever presented that Huawei is a national security risk, because of the unproven accusations they are wrong, this is different in the UK where the head of MI6 (Alex Younger) gave the clear premise that no government should be dependent on essential infrastructure from foreign suppliers, which does make sense, but then they order their hardware from Finland and Sweden, so there is still some level of issue in place. the entire matter comes to blows in different ways as the larger group of EU nations (Germany being the latest) has kept the doors open for Huawei, now we get to the stage that America feared, Huawei will enable these nations to make faster headway in Europe, expected losses for the US will go between $5 Billion and $8 Billion in the next three years alone. My own expected IP would be available for implementation by Q2 2021 (if Huawei accepts), implying that there will be a boost to the 400 million small business owners outside of the United States, leaving an optional $4 billion out of reach of the US in that time frame alone, the moment my projection is proven values should double, in addition to that the entire telecom service model will change to a larger degree, giving the small business owners a lot more options to choose from, that part is also part of the impeachment.

When the economic models under this administration fail, the democrats will add that entire cart (whether valid or not) to the blame game. Whether we consider this or not, the current president will to some degree be blamed for not being a Guardian of the Economy. The Huawei and China trade pacts are merely one part in this. This administration has pushed the American deficit to the highest in history, even if we accept that the bulk of that failure are the American corporations who became complacent and flaccid, it is more likely than not that the democratic party will voice this in another way. In addition, the guilty of life for Americans have only gotten worse. At present it seems that the current president failed in at least 6 of his 7 roles, as far as I can tell the other impeachment had less on those presidents, we can argue that an adulterer is supposed to lie about those actions, so let’s not go there.

The roles

Chief Diplomat. Failed, the China trade war, I believe that the acts against Iran were justified.

Chief Legislator. Undecided

Party Leader. Failed, his racist tweets are a clear example and they are not the only one.

Chief Executive. Failed, openly hostile to challenges, his manner towards the National Security Advisors as well as his issue with academic opposition makes him a failed chief executive, He used 4 National Security Advisors in ONE term, which is a record as well.

Chief of State. Failed, the G-20 summit, as well as his dealings with the media gives him a fail mark.

Commander in Chief. Failed, the actions in Syria call his military insight and decision making into doubt to the largest degree.

Chief of Guardian of the Economy. Failed, Chinese trade war could have been prevented, outside factors (like iterative corporations merely added to the failure) and of course there were a few fiscal blunders as well.

The entire national security issue, as well as the connections that are being investigated should have sparked impeachment well over a year ago, perhaps the entire CIA matter ended up being the straw that broke the impeachment camel’s back. #Justsaying 

Yet this entire matter is far from over, the Guardian reported: “Donald Trump’s secretary of defense said on Sunday the Pentagon would cooperate with the House’s impeachment inquiry, while cautioning that Trump may try to restrict his disclosure of information“, whilst CNN gives us “Democrats also face extra scrutiny over their strategy as they race to prove that Trump abused his power by seeking election dirt on former Vice President Joe Biden from the President of Ukraine“, the question becomes why focus on strategy? Are the actions valid or not? Can a case be made or not? That is the mother lode of impeachment. Yet the fact that even Republicans are now more and more in support of the Ukraine investigations are making the map of red a hazardous place, it means that not only is there every chance of the next elected president being a Democrat, they have a real chance of winning both congress and the senate in 2020, this would push republicans out of play for 4 years, 4 years on the sidelines with their only option to play interference to some degree.

This was a race with growing chances; the entire impeachment matter merely hastened the shift from red to blue. At present there are numbers giving rise to the chance that the republicans will lose 7 senate seats, with an additional 4 unknowns that could optionally make the next election the biggest loss for Republicans in the Senate since 1936. In that year Democrat Joseph Robinson ended with 74 seats, I am willing to wager my last $1 that there is an option that the Democrats are at present optionally in a position to get 75 seats; it would be a new record. Republican Nebraska has one small advantage as Ben Sasse was openly critical of President Trump, in 1936 they were independent, this time around there is a chance for Chris Janicek to become Senator for the Democrats if he gets the right support, and of course if he plays his cards right.

Impeachment did no start with a meme, but my look at the shift of comedians and politicians did, when national wisdom and honour comes from a man like Jon Steward (never my favourite comedian) we stop and pause to reassess our values and we look at what we hold to be endearing and holy to us, holy values are not religious values, our family tends to be holy, our achievements are enshrined, but the steps we take to enable the next generation (usually our kids) are our step towards holy grace, we all want to leave something behind that lasts and when the clowns are running the asylum (congress) and Donald McDonalds has a large white Kentucky Fried Chicken mansion on Pennsylvania avenue (a little upstream from the FBI building, we see the folly of choices and we tend to demand change, in the case of America it took almost 4 years to figure out the folly beyond the minimum required degree.

When we seriously consider replacing Donald Trump with Jon Steward as President of the United States, at that point we realise that our values need to be restored, and we will elect whoever will give value to the values that truly matter, social media be damned.

I believe that there is a larger need; not merely the separating from church and state, the separation from corporations and state is now becoming a larger imperative, especially with a national debt that at present exceeds $22.8 trillion dollars with absolutely no plan in sight to repay any of it.


Leave a comment

Filed under Law, Media, Military, Politics

One failing director?

It does not happen often, it is actually rare to say the least. When I go back to the one I remember the best (former director Admoni), the ranks of Mossad have been nothing but exercises in excellence. when I think of them I remember the words of Robert Graves regarding General Tiberius (before he became emperor). “Every drill was a war, every war a bloody drill“, It is no different for Mossad, I reckon that Nahum Admoni, Shabtai Shavit, Meir Dagan and Tamir Pardo are perhaps the only men I have truly ever feared. Every security drill a war, every war a drill set to perfection, when the directors of the CIA, MI-6, DGSE, VAJA, FSB and GRU have nightmares, these are the 4 men that they dream about, each of them grilled for war, for subterfuge and all masters of intelligence gathering. Going up against them is like Boris Spassky or Anatoly Karpov offering you a game of chess that is unless you really pissed someone off, at which point it will be a smiling Bobby Fischer facing you. No matter how you slice it, you mess with Mossad at your own peril that is until recently. A case has been out in the open and I cannot fathom how Yossi Cohen left the game this open, and his pieces unprotected and setting them in the optional sunlight of direct peril.

I am talking about the Malka Leifer case. After the entire Catholic Anal Retentive Entertainment case (CARE), as nation after nation went berserk with the Catholic clergy, we now see another mess grow to fruition and even as the anti-Jewish sentiments have never been the fault of Israeli’s, Jews or the state of Israel, the antipathy that the Malka Leifer case is growing could have much larger repercussions. People who have always been open to a larger field of more religions, most of them fathers and mothers who are overly protective of their children; that group is confronted with rage, anger and confusion as we see that her extradition case has dragged on for five years, involved 57 hearings and more than 30 psychiatrists. Now we all heard and most of us can accept a second opinion, yet I feel certain that director Yossi (or director Yoshi when he is playing his Nintendo Switch) has no real explanation why the other 28 psychiatrists were needed, especially as most cases in the IDF get one psychiatrist at the most. So why we see Malka Leifer getting 5 years and 28 additional voices on a setting that could have been decided within 90 days with no more than 4 psychiatrists (two for each side) is a little beyond me.

The Guardian (at https://www.theguardian.com/commentisfree/2019/oct/08/malka-leifers-case-is-shaking-the-australian-jewish-communitys-faith-in-israel) also gives us: “Dassi Erlich and her sisters, Nicole Meyer and Elly Sapper, have mounted a courageous campaign to have her extradited. Their advocacy has given the case a high profile within the local Jewish community“, in light of all this, we see not the case on the law, we see an optional pressure point against the state of Israel that Yoshi could have solved by putting Malka in a drop cloth and delivering her quietly at any Australian airport with a label ‘יהיה לך יום מקסים‘ attached to the package.

In this day and age where observation and deduction is the core stage for Mossad we see: “Leifer’s lawyers claim she suffers from paralysing anxiety and is mentally unfit to face court; yet despite clear-cut video evidence that she is going about her life as normal“, Malka is playing a game that has outreached its timeline and when we consider what she has been and what he is likely to become over the coming year, the case for Mossad is clear. You see, Mossad is responsible to keep the state safe, even as Malka is no danger, she is instilling anti-Israeli sentiments and that is a different matter, in this, as Mossad is by good luck exempt from the Constitutional Laws of the State of Israel, a more secure setting could be reached. In this, as we remember that extradition does not mean execution, it merely means that Malka Leifer has to face a court and a jury in a nation that does not have the death penalty. Can Yossi Cohen sit by and let pressures build that in the end will be poised and aimed at the wrong target? In the end, does Malka Leifer not get what she deserves? Having to personally face those she wronged? Perhaps that is the true fear that Malka faces, the mirror of accountability. It tends to paralyse to fear most people, which is not an acceptable form of defence in the first place, if that were true every taxpayer would get a lifelong reprieve from paying their taxation (that is a lovely idea though).

Yet the non-extradition is also a cloak of protection towards others, as we remember the small part “school management helped spirit her to Israel in 2008“, I feel certain that those so called ‘managers’ must equally be afraid on Malka entering a courtroom and their actions become open to scrutiny, yet that is one part that should not stop Director Cohen, if these managers are willing to do that, what other harm could they propagate? Is that not a valid question? I personally believe that extraditing does not give doubt to the state of Israel, inaction will give doubt, and you merely have to look at the Catholic impact to see that part.

That is when we get to the one debatable part. the quote “there has been an implicit acceptance by the heartland of Australian Jewry that the conflict is intractable, everyone’s hands are dirty and that Israeli governments should not be judged any more harshly than others around the world“, I do not disagree with that sentiment, but in equal matter, the stage of judgement of the inactions by the state of Israel is optionally building weights on the wrong side of the scales for the State of Israel and I believe that there is wisdom of removing all weights that are on the scales that support Israeli opposition, when the scales are set, you want to make sure that the playing field is equal or in favour for the State of Israel and in all this Malka Leifer has become too much of a counterweight to the agenda and needs of the State of Israel.

This should not be allowed to continue as it is.


1 Comment

Filed under Law, Media, Politics

Marketing Deceptive Concepts

We are all in the lane of what is coming; the problem is that what is coming is set on the E40, the longest European highway going from Calais all the way to Kazakhstan (Ridder). So as we depart from Ridder, trying to get to Calais on this AI highway, we need to consider that at present we only got past the first 100 kilometres of a trip that will be 8,000 kilometres long and we are not driving a Aston Martin, not even a Lada, we are traversing this in a 1908 Model T, giving a much clearer indication that this trip will take years (read: a decade at the very least) at best. To be quite honest, as technology goes, we are nowhere near AI, true AI. It will take the largest players (Google & IBM) decades to get to the real AI part, and only when computers become more technically savvy and a lot faster. As such I do not see the reason for people and companies like RACGP to give us: ‘AI is coming to healthcare – and it’s here to help‘, with the quote: “real promise – of artificial intelligence in healthcare“, yet we remain fair. Dr Martin Seneviratne stays faithful when he gives us: “we’re far away from that, to be honest” and he is correct. Yet the stage is there where we see: “In this article we are listing top 15 artificial intelligence apps for android and iOS users“, as well as “an Indian start-up claiming to have built an artificial intelligence-assisted app development platform, is not in fact using AI“. It is all BS (read: Hogwash), there is no such thing as AI, it is theoretical, conceptual at best, the real deal is at least a decade away. It reminds me of some Sales Dumbo I had to deal with on how cloud computing was it bees knees. When I mentioned that there is no thing like a cloud, it is merely someone else’s computer, I was the one who did not comprehend it (in the end I was right, and he (read: it) was not). Yes, I am aware of the ZDNet article (at https://www.zdnet.com/article/stop-saying-the-cloud-is-just-someone-elses-computer-because-its-not/). We get it, it is about scalability and the scale of the cloud is huge, but still, it is a server center that is owned by someone else, and the location of that server is equally important in the data laws we see today. Because the moment China launches its own commercial cloud system, the Americans will ‘suddenly’ come with issues like cloud locations and how the Chinese government can look into every cloud account. I was not belittling anything, merely making sure that we keep focus on terms used (and awareness is often larger than anyone considers). It is the monitoring, hacked data and more important lost data. The cloud comes with all kinds of marketing hypes, but informing on the scope and warning of the dangers that poor passwords bring is often not seen.

So when we get to the Verge where we see: “The company was sued earlier this year by its chief business officer, Robert Holdheim, who claims the company is exaggerating its AI abilities to get the funding it needed to actually work on the technology. According to Holdheim, Duggal “was telling investors that Engineer.ai was 80% done with developing a product that, in truth, he had barely even begun to develop“, we see the larger deception and we also see a lack of actions by governments to a much larger degree, apparently white collar deception is OK in their books.

So when we get back to the RACG (at https://www1.racgp.org.au/newsgp/professional/ai-is-coming-to-healthcare-and-it-s-here-to-help) where we see: “‘Documentation is a constant issue, and so is having a computer separating you and the patient,’ Dr Seneviratne said. ‘The dream of this AI revolution is that it helps with the parts of medicine doctors and patients don’t like, creates a safety net for ensuring quality across the board, and gives clinicians more time to be with their patients.’“, my mind goes back 47 months, 12 days and 14.1 hours (roughly) when I designed the concept of what could be the Google Tome (I concluded that the iTome could never become a reality in an technological iterative pushed corporation), a device that would take case of part of it and help the UK NHS to get a handle on their paper mess and red tape. The device would also be a great solution for places like Scandinavia where the rural population is all over the place. There was one tiny setback, it required 5G, it was the only way to get it to work to the degree it did and 5G was nowhere near ready to the stage that places like the NHS, GP’s and clinics could be upgraded. We are still 1-2 years away, but the Google Tome would be a game changer as it worked on a very different IP. Apple would take a decently large hit as I remembered some original parts from before the PowerMac and Apple actually had the inside track, with today’s iPad they could have ruled, but in the last two years they became a mere iterative needy toddler, taking them out of the game. both IBM and Huawei are not ready for this leap giving Google an actual first position with no chance of any number two catching up for close to half a decade. My solution was not AI based, it was based on the realistic foundation of NHS administrations and to see where the obstructions were. Instead of making some political never working one system (UK Parliament spend £11.2 billion learning that it did not work), my path was to upgrade all the elements and give a new definition to speed, not the one that is founded, for downloading, but a new on access protocol that emphasises on security and data safety. In fact, the results would in theory get to the right physician 30%-60% faster. Anyone who waited for results in an NHS location can tell you what a game changer that is.

And none of this touches the 5G IP I created three years later.

But that is not what it is about, it is about the marketing ploys we are confronted with and for the most, the media greedily uses that hyped term to get traction with people, clicks and awareness, the information is less and less a concern to the larger group of media (or so it seems). The one that I got confronted with yesterday is the one that set it off. A friend (Tom Breur) wrote an excellent piece regarding Data Democracy (at https://tombreur.wordpress.com/2019/08/13/what-does-data-democracy-stand-for/). Yet in data, as I personally see it, there is no real democracy, it can be dictatorial, it can be feudal, it can even be tyrannical, but it is never democratic, you do not get a vote in that hierarchy, that is the way with data and it is the researcher who can redefine you through giving you a weight of 1 (or lower) or disregard you as inconsequential as grouping you with other user missing points of non interest. The respondent never had a voice in the matter negating the entire democracy part.

This setting was most likely started by media with their claims of “Big data’s threat to democracy becoming global problem“, and there the delusion started. Big data is never about democracy and democracy is not about data, it is about applied wisdom, they do not correlate and are even less likely one and the same. It becomes even more entertaining when we (at https://morningstaronline.co.uk/article/labour-will-ban-big-money-buying-democracy) see: “Labour will ban big money from ‘buying up democracy’“, it is entertaining and hilarious as this has been happening well over a century, long before there was a silicon based economy (not talking about boobies here). When we get: “Last November Mr Johnson was flown to New York and was paid £94,507.85 for a two-hour speech at the multibillion-dollar hedge fund company Golden Tree Asset Management“, we can argue that he was merely doing a job he was allowed to do, and that is not impeding democracy, is it? And when we see: “We are funded by workers through their trade unions and small donations, averaging just £22 in the last general election“, how much support did you give the people who voted for UK Labour without a donation? And when we see the Washington Post give us: “Data shows that an overwhelming majority of Africans believe that democracy remains the best form of government“, I might not disagree with that, yet the issue is not agreeing and disagreeing, it is the deceptive model of awareness creation that big business allows for when they buy the identities on Facebook by millions and target them with political advertisement. Even as Senators like Ron Wyden are calling to ban that, he knows he is fighting a lost war. Also, as a member of the Senate Intelligence Committee, he is watching proven CIA tactics being deployed via Facebook and he knows how efficient those can be, it is a game only the rich can play. He even hides behind “I’d rather have them do it voluntarily than requiring a law“, because there is no way that they can pass that law in time and even then there will be a dozen loopholes to circumvent the law passed via the first amendment.

It is all due to the marketing we allowed from the very beginning. there was no stop to the media, the hold on awareness versus deceptive is sketchy at best and now that there is a whole slew of iterations coming forward we see more and more deceptive conduct, yet nothing is done, there are attempts, but they are feeble at best. That evidence is seen when we consider Engineer.ai and its founder & CEO, Sachin Dev Duggal. We see the news in the Wall Street Journal as well as the Verge, yet less than 3 days ago that person won the Serial Entrepreneur award, so it seems that the players are all OK with deceptive conduct. Yet I remain optimistic, I merely have to wait to see this blow up in the faces of those sales driven CEO’s and VP’s to see that their failure gave them months of reprieve and every documented event merely sets the stage for my IP in a much more powerful way.

We need to consider that when it comes to creating awareness, the media is still accountable to shareholders, stake holders and advertisers, as such there are a lot of issues in the IT field, personally in light of recent events the do’s and don’ts of Sachin Dev Duggal take the cake. Don’t take my word for it, merely look at the Wall Street Journal (at https://www.wsj.com/articles/ai-startup-boom-raises-questions-of-exaggerated-tech-savvy-11565775004) and consider how the award two days later was still handed to Sachin Dev Duggal. Even as the man ‘hides’ behind ‘human-assisted AI‘, and when we look at the quote: “it uses artificial-intelligence technology to largely automate the development of mobile apps, but several current and former employees say the company exaggerates its AI capabilities to attract customers and investors“, we need to ask a whole range of questions, none of those are found anywhere. I am not raining on the man’s parade, but clearly no one else is either. I wonder how many righteous participators at that entrepreneurial award feel left out in the cold, a fair question if I say so.

I merely look at the marketing part of it all, when I look into the direct impact, that some marketing hypes are giving us, I tend to wonder if the need was really awareness, or confusion that was behind the creation of the hype. It is sad but that is more and more often the need to wonder when any form of media gets involved.

It is a sad evolution in the age of information as it has been for some time now.


Leave a comment

Filed under Finance, IT, Media, Politics, Science

Government? Censorship?

We see it, we ignore it and others remain in denial. We are censored almost every day and we remain unaware. You see, the issue is not advocated as censorship. It is presented as filtered news, and it is not the same. As we looked Yesterday into the events surrounding Evgeny Lebedev, we see people like Jeremy Wright hiding behind “may have an effect on the Evening Standard and the Independent’s news agendas“, yet to what degree and in what direction, that part was not given, was it? In addition we were introduced to Nicky Morgan and the fact that this is now on her plate. Yet the issue of censorship is still here.

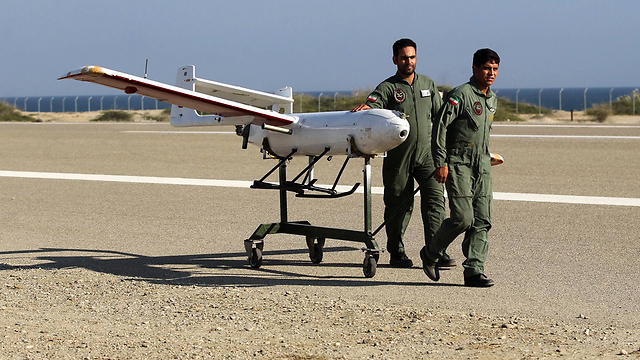
Bloomberg gave us: ‘Saudi Oil Plant Attacked by Drones‘ (at https://www.bloomberg.com/news/articles/2019-08-17/saudi-oil-plant-attacked-by-drones-but-production-unaffected) 11 hours ago. We also get: “Yemen’s Houthi rebel leader Abdul Malik al-Houthi claimed responsibility for the attack in a televised speech which was aired via the rebel-held Saba news agency. The Houthi leader said the group launched the assault on the oil and gas facilities with 10 drones. This was done to deliver an “important message” to the members of the Saudi-led coalition in Yemen, he said” yet no one is giving any explanation how Yemeni Houthi fighters got access to high end drones. 10 drones represent a significant investment, the Houthi forces have neither the funds nor infrastructure to acquire or built them, yet they are delivered, where from?

An attack that might be seen as a terrorist attack and the exposure is close to nil. We get the news from Arab News, from Al Jazeera. Yet the event that happened 11 hours ago, is still not covered by the BBC. They limited the Middle Eat page to the US Warrant to an Iranian oil tanker, then the news on ‘Rashida Tlaib rejects Israel’s offer of ‘humanitarian’ visit‘, which is a day old, the rest is 2 days old, or even older. That is the BBC now! We do see some news from Reuters and Haaretz, yet nothing from the other UK papers. Is that not weird? Is it so weird that Saudi Arabia wants to see more on the attacks on them? The UK is facing massive censorship and has been under censor’s scrutiny, yet the UK remains silent.

We see a little more when we face Al Jazeera who gives us “A Houthi military spokesman said earlier on Saturday that the group targeted the Shaybah oil field with 10 drones in what he said was the “biggest attack in the depths” of the kingdom, the world’s top oil exporter” in the article (at https://www.aljazeera.com/news/middleeast/2019/08/drone-attack-yemen-rebels-sparks-fire-saudi-oil-field-190817132916661.html). The other non-given issue is that the Shaybah facility is really close to the UAE borders. A lot of issues remain, but the media to a much larger extent has decided to silence the news, they have decided to be Anti-Saudi Arabia. The fact that Houthi terrorist forces are sending drones into Saudi Arabia, drones that they cannot build and drones that require hardware that they do not have, cannot create and optionally cannot operate is a much larger issue, but the UK media remains silent on it. How weird is that? So here we see a direct first part where it makes perfect sense to be in a stage where they have an invested interest in newspapers that might now give voice to what is going on. If the UK really wanted an independent press, the people in the UK would have been given the complete story on Houthi forces and the exposure of Iranian funding would be out in the open, that is not the case and we should all wonder why that is happening. Oh, and I understand that there is more news in the world, I understand that there is only so much on what an journalist can achieve, yet a middle eastern section on the BBC with two articles from the last TWO days and the rest is older is a little too weird for words. The fact that this was an attack on Aramco with the linked fact that we see loads on Aramco, but the entire mess of the attack (and lack of results from the attack) is not shown in the Financial Times, or the Guardian, who was willing to report only a little under 6 days ago ‘Saudi Aramco ready for record $2tn IPO after first-half results‘ gives rise to censorship and one sided reporting. So when exactly did we find that acceptable from any independent news force? The numbers and the events do not add up.

Even the Deutsche Welle gives us (at https://www.dw.com/en/yemen-houthi-rebels-target-saudi-oil-field/a-50066244) “This is the second such attack on the Saudi energy industry in recent days and comes amid high Middle East tensions” Really? the second attack? When was the first and why do I see almost nothing on that, and basically nothing from the Western European Newsgroups? There is even more, the quote “The Saudi acknowledgement of the attack came hours after Yahia Sarie, a military spokesman for the Houthis, issued a video statement claiming the rebels launched 10 bomb-laden drones targeting the field in their “biggest-ever” operation” gives rise to all kinds of intelligence issues, the fact that certain players are leaving this in the shadow of their desk is a larger issue. It gives rise to the accusation that the CIA is still on goal to keep stability in the Middle East to a minimum. The fact that we see the (optionally boasted) claim ‘their “biggest-ever” operation‘, whilst Yemen has no infrastructure to do this, I personally doubt that they have the knowledge to fly these drones to their target, all issues involving Iranian support, optionally via Hezbollah, all ignored and all non-reported.

That is not merely censorship that is the stage of filtering events on the world stage and keeping them out of sight all together. Is this the EU play to keep news away so that they can have some empty nuclear deal afloat? All hiding behind some INSTEX tool (Instrument in Support of Trade Exchanges), whilst none of it brings any revenue or actual trade, there is no positive side and when we investigate the Iranian events towards the Houthi forces in support of attacking Saudi Arabia, we see a diminished setting, yet the EU is still hiding behind the nuclear deal that was never a deal in the first place. And now we can optionally add the news filtering that Saudi Arabia is facing. All is not well and a lot of it is about to get worse, all for the simple reason that some people are asking questions now and a lot more will be doing so soon enough, at that point any election falls into the water in a stage where the UK government has only the spin tour of the next election to rely on and in addition the media will feel the pain too. When the people realise that there is no longer an independent press. It went out of the window when politicians decided to ignore the Leveson report to the largest degree. They made their own bed, enjoy the nightmare it brings.


1 Comment

Filed under Media, Military, Politics

Exposing lies?

We are confronted with lies all the time, the CIA (who is truly gifted in the act) uses it to spread all kinds of discourse, but that is their operandus mondi, so we are not surprised. Yet now we are confronted that these tactics have been embraced by both the FBI and the Pentagon. And it is not my source; it is an American source that gives us this part.

To get to the heart of the matter, we will have to borrow a TARDIS and do some time-travel (a valid Dr Who reference). During this trip we will not be looking at apples and oranges, but we will be investigating fruit, and this has all the bearings on the case.

Trip one

Let’s travel back to November 24th, 2014. It is a sunny day at Sony Square New York, 21 degrees, nice and relaxing weather. It had all the marks of it being a lovely day, were it not that someone decided to hack Sony and they did it, not only did they do it, they left all the markers blaming North Korea. The FBI send their cyber experts and behold, they too agreed that it was North Korea. Even as we were extremely aware that they had no way of doing it, the FBI stood firm on their findings.

Trip two

We are pushing the envelope and stopping at 2015, 2016, 2017 and 2018. We are given “North Korea’s offensive cyber capabilities” and we see Randall Schriver, a top Pentagon official and all the ‘so called’ expressionistic ideas on how North Korea is the big nasty, the large danger and the big hacker. In addition to this the Financial times gives us (at https://www.ft.com/content/cbb28ab8-8ce9-11e9-a24d-b42f641eca37) “Pyongyang controls an army of thousands of hackers who bring in hundreds of millions of dollars annually, according to experts’ estimates“, which was given to us in June 2019.

Into the Heart of Darkness

It was only hours ago that we were given the first light of truth by the Washington Post. To give you that we need to change the topic to fruit and not apples or oranges. You might realise that to get ahead, you need to be ahead. Unless you build a system yourself, you need access to a system of equal quality to hack into a place. Unless you have the passcodes (current password = Inc0rrect%) and inner workings, you cannot hack past the Pentagon Cray, it is close to impossible to do with even the most updated equipment and North Korea is well over a decade behind. It is defended by firewalls and other encrypted matters. Sony is not that advanced, yet still has a lovely set of firewalls and other means to limit access. Yet North Korea, with technology that was considered advanced in 1990, was nothing of the sort a decade before they hacked Sony. In addition, certain access methods or planting of other abilities would have required 4G mastery, a mastery that they do not have. The digital footprint does not match up and it is there that the Washington Post (at https://www.washingtonpost.com/world/national-security/leaked-documents-reveal-huaweis-secret-operations-to-build-north-koreas-wireless-network/2019/07/22/583430fe-8d12-11e9-adf3-f70f78c156e8_story.html) is giving us the goods.

So as we are given: “Before 2008, North Korea struggled to find multinational companies willing to build a 3G network in such a risky business environment. That ended with the creation of the wireless provider Koryolink, which emerged from a discreet visit in 2006 by Kim’s father, Kim Jong Il, to Huawei’s headquarters in Shenzhen, China” this is the first piece of evidence, 6 years before the hack North Korea did not have access to 3G, it was not there, as such the knowhow of hacking would have been severely limited. In addition to this we need to consider “Alexandre Mansourov, an adjunct professor at Georgetown University’s School of Foreign Service, who in 2011 wrote about North Korea’s digital transformation. “They decided to work with Huawei from that time on.”” gives us that in 3 years that stage was not surpassed, or even achieved. The paper by Mansourov also gives: “less than 3 percent of the population currently use modern telecommunication services, it has adequately trained human capital, a rather developed industrial and technological base, and sufficient financial resources to pursue the digital revolution to the benefit of the majority“, which now implies that the fall back is actually a lot larger. If they truly had a ‘rather developed industrial and technological base‘, then they would be the oranges that need not rely on Huawei, yet they are technologically speaking merely apples, they are both fruit, but on a different shelf, a lower shelf and that is where we see the technology fail (especially in North Korea). In his paper we also see: “Because the cell phones connect to Chinese cell phone towers it is difficult for the North Korean government to eavesdrop on the calls, but it does mean use is restricted to the border area“, this implies that the limitations in North Korea are actually larger and as such knowledge is more limited. that last part came from ““How Chinese Cell Phones Help Information Flow,” Martyn Williams, 1 April 2010” which was 4 years before the hack, there is no way for any nation to evolve their technology level in that amount of time without having billions, as well as all the technology available for installation and implementation. Which was never the case, North Korea is hardly on the 3G path keeping them a decade behind everyone else.

Fruit, Apples and Oranges

So even if I am looking at fruit, looking at mobile technology versus hackers is like setting apples against oranges, yet the larger truth remains, a hacker cannot surpass certain levels of access if they lack access to the current generation of technology and that is where we see the flaw in all this. To have antiquated equipment access the Sony mainframe calls for all kind of issues as the access requires speed, and if you rely on old technology there is a limit to what you can get. For example getting a 4TB drive for a PlayStation 3 is bogus as it cannot address the complete drive, so when you look at it from that path, you lack the ability to store all that data and Sony was all about data. More important, if the skill to get behind a 4G system is not there, there was not even 3G, how can you get into the hack? Now we might rely on normal lines, but the flaw is already shown, you need a larger comprehension of technology and telecommunication to proceed and North Korea is stated that it could not get 3G without Huawei; at that point we should recognise that it could not get into Sony. If they actually had done that, then they would have been able to design and build their own 4G (which would still be half a decade too late), but that would be the premise. That absence gives us that the Washington Post, who also gives us: “According to a 2008 contract, Panda would transport Huawei equipment to Dandong, a town in northeastern China known for cross-border trade. From there, it would be taken by rail into Pyongyang“, as well as “In spring 2008, Orascom and Korea Post tasked Huawei with developing an encryption protocol for the network, noting that the government would create its own encryption algorithm, according to the documents” this much larger stage does not absolve Huawei (it is not about that), but the fact that encryption protocols were not in existence implies a delay of at least 2-3 years to get their 3G up and running, the entire matter would have given North Korea less than 2 years to get trained to the levels required to visit the Sony Server and become an actual cyber threat. There is no realistic chance that this would be the case and again, when we consider the press visit to North Korea (somewhere in 2012) where the Dutch press learned that their high ranking escorts had no idea of what a smartphone was, that alone gives a lot more insight in the technological limitations of North Korea and its army.

There is no doubt that North Korea would love to be an actual threat, but when it cannot comprehend 3G to the degree it needs and it has no 4G, how is North Korea an actual threat? I believe that Sony was hacked by someone else, there is also enough valid intelligence to see that those people would love to do business with North Korea, yet the entire matter connected to Huawei implies that North Korea is missing several links on the chain of telecom cleverness, the reigns of the horse of innovation and the armour of progress is all rusty, heavy and useless. In this stage the North Korean cavalry might be the most advanced they had but it still does not match up what other nations have had access to from the late 1800 onwards, when you realise the difference to that degree, do you still believe that North Korea could have been the hackers?

That is seen when we look at ‘The Hill’ in 2017. There we get North Korea and the quote: “Today, when warfare can include the operational use of nuclear weapons, the cumulative consequences of underestimating “friction” could be exponentially more serious. This conclusion is true by definition and thus, thoroughly incontestable” yet when we see in a 4G world that North Korea has not even mastered 3G to the degree it needs, we see a shift of needs, needs that are all about the consultants charging their overexposed ego’s by the hour, whilst we see a lack of evidence on the abilities towards the dangers that we are seemingly exposed to. In that regard the FBI and the pentagon has played into the hands towards consultants like Randall Schriver, yet the actual evidence (implied to be) as we now see in the Washington Post gives us another picture, one that bounces against earlier accusations and speculations. March 27th, 2019 C-Span gives us the premise that China and North Korea are set together as a threat, yet the overbearing accepted evidence shows that the division sets the stage where China is 99% the threat and North Korea a mere 1%, yet together is nice to bump the budget. So far no actual or factual evidence has been shown where North Korea is an actual cyber power. As I personally see it, even the NY Times is in on it.

When we are given: “Their track record is mixed, but North Korea’s army of more than 6,000 hackers is undeniably persistent, and undeniably improving, according to American and British security officials who have traced these attacks and others back to the North“, as well as “North Korean hackers tried to steal $1 billion from the New York Federal Reserve last year, only a spelling error stopped them“, and “only sheer luck enabled a 22-year-old British hacker to defuse the biggest North Korean cyber-attack to date“. when we are confronted with ‘spelling error‘ and ‘sheer luck‘ we are sold a bag of goods, the fact that North Korea is at the most about 3G, we see the lack of certain abilities. If these hackers were that good, than their abilities would have been to acquire all the technology that we have full access to and that has seemingly not happened. In any war we acquire the weapons to be an equal footing, or more advanced footing, von Clausewitz and Sun Tzu taught us that. You do not rely on the flintlock when the opposition is walking with a 7.62mm MAG. The accusation (also from the NY Times) “the country is suspected of having thousands of hackers capable of carrying out global cyber-attacks, like the recent ransomware attack in more than 150 countries” gives us that they are a large threat and this is only possible with a large established infrastructure. That is seemingly not the case so as we ponder ‘suspected‘ we see the speculated inflated danger that North Korea is, and until today, until the Washington Post gave us the article, that part was too eagerly accepted.

There is no doubt that there are hackers in North Korea, but as the technology shows, they are fighting with one hand on the back wearing a blindfold. It does not make them less dangerous, but it also implies that the events that have taken place were done by others and as such the cyber operatives trying to stop it are not merely failing, they are at present completely unaware who they are actually up against and that is the sad part of this story. after all the billions they got they are still clueless in the dark, a sad story that only came to light as the Washington Post gave us: ‘Leaked documents reveal Huawei’s secret operations to build North Korea’s wireless network‘, seemingly a 3G network no less. And even there we have no evidence at present. That part is given through: “Since then, any company to provide Panda with telecom items intended for North Korea and containing at least 10 percent U.S.-origin content without a license would be in violation of the export ban”, so not only is there a question on one side, the lack of evidence at present gives rise to a lot more issues and that makes for such a sad situation at present.


Leave a comment

Filed under Uncategorized

Simple Complexity

Less than 24 hours after we looked at Iran getting ts fingers on a ship with too many unknown variables (like Owner, origin and so on), we see them fall into their old habits by grabbing two tankers with British links. The article (at https://www.theguardian.com/world/2019/jul/19/british-tanker-iran-capture-fears-stena-impero-uk-ship-latest) gives us plenty to consider. And when we are exposed to the quote: “Iran’s Revolutionary Guard claimed to have taken the British-flagged Stena Impero into port with its 23-strong crew, and Iranian officials claimed it had infringed maritime regulations” er see the first play in a larger game. The first question we get is likely to be ‘how did it infringe maritime regulations?‘ Yet that is not what this is about. And whilst we look at both ships, all whilst for the second one we get: “The Mesdar’s Glasgow-based operator, Norbulk Shipping UK, confirmed that the vessel had been boarded by armed guards but had then been allowed to continue its voyage. “All crew are safe and well,”” we now get a new scene, one you might not have considered.

The idea hit me in the early morning 8 minutes after the first tanker (who is still missing on Iranian grounds) message came to me. The thought:

‘If you cannot fathom the simplicity of complexity where will you remain?‘

You see, most people want you to believe that they are opposites; we see studies that are about understanding the relationship between simplicity and complexity. It is not that, no matter how complex an equation, it must adhere to the simplest of rules. When we go back to the foundation of programming, some might recall one of the oldest lessons. Any program consists at the most of sequences, selections and loops. Once you get that, the simplicity of complexion becomes a point of focus. The entire Iranian matter is not about the Gibraltar tanker (although it will be voiced as such), it is only partially about pushing the opponents. In its current state it is to prove that the US and Europe are basically pussies, they will try to do whatever they can except start the war, that what this is about. All the big words that we got from the man and his administration are starting to become null and void. Even now we see: ‘Trump Says He’ll Work with U.K. on Response to Tanker Seizure‘, we also get: ‘Trump confirms he authorized Rand Paul to negotiate with Iran‘, it is all about ‘reducing’ tensions.

So at present Game, Set and Match for Iran.

This is about sending a message to the Kingdom of Saudi Arabia and the State of Israel that they stand alone, it was a simple play and the media remains clueless, merely reporting the voices and not seeing the orchestra play. It is like watching Wagner (at https://www.youtube.com/watch?v=3ZP-yXsNV2E) with the sound muted, we see the dance, we see the subtitles, yet without the music the play makes little sense. That is what the media enabled in all this. Iran is playing the game a lot better than I expected them to play. There is at present a 20% chance that Europe will find some excuse to let the tanker go to Syria, yet the tanker will not be empty, it might be reduce, or what the media will quote as ‘nearly empty’, yet an oil tanker optionally holds more than oil.

And even as the Guardian gives its readers the quote: “Jeremy Hunt, the UK foreign secretary, told Sky News: “We are absolutely clear that, if this situation is not resolved quickly, there will be serious consequences.”” there will be a debate and we will find the ‘serious consequences’ laughable in the end. A second message that the support to Saudi Arabia will be scaled back. I have no idea how King Salman bin Abdulaziz Al Saud could ever see these two players as actual allies. So far they have folded at close to the first time of pressure. Consider the evolution of the events and place them next to a phone call made 20 hours ago: “Iran’s President Hassan Rouhani urged Europe on Thursday to speed up efforts to salvage the 2015 nuclear deal, during a phone call with French President Emmanual Macron“, consider that the tanker was already clearly on route to be intercepted, consider the timeline of events and the complexity becomes a simple equation, Iran is playing a multifaceted game to show its enemy the Kingdom of Saudi Arabia that it has no western friends, it has no western allies and so far the US the UK and the EU states have been playing their part in musical chairs exactly as Iran hoped. We can see Senator Rand Paul the Republican from Kentucky as evidence in that game. Even the Washington Post is giving part of my view a few hours ago with: “Resetting the U.S.-Saudi relationship on a more honest basis is urgent now, as the danger of regional conflict grows. The latest sharp escalation came Friday as Iran seized a British tanker in the Gulf, according to a U.S. official. This provocation makes British and probably American retaliation likely — compounding the crisis further, which seems to be Iran’s goal.” (at https://www.washingtonpost.com/opinions/global-opinions/saudi-arabias-leader-must-reset-his-relationship-with-the-us-as-iran-tensions-soar/2019/07/19/10cd6c0c-aa46-11e9-86dd-d7f0e60391e9_story.html), they call it resetting, I think they are creating a distance between themselves and the KSA, a bad escalation, Iran seems to have its tactic in place and even as we see the stage given as “demonstrate accountability by prosecuting Saud al-Qahtani” on the death of a journalist no one cares about, that part is proven with the inaction on Journalists kept in Turkish prisons, its flim flam theatrics that are collapsing on itself. It is a media circus propelled through UN essay writer Agnes Callamard, a stage of issues lacking actual evidence, only assumptions, circumstantial evidence at best and all trying to influx circumstance by adding the CIA report of ‘high confidence’ again not evidence.

Iran saw it for what it was, an option to push and not get any pushes back, pushing until Europe (holding a nuclear deal carrot) and America (sending Senator Paul) fold in their contributions towards the Kingdom of Saudi Arabia. I expect that at that point the Iranian attacks will intensify via both Yemen and through Hezbollah. If I am 100% correct these attacks will start again no later than August 4th, or more likely within 1-2 days after some form of agreement with Europe and America has been reached. At that point Israel will have to get very careful on their actions because all bets will be off and Europe is unlikely to do anything operational they will merely leave Israel to their own devices, there is less certainty with the US, but Iran will not care about that part in the short term.

To be honest I fear that August will be a stressed month to be certain, to what degree is not known, because it will depend on what actual orders Senator Paul has at present. I have not forgotten about the US troops, but overall, their mission statement was not given to the media, was it? We get ‘hosting U.S. troops to enhance regional security‘, yet that does not mean that they have any operational value at present . The quote I found was: “USMTM’s mission is to advise and assist the Saudi Arabian armed forces through security cooperation efforts in developing, training and sustaining capable deterrent and self-defence forces for Saudi Arabia in order to facilitate regional security“, so basically these people are consultants and trainers, which is fine, yet when the regional security is threatened, will they act in defence, or only act in self-defence? When you remember the issues that the MFO could have faced in 1982/1983, that setting is rather important. And if Iran changes the premise with their actions, how useful will these US troops be?

These are valid and important questions and the media pushed away from these parts to the largest degree. As far as I can tell, this is an evolving game of chicken with Iran walking around wearing a white table sheet saying ‘Boo!‘

The fact that both US and Europe Jumped is cause for worry (the European ministers are actually scrambling) which is a worry to the degree that we are watching a paper tiger with its teeth and claws yanked, it looks nice but in the end its a rather pointless and powerless presentation.


Leave a comment

Filed under Media, Military, Politics

Analyzing Intelligence

What is given to us is behind a veil, we accept that and at times we accept that the media does not give us everything. It is however weird when the change is slightly larger than we expected and in a direction we did not see coming.

This all started almost three days ago when Iran ended up with a tanker, the news (several sources) gave us: “Tracking data shows an oil tanker based in the United Arab Emirates traveling through the Strait of Hormuz drifted off into Iranian waters and stopped transmitting its location over two days ago, raising concerns Tuesday about its status amid heightened tensions between Iran and the U.S.” we all have issues and we all thought about the big bad Iranian doing things that are unacceptable. In light of everything that happened, this is a fair point of view to have (you know that Iranian tanker in Gibraltar).

Yet now, CNN gives us (at https://edition.cnn.com/2019/07/18/middleeast/iran-tanker-intl/index.html) “Iran has seized an oil tanker it claimed was carrying 1 million litres of “smuggled fuel,” state news agency Press TV said on Thursday, before later releasing a video purporting to show the tanker.” we all want to think the worst of Iran (still a valid point of thought), yet that premise changes when we also get the following quotes: “US intelligence have been investigating what happened to the Panamanian-flagged tanker M/T RIAH. The ship-tracking website Marine Vessel Traffic has not had a current location for the tanker since July 7“, as well as “It remains unclear who owns the ship. While the initial US intelligence suggested that the tanker was UAE-owned, the United Arab Emirates has said that the tanker in question was “neither owned nor operated by the UAE. It does not carry Emirati personnel, and did not emit a distress call,” according to state-run WAM”

And now we have an actual problem

To begin with, with all the digital options, and registries we get: ‘It remains unclear who owns the ship‘ are you flipping kidding me? In a time when both the Sea of Dammam, as well as the Strait of Hormuz are an absolute tinderbox, you have no idea what is going in and out of that place, you cannot tell who owns a million litre tanker? This is not some $27,000 Glastron poaching lobsters, too small to be seen by radar, this is a piece of metal the size of 500 40 feet containers this puppy is really visible! So not only does it imply the incompetence of the CIA, it shows that there is a larger facilitation at play.

When we consider the political and intelligence pressures in the Middle East as they are presently presented; the quote: ‘The ship-tracking website Marine Vessel Traffic has not had a current location for the tanker since July 7‘ reads like an absolute joke. When we consider intelligence pressure, the CIA, DGSE, MI-6 and optionally Mossad should have had an alert within 24 hours that any tanker vanishes. More important depending on where that happened red flags should have been raised all over the place and now that we see: “US intelligence suggested that the tanker was UAE-owned, the United Arab Emirates has said that the tanker in question was “neither owned nor operated by the UAE. It does not carry Emirati personnel, and did not emit a distress call” we see a much larger failing. There are programs in place to check ships registries, there are systems that can check the moment any blip is added or removed on the website Marine Vessel Traffic (and several places alike), in addition the fact that the UAE now gives us that an apparent UAE ship is not and neither does it have UAE staff is a failing on several fronts. I personally wonder what excuse Lloyds registry gives us soon enough. We cannot fault them for not being aware of facts, but the fact that a ship of this size cannot be identified as being owned is a failing, it is a tactical one to a much larger degree.

Overreacting much?

Is it? when we see the attacks in Yemen and other places, we see a tanker that could do massive damage to any harbour and for 9 days we had no clue that something was wrong, perhaps we did not care, but consider that a tanker like this could destroy in several ways a harbour and the environment in either Iran, Saudi Arabia, Kuwait, Bahrain, Qatar or the UAE, yes that is a large issue. A floating fuel bomb (a slight exaggeration) with one million litres of oil is a large issue. At the top of my head, Dubai, Abu Dhabi, Doha, Riffa, Manama, Dammam, Kuwait city, as well as several Iranian villages, any of them could have been a target leaving any of these places in ruins for at least a decade. So yes, the intelligence community failed, moreover, at present with the presented awareness the IRGC did nothing wrong. The fact that in opposition the stage where US intelligence has nothing credible to offer is a larger failing still (yes more to come).

You are who?

When we consider that awareness of Panamanian-flagged oil tanker MT Riah could have been found in minutes is one part, the fact that the implied owner UAE is not gives us a larger doubt on intelligence data. Now data is dependent on vetting and checks and we cannot check it all, yet when we consider the registry, the owner was someone, who is not implies it was sold, so basically 40 hours ago, that part could have been verified and none of that seems to be the case (or it is classified beyond my eyes, which is weird, right?)

So for no less than 35 hours certain escalations seem to have been the case and CNN ignored that part, which might be a valid embargo, these things happen, yet the global news is propagating facts that are not and facts that are nowhere and none of it has any validation. This now sets a larger stage, in the eyes of the world Iran did nothing wrong (which does actually happen), but this floating tinderbox should have received a lot more visibility with credible and verified data, which is not the case and a lot of missing data in the last 24 hours ago implies that there is a path and that path is about something we are not informed on (which is still valid and credible) but in light of the fact that only 5 hours ago Reuters merely mulls data that has been known for well over 36 hours implies that there is a larger play and for whatever reason we see the absence of awareness by the news and those claiming to inform us leave us with the stage of “Iranian state TV aired footage of a vessel called “RIAH” that it said was seized by Iran’s elite Revolutionary Guards for smuggling fuel” and was all they gave us 5 hours ago, whilst I gave a dedicated list of actions that could have been followed up on by actual journalists in the three minutes it took me to digest the data available. Is that not weird?

It gets to be worse

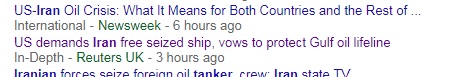
That is seen when we look at UK Reuters. We search of all news gives us: ‘US demands Iran free seized ship, vows to protect Gulf oil lifeline, In-Depth-Reuters UK‘ a mere three hours ago, yet the article it links to is all about ‘U.S. says Navy ship ‘destroyed’ Iranian drone in Gulf‘, something here does not belong, this is not a simple error and Reuters does not usually make these kinds of blunders, this is about something more and even as we all want to point fingers at Iran, we now have a larger stage and the US loss of credibility (that famous silver suitcase) gives us more to worry about, this is a set stage of pushing awareness and whilst the Europeans are all about saving a nuclear deal and the fact that (what I predicted) the surpassed transgressions of Iran on nuclear terms are now trivialised imply that there is a theatre going on, I merely wonder who the players are an which government ends up playing the court jester.

We might think about trivialising the entire matter, but consider that the ship optionally was smuggling merely $250K in crude oil, someone is not really getting rich, not in the larger scheme of things, so what was this actually about? Is it not interesting on how the media is not all over this, especially as it could escalate gulf pressures to a much larger degree?


Leave a comment

Filed under Finance, Media, Military, Politics

Iranian puppets

Saudi Arabia has been under attack for a while, yet the latest one has been the hardest hit for now. 26 people were injured in a drone attack on Abha Airport. The fact that it is 107 Km away from the border gives rise that this is not the end. Even as we see: “a late-night cruise missile attack by Houthi rebel fighters”, I wonder if they were really Houthi or members of Hezbollah calling themselves Houthi. In addition, when we see: “the missile directed at the airport had been supplied by Iran, even claiming Iranian experts were present at the missile’s launch” as the Saudi government stated this, I am not 100% convinced. The supply yes, the presence is another matter. There is pretty hard evidence that Iran has been supplying drone technology to Lebanon and they have been training Hezbollah forces. I think this is a first of several operations where we see Hezbollah paying the invoice from Iran by being operationally active as a proxy for Iran. It does not make Iran innocence, it does change the picture. the claim by Washington “Iran is directing the increasingly sophisticated Houthi attacks deep into Saudi territory” is more accurate as I see it. It changes the premise as well as the actions required. From my point of view, we merely need to be able to strike at one team, if anyone is found to be Lebanese, Saudi Arabia can change the premise by using Hezbollah goods and strike Beirut – Rafic Hariri International Airport with alternative hardware. Lebanon stops being the least volatile country in the Middle East and it would stop commerce and a few other options at the same time. I wonder how much support they get from Iran at that point. I believe in the old operational premise to victory

Segregation, isolation, and assassination, the tactical premise in three parts that is nice and all solving; It can be directed at a person, a location, or even an infrastructure, the premise matters. It is time to stop Hezbollah, that part is essential as it does more than merely slow down Houthi rebels, it pushes for Iran to go all in whilst being the visible transgressor, or it forces them to back off completely; that is how I personally see it.

So as we see the Pentagon rally behind diplomatic forces, I cannot help but wonder how it is possible for 15 dicks to be pussies? For the non-insiders, it is comprised of the 7 joint chiefs of staff, the septet of intelligence (Army, Navy, Air force, Marine, FBI, CIA and NSA) and of course the National Security Advisor. It is time to change the premise, it really is. It is also a must to proclaim ourselves to either the Kingdom of Saudi Arabia, or Iran and I will never proclaim myself towards Iran (a man must keep some principles).

We can be all angry find a solution to erase them. As I see it, my version is more productive in the end. They are targeting close to the border as much as possible, this implies that their hardware has limitations. Even so to merely rely on anti-drone and some version of an Aveillant system is economically not too viable, it will merely make some places (like airports more secure). When we look around we see that there are 6 ways to take care of drones.

  1. Guns, which requires precision and manpower
  2. Nets, same as the first, yet a net covers an area better chance of results and a chance to get the drone decently unharmed, or retrieve enough evidence to consider a counter offensive
  3. Jammer, a two pronged option, as the connection fails most drones go back to their point of origin giving the option of finding out who was behind it.
  4. Hacking, a drone can be used for hacking, but the other way is also an option if the drone lacks certain security measures, optionally getting access to logs and other information
  5. Birds of Prey (Eagle, Falcon), A Dutch solution to use a bird of prey to hunt a drone, an Eagle will be 10 times more deadly than a drone, Eagles are a lot more agile and remaining as fast all the time.
  6. Drones, Fighting drones with drones is not the most viable one, however these drones have paint guns which would hinder rotor function and speed, forcing gravity and drag to be the main issues for the drone.

The issue is not merely how to do it, but the specifics of the drone become a larger issue. An Eagle and most solutions will not work against the MQ-9 Reaper drone (to name but an example), yet Hezbollah and Iran rely on the Qods Mohajer (optionally the Raad 85), which when considering the range is the more likely suspect. What is important to know is that these devices requires a certain skill level, hence there is no way that a Houthi forces could have done this by themselves. It required Hezbollah/Iranian supervision. There the option of jamming and drones with a paint gun would work, if a jammer gets shot onto the drone, it will give them a way to follow, paint can have the same effect whilst at the same time limit its capabilities. If the drone is loaded with explosives and set for a one way trip there is a lot less to do, yet the paint could still impact its ability if there is enough space left, if the paint is loaded with metal it could light it up making it a much better target. All options that have been considered in the last few years in anti-drone activities, the question is how to proceed now.

I believe that inaction will no longer get us anywhere, especially when Hezbollah is involved. That is the one speculative part. There is no way that Houthi rebel forces have the skills; I believe that Iran is too focussed on having some level of deniability, hence the Hezbollah part. It is entirely probable that Iranian forces are involved, yet that would be the pilot and with the range, that pilot would have been really close to the Yemeni border making Abha airport a target, yet unlikely that more inland another target would be available to them.

Knowing that gives more options, but also makes it harder to proceed, the earlier five methods mentioned are direct, there is one other option, but I am not discussing it here at present as it optionally involves DoD classified materials (and involves DARPA’s project on Machine learning applied intelligence to the radio spectrum) and lets not put that part out in the open. It is actually a clever program conceived by Paul Tilghman, a graduate from RIT (Rochester Institute of Technology), an excellent school that is slightly below MIT and on par with UTS (my creative stomping grounds).

It is a roadmap that needs to be followed, I am all for bombing Hezbollah sites, unlike the earlier mentioned group of 15, I prefer my level of evidence to be a little higher as such the Tilghman solution is called for, after that, when we get that we can address the viability of Beirut and Tripoli with 2500 lbs hardware donations, depending on the evidence found mind you, we can make adjustments, as some materials would have needed to be shipped to Yemen either directly or via Lebanon and in all honesty, I am of the mind that Iran would not have done this directly. Proxy wars require a higher level of deniability to remain proxy wars; as such we need the hardware as evidence.

And even as we see: “Mohamed Abdel Salam, said the attack was in response to Saudi Arabia’s “continued aggression and blockade on Yemen”. Earlier in the week, he said attacks on Saudi airports were “the best way to break the blockade”” (at https://www.theguardian.com/world/2019/jun/12/yemen-houthi-rebel-missile-attack-injures-26-saudi-airport) we need to realise that this is growing and potentially a lot larger than before. Even as we acknowledge that the forces have withdrawn from the harbour, we have no insight on where they went, there is no indication that they have stopped fighting, merely that they are at the moment inactive, a status that can change at any given moment.

Add to that the threat (or is that the promise) by Tehran who decided to “threaten to resume enriching uranium towards weapons-grade level on 7 July if US sanctions are not lifted or its European allies fail to offer new terms for the nuclear deal“, here my answer is ‘What deal?‘, there is enough indication that enriching never stopped, but was merely scaled down to 95% of previous effort, as such there is no need to offer more incentives that will only be broken. As such my strategy to seek out Houthi (and optionally Hezbollah forces) to take away the proxy options of Iran, they must either commit 100% or back down, at present their fear is having to commit fully to this and change the stage of proxy war to actual war, and as such my strategy makes sense. They have no hope of winning as too many government would be willing to align with Saudi Arabia (that might make them surprised and happy as well), and a united front against Iran is what Iran fears, because Turkey would have no option but to cut ties out of fear what happens when we are done with the other Iranian puppets.

It is perhaps the only side where I disagree with James Jeffrey (US special representative for Syria engagement), I do not believe that it is a “hegemonic quest to dominate the Middle East“, I believe that Iran knows that this is no longer an option, yet bolstering foundations of a growing alliance is the best that they hope for and here Iran merely facilitates in the urge to state to Syria (the government and its current president) in the voice of ‘You owe us, we helped you‘, it is slightly pathetic and merely the voice of a used car salesman at present. As more of the proxy war becomes open and proven Iran is backed into a corner, it makes Iran more dangerous, but it also forces them to act, not through proxy and I am decently certain that Iran has too much to lose as present, especially as Russia denied them the S-400 solution.

Even as Gevorg Mirzayan (an expert in Middle East and a leading analyst at the agency Foreign Policy) is getting headlines with ‘‘Dumping’ Iran Would Be Mistaken, Since Russia Doesn’t Know What The US Will Offer In Return‘, we see that the stage is a valid question, but there we also see the answer. the direct (and somewhat less diplomatic) answer is “Never set a stage where a rabid dog can call the shots“, the more diplomatic answer (by Russian Deputy Prime Minister Yury Borisov) was “Russia has not received any requests from Iran for delivering its S-400 air defense systems” is nice, and it puts Iran in a space where they need to admit to needing this kind of hardware, yet on the other side, Russia realises that Iran is driven to flame the middle East and down the track if its alliance is too strong, takes Saudi Arabia out of consideration for several lucrative Russian ventures and they know it.

All these elements are in play and in place, so segregating and isolating Hezbollah limits the options of Iran, making it an essential step to pursue. Interesting is that these steps were firmly visible as early as last year August, and that group of 15 did little to bolster solutions towards truly isolating Iran, that Miaow division was optionally seeking milk and cream and finding not that much of either.

So the time is now essential moving to critical to take the options away from Iran, we let Lebanon decide whether they want to get caught in a room painted in a corner with no directions remaining, at that point they become a real easy target.

That was not hard was it?

Happy Friday and remember, it will be Monday morning in 60 hours, so make the most of it.


1 Comment

Filed under IT, Military, Politics, Science

That’s the way the money flows

The Independent had an interesting article 2 hours ago. The article (at https://www.independent.co.uk/news/world/americas/china-drones-spy-us-dhs-security-data-alert-a8922706.html). The title leaves little to the imagination with: ‘Chinese drones may be stealing sensitive information, DHS warns‘, after the Trump google play, after his refusal to submit to subpoena’s, after the anti Huawei activities that so far has never yielded any active evidence (the 8 year old case was settled within months are done with). Now we see: “Chinese-made drones in America may be sending sensitive data to their manufacturers back home where it can be accessed by the government, the United States Department of Homeland Security (DHS) has warned“, which might be a nightmare if it was not so hilarious. You see the next quote: “CNN, which obtained the internal alert, reported that the DHS fears drones will offer Chinese intelligence unfettered access to American data“, it comes across like we have a case where a CNN reporter has been hit by a silly stick and never recovered. Consider the drones we see, there is no space to have a dedicated hack system on board. Yes some can be done with a mobile, and there is plenty of space in that device, now consider the ‘sensitive’ data that needs to be found, the data needs to be connected to (and with all these faulty Cisco routers that is relatively easy at present), then a selection needs to be downloaded and that is merely for one place, one device. All this stops when any person uses common cyber sense. It is the revelation that we see next, that is the one that matters. With: “Though the alert didn’t name specific companies, the vast majority of drones used in the US and Canada are made by the Shenzen based Company, DJI, CNN reported” we see the part that matters. As drone services are up on an almost exponential growth as we see the push that got there. The news from November 2016 gave us: “Domino’s Pizza Enterprises Limited (Domino’s) and drone delivery partner Flirtey delivered the first order, a Peri-Peri Chicken Pizza, and a Chicken and Cranberry Pizza“. Consider the option to avoid traffic in New York, Los Angeles, San Francisco, Boston, Chicago, Seattle, Pittsburgh, all places with massive congestion. Drones are the optionally the newest quick way to deliver food, Amazon needs, Walmart needs, all in growing need due to the events where retailers and shippers combine forces to avoid a few items, and with congestion set to zero, people will flock to that consideration. Now the operational part, it seems that DJI is ahead of the curve, another Chinese company decided to truly innovate and now that the push is there and America is bankrupt (as I personally see it) anything possible to avoid money going to China, America is taking a pot shot at that. So when we are also treated to: “A spokesman for DJI denied that any information was being transmitted to it from its drones, adding that the security of its technology has been independently verified by the US government.” I start wondering if DHS was able to do its job properly. Now let’s be clear, there is no doubt that ANY drone can be used for espionage, especially if it is quiet enough. Yet is that the issue for DJI, or is that an issue with the spy that utilises drone technology? Yet that is actually not the only side, on the other side we see mentioned: “Those concerns apply with equal force to certain Chinese-made (unmanned aircraft systems)-connected devices capable of collecting and transferring potentially revealing data about their operations and the individuals and entities operating them, as China imposes unusually stringent obligations on its citizens to support national intelligence activities,” Now, this part does make sense. It is the same as the Apple Fitbit, that due to its global nature started to hand out the jogging patterns of Special forces in the Middle East, so within 3 days several members of the two dozen operatives had a check on their calorie burning and health, whilst the mapping data showed the world where the CIA black site was (oh apologies, I meant to say a military specialist endeavouring location of an undetermined nature). The question becomes how was the ‘the security of its technology has been independently verified by the US government‘ achieved? Was that verification process competent, or perhaps slightly less so?

I am not stating my verdict in either direction; yet the entire Huawei mess, as well as the DJI setting implies that the growth industries are shunned from America, mainly because it is not an American industry. Yet in all this, the forget that places like the EU and India are large enough to go forward with both players and truly grow further, whilst the downturn and the economic lag that the US is creating will merely grow the loss of momentum and the recession it will fuel in other ways. I would consider that the setback that Google is trying to create will have larger repercussions down the road. As larger Data vendors will now optionally choose the Chinese side, they will grow market share. You see no matter how it is sliced, all this is data based and data can only grow if there is usage. So when people remain with Huawei as their phone keeps on working, we see that there is a larger concern soon enough. At some point people will stop trusting Samsung, Google and Apple phones, which works out nicely for several players (Microsoft actually more than most), what do you think happens when the larger share of 14.7% of a global market changes to player three and not use Google apps to some degree? Google momentum relies on non-stop data and usage, when a third of the 60% that these three cover stops, do you think that this has no impact for Google?

The same applies to drones. You see intelligence makes the drone and as it grows its market share and the collected data of drone usage is set, the innovation of DJI grows faster. It is the difference between generation now and generation 2022, DJI will grow and can grow in several directions, yet the entire the setting of ‘data theft’ we see that there is a lack of ‘what’ data. What data is collected, the flight path? Well, I think we all need to know in 2023 what flight path was taken for the delivery of 342,450 pizza’s delivered per hour, is it not? It is not that Google Map has that data, and within a building in New York, is there truly a clear sign in the drone itself who exactly the merchandise was for, or was that on the box (instead of the drone). Now, there is no denying that some of that data would optionally be accessible to the Chinese government? Yet what data, what level of data? Do you think that they have time for the hundreds of drones and the data whilst they can monitor 20,000 times that data with a spy satellite (and an additional truckload of data that the drone never had in the first place?

It is when I see ‘unfettered access to American data‘ where the questions become pressing. It is like watching Colin Powell coming into a non-disclosed location with his silver briefcase and in the end the lack of WMD’s, are we going in that direction again? when I see ‘unfettered access to American data‘, it is at that moment I see the optional comparison (an extreme lose comparison mind you) with the innocent preachers daughter who did the naughty thing to 30% of the boys coming to Sunday sermon, having attempted things I cannot even rent on adult video. It is the CNN article (at https://edition.cnn.com/2019/05/20/politics/dhs-chinese-drone-warning/index.html) that gives additional rise to concerns. When you see: “Users are warned to “be cautious when purchasing” drones from China, and to take precautionary steps like turning off the device’s internet connection and removing secure digital cards. The alert also warns users to “understand how to properly operate and limit your device’s access to networks” to avoid “theft of information.”” It seems to me that there are dozens of ways to get this data, a drone seems like an expensive long way round-trip to get to that data, whilst more can be accessed in several other ways and it is the speculation through ‘device’s internet connection‘, so when we see one of these devices (at https://www.dji.com/au/phantom-4-pro-v2/info#specs), we are treated to: “The new Phantom 4 Pro V2.0 features an OcuSync HD transmission system, which supports automatic dual-frequency band switching and connects to DJI Goggles wirelessly“, where did the internet come in? Yes there is an app, to get a live view from the drone, so what ‘unfettered access to American data‘ could there be that Google Maps at present does not have in more detail?

It is the next part that is the actual ace. When we see: “DJI, which reported $2.7 billion in revenue in 2017, is best known for its popular Phantom drone. Introduced in 2013, the drone is the top-selling commercial drone on the market“, information the Independent did not give us, that is the actual stage as I personally see it. It was $2.7 billion in 2017, there is no doubt that when drone delivery truly takes off, at that point revenue that sits between $15 and $27 billion is not unrealistic, the dire need to avoid congestion on a global scale will drive it and that is before you realise the non-US benefits in London, Amsterdam, Paris, Berlin, Munich, Madrid, Barcelona, Rome, Athens, Moscow. At that point you will see stronger growth and I haven’t even looked at the opportunities in a place like Mumbai, Tokyo, Delhi, Bangkok, Rio, Buenos Aires and Sydney yet. Everything leaves me with the impression that this is not about security, it is about money. That fact can be proven when you realise that everyone remains silent on the 29 new vulnerabilities that Cisco reported merely a month ago. How many Cisco router stories have come from that non-technologically refined White House, where they are currently optionally limited by “Cisco routers, including ones that can be found in malls, large companies or government institutions, are flawed in a way that allows hackers to steal all of the data flowing through them“, the cybersecurity company Red Baron handed out that issue to the media last week, so who picked up on that danger to ‘unfettered access to American data‘? And when you consider ‘it allows potential malicious actors to bypass the router’s security feature, Trust Anchor. This feature has been standard in Cisco’s routers since 2013‘, when we realise that Cisco is a household name on a global scale (especially when connected to the internet), the entire Cisco matter seems to be at least 15,000 times worse than any DJI drone ever could be, and the fact that DHS remains silent on that gives (again, as I personally see it) is added proof that this is merely about the money and the fact that US companies are losing markets on a global scale.

I could set the stage by singing ‘All ‘Bout the money‘ by Meja and ‘That’s the way the money goes‘ by M, but then, I realise that people would most likely pay me serious money not to sing (my voice is actually that bad).

That’s the way the money flows, specifically at present in a direction that the US is for the foreseeable future most displeased about.


1 Comment

Filed under Finance, IT, Media, Military, Science