Category Archives: Military

What makes it a story?

That is the question that floats to the top. You see, the bulk of the media, including the BBC nowadays have lost too much credibility. The issue becomes verification, and in too many places there isn’t to much of that. So in this mindset I stumbled upon an article. This was in part funny, as I mentioned the ‘disgraced’ Al Jabri only two days ago and 11 hours ago this article was published by the BBC. I do not think the two are connected and it is clear that no such connection should be made other than the mention of these timelines (to keep my blog to some degree a valid source). But 11 hours ago (at https://www.bbc.com/news/articles/c4gz8934wrro) we see the appearance of ‘Power, oil and a $450m painting – insiders on the rise of Saudi’s Crown Prince’ by Jonathan Rugman. The article was glared over by me, until I noticed a name. This set me in a different mindset and it is time to report on this.

It all starts with “he summoned a senior security official to the palace, determined to win his loyalty” and the name Saad al-Jabri is mentioned. The man who seems to manage a multi billion portfolio for the CIA (allegedly) and was in a court case in America, whilst he is in Canada and setting the space not to allow certain evidence to be mentioned. We then get mentions like “According to Jabri” and (did I mention) that he is a disgraced official, but that part is not mentioned in the article? The mentioned stage “he was friends with the heads of the CIA and MI6” makes for ‘exciting’ reading, but in my mindset it is a dangerous connection because there is a lot of non-verification. So we get the first reference ‘Family of exiled top Saudi officer Saad al-Jabri ‘targeted’’ (at https://www.bbc.com/news/world-middle-east-52790864). There we get “Dr Saad al-Jabri, who helped foil an al-Qaeda bomb plot against the West”. My issue was that there is little verification. Now, this makes sense because it is intelligence related and they do not spout these issues in open places. But with the accusation of treason and ‘funds removal operations’ according to other Saudi sources it sets the possibility that Al Jabri made a sting using optional Al Qaeda plants and now we get the setting that the CIA gave him safe passage whilst Al Qaeda gets the optional blame for it all. I am not saying that this is what happened, but the timing of the intertwined facts are a little too convenient (for Al Jabri). This could have been all set aside with proper verification, but the term ‘according to sources’ allows for my speculation, and lets be clear, I was and still am speculating on this.

And the stage of “He was also the linchpin in all Saudi Arabia’s relations with the “Five Eyes” (US, UK, Canada, Australia, New Zealand) intelligence agencies.” This is important because linchpin means “a person or thing vital to an enterprise or organisation”, as such Saad Al Jabri was important to the stage of some (most likely the CIA) and Al Jabri in a self professed difficult situation was eager to carry that mantle (my speculation), especially as he was accused to have taken the quick way out with billions. People have done a lot more for a mere 0.1% of such an amount. 

Then we get to “we shed new light on the events that have made MBS notorious – including the 2018 murder of Saudi journalist Jamal Khashoggi” and this had issues with me. On February 27th 2021 I wrote ‘That was easy!’, (at https://lawlordtobe.com/2021/02/27/that-was-easy/) in this blog article I shot holes in an United Nations document, with a lot more issues that I was happy with. The fact that I had even one issue with a document from the United Nations should have been close to impossible. The fact that I did implies that this was a hatchet job and I added the UN document so that people could see it for themselves. In addition at a later stage I added the mention that Khashoggi was alive with a mistress spending their days on Bora Bora (I also mentioned that this came from a non-reliable source). The setting we have now is that there is a debatable story (in depth) due to at least one main source that is debatable and the mentions of Al Jabri needs to be seen as at the very least debatable. This is what you get when the lack of verification is there, there is simply no other outcome as I see it.

We then see “accusing MBS of forging his father the king’s signature on a royal decree committing ground troops”, as well as “The prince was apparently so impatient for his father to become king that in 2014, he reportedly suggested killing the then-monarch – Abdullah, his uncle – with a poisoned ring, obtained from Russia. “I don’t know for sure if he was just bragging, but we took it seriously,”” my issue here is two fold, the one mention of “I don’t know for sure if he was just bragging” sounds nice, but in both cases the source is Al Jabri and in my view he is a debatable source on more than one issue and verification is missing here and that is all on Jonathan Rugman as I see it. This all takes me back to the 70’s. A writer named James Grady wrote a book that was made into a movie with Robert Redford, the movie was called Three days of the Condor. After I saw the movie I also read his sequel ‘Shadow of the Condor’ (I believe that was the book). There we come across the term ‘Gamaljoen’ (I read the book in Dutch). The term makes reference to a person that is raised to a much larger status than he (or she) should be. Because of the status those who are wielding that person are raised as well. That is the feeling that I have on Al Jabri. Now lets accept that I could be (totally) wrong, but that requires verification to see and we see no verification with the debatable doubts I throw on to the Khashoggi issue we get an unbalanced stage. And I am trying to avoid the “he said, she said” debate. This is why there are issues with an in depth story. There are other sources mentioned, but these are all to ‘trivial’ matters. 

We then get a part that reflects on my story yesterday ““He planned for my assassination,” Jabri says. “He will not rest until he sees me dead, I have no doubt about that.”” Whether he did or did not is also debatable. The ‘simple’ fact is that I created an optional plan to do just that, in under an hour no less. And I am not a professional on the matter. The fact that Mohammed bin Salman Al Saud has actual specialists on the matter and we see some ‘tiger team’ bungling it puts question marks on it all. Is there an actual execution order out on Al Jabri? It is a valid question. I have no doubt that Al Jabri is likely to face jail time at the very least is he ever goes back to the Kingdom of Saudi Arabia, there is a wallet with billions (allegedly) missing to support my view. 

With “The killing of Jamal Khashoggi at the Saudi consulate in Istanbul in 2018 implicates MBS in ways that are very hard to refute. The 15-strong hit squad was travelling on diplomatic passports and included several of MBS’s own bodyguards” the writer of the BBC story is missing the beat. You see, the setting of “implicates MBS in ways that are very hard to refute” is what I did (in part) in the UN document in the article I mentioned earlier (That was Easy!) I cast a really large doubt in the issues, in the second setting ‘15-strong hit squad’ is also extremely debatable. If it was a hit a mere 1 person would have sufficed. That there was an optional team to ‘retrieve’ is possible, but the media used the setting to explode their paper revenue, so too much of it is too ludicrous for words. The media is nowadays too much about creating emotional flames for the supportive need of clickbait, at the expense of their own credibility. 

Then we get “A declassified US intelligence report released in February 2021 asserted that he was complicit in the killing of Khashoggi” yet the linked article states “The report released by the Biden administration says the prince approved a plan to either “capture or kill” Khashoggi”, whilst we see “We assess”, which in CIA terms would be seen as fairy tale material. It lacks evidence, merely conjecture. All whilst the linked report (by the office of the US director of national intelligence) can no longer be retrieved. That’s your evidence? 

There is a lot to make up for and the BBC better do that soon, as the article ends with “Jonathan Rugman is consultant producer on The Kingdom: The world’s most powerful prince” the writer being a producer of materials as well? Whatever could be wrong next.

The amazing amounts of fairy tale materials that goes back as far as the United Nations gives pause for a larger setting, whatever you call ‘inDepth’ is almost a new kind of story with the APNews happily posting it with the mention of ‘Former Saudi official alleges Prince Mohammed forged king’s signature on Yemen war decree’ a mere 4 hours ago. Is that how the news goes around nowadays?

And to all I say have a great Tuesday, a mere 4 hours until breakfast for me, time that I snore like a lumberjack. 
Leave a comment

Filed under Finance, Media, Military, Politics

Cold War 2.00.05/LW

The BBC alerted us to an optional issue, the article (at https://www.bbc.com/news/articles/clyn8vk4g42o) is a tap on the door. There is absolutely nothing wrong with the article. It alerts us and it tells us stuff, but there is an underlying setting. You see there is an absolute chance that Russia is active in Germany, but there are doubts within me. Russia has a lot more problems than many of us realise. And there we, optionally, now have a new player in the German field. The radical sited lone wolf getting their message from Tehran. I will come right out with ‘it is speculative’, it is my speculation. You see with “Holes mysteriously found cut in army base fences” we see part of the deception. If it was me, I would hide 2-3 drones, out of sight with a good view of several buildings, not flying in a landed state. Army camps have many roofs and not of them are watched all the time. And a landed drone leaves no signature. So there the culprit, optional plural have drilled a hole in a fence, nicely hidden, but not strong enough that it will avoid detection. So the guard patrols call it in and suddenly the base is rushing to the sensitive places and checking them out. And now with the drone cameras they will know WHERE to hit that place, optionally not hitting that place at all (that week). The army signature move is to check all the sensitive areas as well as the munition storage and armouries. Their alert giving the lone wolves where to come soon enough and that time there are no holes at entry. 

Not a case they expected, but this is not an intentional Cold War or Cold War 2.0, it is a Cold War 2/LW (Lone Wolf). A new setting and most standard procedures will not suffice, well they might but you are up against a different enemy, the Lone Wolf is desperate for success and more important, he/she will be more desperate for success, as such they will resort to killing a lot sooner, as such the plan changes somewhat. Whether they are out for secrets to dispense to a player like Iran (optionally one of their agents via Hamas, Hezbollah, or Houthi). I see this as a realistic setting. 

We cannot merely rely on:

  • An alleged plot to assassinate Germany’s top weapons manufacturer.
  • Phone taps on a high-level Luftwaffe call.

These are still settings that are happening and it is even possible that these are separate issues. In any espionage setting the Luftwaffe taps could most definitely be Russia as for the alleged assassination. It is anyones guess who it is and how real it is. The danger of an assassination cannot be ignored, but these people are aware of those dangers and the replacement is likely to be a lot more dangerous than the one they replaced. When the danger becomes realistic, the claws come out and they will suddenly be a lot more dangerous, as well as the BND (Bundesnachrichtendienst), they will at that point be out for blood, all of the blood they can lay their hands on. 

So am I right?
Not sure, but I just gave you a scenario that I came up with in 5 minutes. These Lone Wolves have been brooding over a plan for months. It is there that we see the folly that I saw in the case involving Saad bin Khalid Al Jabri in Canada. In 2021 we get from 60 minutes that Mohammed bin Salman wanted him dead. This might be true, but then we get in August 2020 that ‘Saudi hit squad was sent to Toronto to try to kill former intel official, lawsuit alleges’ (source: Toronto Star) with a 100 page lawsuit and in the end none of the allegations have been proven in court. What a jolly shit show. There was another article (I forgot where it was) stating that the Tiger Team of 30 man were employed. To give you a little rundown, after 42 years leaving the army (draft) I came up with a simple idea of using 3 teams of 2 man and at the end of that exercise that would have taken a mere 20 minutes with one team active for an additional 12 hours, there was no living Al Jabri, he would be as dead as the concrete building he was living in. OK, I do not know the setup of that building, but it would be a simple exercise for 3 teams of 2 (one team observing and directing. An optional use for the M202A1 66mm FLASH with adjusted missiles would be used (in a certain debilitating case) but that is merely on a ‘what if’ whim. The rest is a simple exercise using two boom boom items. Hard case, a mere exercise and I am certain that certain parties (who are in this field) could have thought of this long before I did. I have had my issues with the assumptions that Saad bin Khalid Al Jabri have tried to sway us with. The other fact was that the US, where a lot was set in their courts (even though he was in Canada) with all kinds of objections against the Saudi representative there. I had my doubts on a lot of it. This is a mere setting and this now goes back to Germany. Is there an optional Cold War brewing? That is very much possible, but in all this the Lone Wolf is optionally overlooked. So are these the actions of a Lone Wolf, or a Lone Woof. Anyone can make a hole in a fence, having the Army run around would be fun the the lone woof looking from a distance, it does not make for a base invasion. So at the near end of the article we get “Not all of these events can definitively be blamed on Moscow, but Germany is on heightened alert for possible acts of Russian sabotage, because of Berlin’s continued military support for Kyiv” this is a better be safe then sorry and I cannot disagree, but the media had a decent responsibility to state more than this and the mere ‘Not all of these events can definitively be blamed on Moscow’ was not enough. With Russian sympathisers all over Europe a lot more was required, because belief it or not Lone Wolves are a clear and present danger to many European nations. Troll farms are ‘their’ essential misinformation, but merely misinforming people and watch it unfold tends to be only entertaining in the first few hours. When we get to tipping scales, actions tend to be needed to make the scales tip over a lot more, but that is merely my point of view.

As “last month when CNN reported that US officials had told Berlin of an alleged Russian plot to kill the chief executive of Germany’s biggest arms company Rheinmetall” doubts come into play again. You see a player like Rheinmetall has procedures in place for this level of events, of that I have no doubt. So what is to be gained from a simple and single execution? Is it the target, or is it a ploy to keep the BND active in the wrong places? Lets not forget that Sun Tzu taught us that all war is based on deception. So how did CNN get the news? Any alleged plot (especially from Russia) would be based on the expertise by people like the GRU and they do not talk (if they do President Putin has a lot more problems that he realises). So how did CNN get it, what were the sources? As such I have to some degree my doubts on this.

Have a fun day and that red dot you see on your chest? It’s merely your imagination.

Leave a comment

Filed under Media, Military, Politics

How Presidents become sniffling bitches

It is strong, it is optionally regarded as disrespectful, but seeing the BBC give us ‘Ukraine claims to control 1,000 sq km of Russian territory’, the story (at https://www.bbc.com/news/articles/cx2lmr29ygjo) comes with the underline of President Putin called stating “Russian President Vladimir Putin has described the incursion as a “large-scale provocation” that involved “indiscriminate shelling of civilian buildings, residential houses and ambulances.”” (Source: Baltimore Sun). So how does it feel to have the shoe on the other foot?

Lets not forget 

Russia has bombed hospitals, churches, refuge’s and civilians with intention. Now after almost devastating losses the Ukraine is expanding into Russia. Ukraine is coming to Russia and calling these new lands optionally their new home. It is a little bit speculative, because there is no clear path. As I can see it, Moscow will soon have another name (my wishful thinking) and the Ukraine has already found a new home as their community building, it will be the Kremlin. It might be a little too soon for that thought. But there is another setting. The other setting is that several GRU members will be wanting a way out. Not everyone is agreeing with the picture that President Putin is painting and as such GRU officers with folders on the agreements on Pascal Hillebrand, Thierry Baudet and other like minded people will be eagerly wanted by the Dutch AIVD and media. Not to mention the army of internet troll media arrangers who are doing real damage to European, American, Australian and Canadian democracies. All that became an optional reality when Ukraine took land from Russia. 

This hasn’t happen since Stalin (1941) when the Germans started operation Barbarossa. Now there is a setting we shouldn’t dispense with, Russia could mobilise their entire army now. The problem is that they have plenty to sow into that region. It weakens the Russian forces to a massive degree. When you have an army that merely covers 70% of your country and pushing it to different areas, more areas will be weakened. The second setting is that it will take longer for Russia to ever recover. The amounts lost and the lack of a properly functioning logistics and equipment supervision, for that matter the actual availability of equipment are all matters that are strangling Russian forces. Using your finger saying ‘pew, pew, pew’ doesn’t really work on forces who have seen their homes devastated, and it was an unprovoked devastation. Being that the Russian forces are relying on North Korean and Chinese arms to an increasing degree is also not to be underestimated. 

On a sideline (making it about me), there is still the plans to ‘make’ Russian nuclear reactors go into meltdown mode. Should Ukrainian forces enable that part than the loss of a mere 3 reactors will put Moscow into dark mode, no electricity and no heating. Taking in consideration that things turn cooler in November which lasts until mid February and it stays snowy until April. You see concrete and steel buildings are nice, but without heating they nearly instantly turn into refrigerators and sleeping there is a one stop location to the death sleep. 

That was the part Russia forgot about, and people like Vladimir Solovyov and Vladimir Molchanov forgot about. We saw their ranting on YouTube and they all forgot what happens when their turn is up. They never thought Russia could be attacked, but the aggressive nature that Russia employed since February 2022 now has a new wrinkle. As Putin announced the 2022 Russian invasion of Ukraine, he claimed to commence a “special military operation”, side-stepping a formal declaration of war. Now that comes to bite him and his ‘friends’ will soon be a lot more afraid then they thought they ever could be. In the mean time I designed several new weapons, one to cluster down on Russian harbours and that is a nice piece of icing (DARPA eat your heart out). You see most weapons are about destruction, as such I designed a steal approach to dislodging. It seems less ‘effective’ but there is nothing as effective as taking an entire port out of commission. OK, I admit that some harbours will merely be in part less effective. Russia has a nice navy when it doesn’t work it is merely a bundle of steel going nowhere. And as they lose their Black Sea and Atlantic abilities, they will see the disaster they unfolded in 2022. Consider (merely consider) that Zapadnaya Litsa is take off the operational board, that and their Arkhangelsk become set pieces in a Russian comedy called ‘What do we do now’?

How will it go from here?
I have no idea, but the fact that the Ukraine captured land from Russia was unforeseen by everyone, Russia least of all. So when we consider “A senior British military source, who asked not to be named, told the BBC there was the risk that Moscow will be so angered by this incursion that it could redouble its own attacks on Ukraine’s civilian population and infrastructure” is decently accurate, but then Russia had bombed Ukraine pretty much into the stone age. This is the setting where we see that people stated that this would be over in 2-3 days, it is now year two and Russia is losing lands. That is the reality they fece and as such a lot more domino stones will be falling over. I am partially hoping that several GRU and FSB officers will defect the bad place they are in and come with their files to other places outside Russia. They still need proper vetting as this is a tactic that dead spies cater too (a Sun Tzu reference, Chapter 13). But it is clear that Russia has now a different kettle of fish on their table and they were never ready for that part.

So as we revisit the current losses consider how come that the 20th strongest army is setting such losses on one of the top three armed armies of the world?

When we consider that for about 5 hundred years we have seen the expedition of logistics, hardware distribution, armed forces and intelligence gathering. So how come that a 2-3 day war has become a 2-3 year war? I stated a partial in ‘On the subject of failure’ (at https://lawlordtobe.com/2023/02/27/on-the-subject-of-failure/), yet an capture the land against Russia was never a reality, how wrong I was and I was not alone there as the BBC now shows me.

All war is founded in deception, a quote that China came up with over 2000 years ago, to see it to this degree is almost unbelievable, so President Putin had clear documentation that could have prevented this. How the mighty fall.

Enjoy this day, my Tuesday ends in 20 minutes, Vancouver is just about to start their day with waffles, eggs and more. 

Leave a comment

Filed under Media, Military, Politics

Setting of the day

On a good day
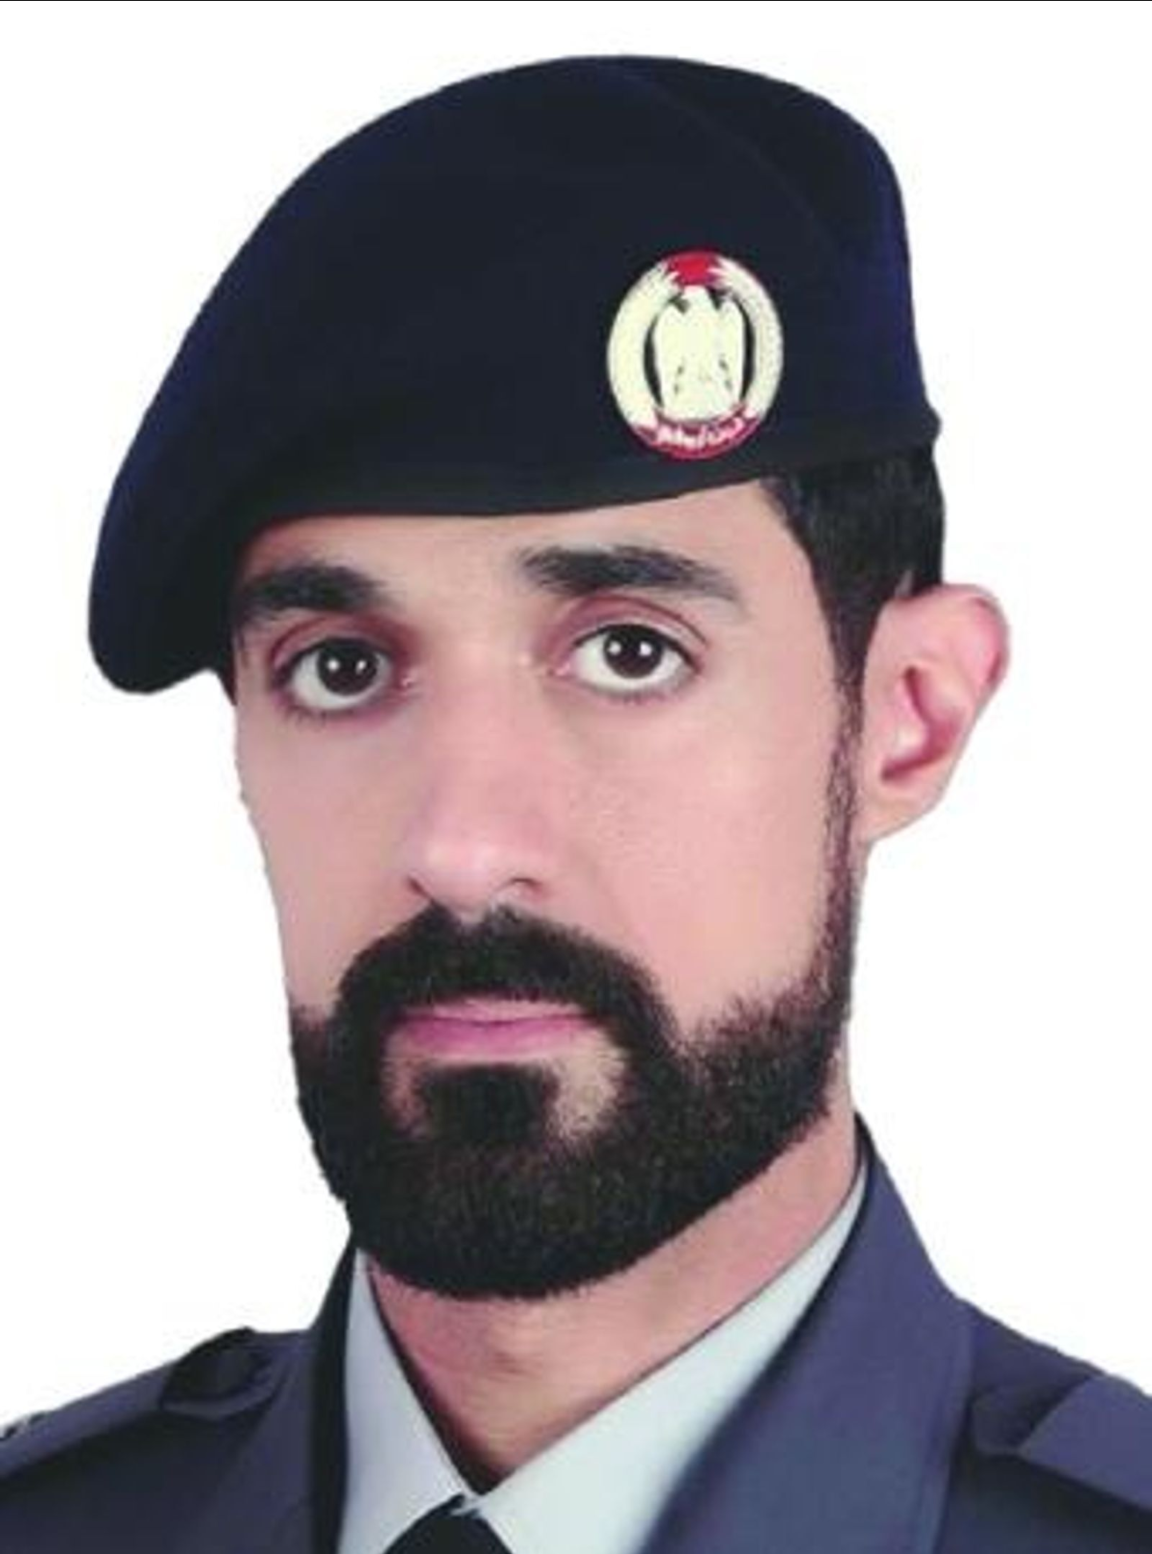
The Khaleej Times Jost informed me on how a good day comes to pass. Here (at https://www.khaleejtimes.com/uae/meet-the-uae-police-officer-who-uncovered-183-money-laundering-cases-in-15-years) we are introduced to Major Saad Ahmed Al Marzooqi. 

The headline ‘Meet the UAE police officer who uncovered 183 money laundering cases in 15 years’. We are also given “He was recently appointed as the first Emirati member of the Financial Action Task Force’s (FATF) International Cooperation Review Team” and we can be mesmerised, or brag about his abilities, but the numbers imply that he slightly uncovered more than one case a month. There are plenty of police forces all over the world where half of these numbers would imply a stellar career. As we gawk over “exposed 183 money laundering cases that are related to drugs and financial embezzlement. He had also created a database of incidents, which contributed to an increase in convictions from a monthly average of 3 to 14” we need to realise that the increase of 3 to 14 implies that this one person achieved more than any average police station in Europe. 

This is the kind of man the world needs and that will be explained in the next article, because the universe relies on balance and the imbalance we are about to see takes the cake and changes an optional day to night.

On a bad day
Yes like any hero that needs a antagonist to make things interesting, we have Microsoft in two mentions. Now this isn’t directly involving anyone at Microsoft, but the follies are a setting that makes things a lot worse.

First we get Wired (at https://www.wired.com/story/microsoft-copilot-phishing-data-extraction/) who gives us ‘Microsoft’s AI Can Be Turned Into an Automated Phishing Machine’ we get to see “Attacks on Microsoft’s Copilot AI allow for answers to be manipulated, data extracted, and security protections bypassed, new research shows” which is not good, but anything positive can me mauled into a criminal jester for organised crime. The additional “Microsoft raced to put generative AI at the heart of its systems. Ask a question about an upcoming meeting and the company’s Copilot AI system can pull answers from your emails, Teams chats, and files—a potential productivity boon. But these exact processes can also be abused by hackers.

Today at the Black Hat security conference in Las Vegas, researcher Michael Bargury is demonstrating five proof-of-concept ways that Copilot, which runs on its Microsoft 365 apps, such as Word, can be manipulated by malicious attackers, including using it to provide false references to files, exfiltrate some private data, and dodge Microsoft’s security protections.” Now, I haven’t seen this, but Wired has a solid enough level of credibility to not ignore this. And that isn’t all. Bargury gives the world “the ability to turn the AI into an automatic spear-phishing machine. Dubbed LOLCopilot, the red-teaming code Bargury created can—crucially, once a hacker has access to someone’s work email” as I speculatively see it a mediocrity solution to turn the Internet of Things into a machine serving organised crime, optionally the NSA too, well done Microsoft. As I see it, the workload of Major Al Marzooqi would increase fivefold when this hits the open world, actually it already has if I understood the words from Michael Bargury correctly. In this, we optionally an even bigger problem, or at least a lot of corporations will.

You see there is a second message, in this case from Cyber Security News (at https://cybersecuritynews.com/microsoft-entra-id-vulnerability/). They give us ‘Microsoft Entra ID (Azure AD) Vulnerability Let Attackers Gain Global Admin Access’ with the subtext “Security researchers have uncovered vulnerabilities in Microsoft’s Entra ID (formerly Azure Active Directory) dubbed “UnOAuthorized” which could allow unauthorised actions beyond expected controls” Now take these two parts together and the phishing expedition could hit every R&D system on the planet using Azure. I am certain that Microsoft will have some patch coming soon, but in the meantime the bulk of R&D (under Azure) will be vulnerable and approachable by many hacker and especially organised crime, because selling secrets to competitors tends to be a lucrative setting and most corporations aren’t that finicky in acquiring something that raises (and assures) the bonuses of the members of their boardroom. OK, this is speculative on my side, but wonder what some will do to get the upper hand in business, especially if there is a bonus raise involved. 

I wish I had a solution, but my personal feeling is that Microsoft has too many holes, loops and a whole rage of other issues and switching to either AWS, IBM cloud or Google Cloud tends to be an essential first step coming to my mind. Now, if there are sceptics who think that I am anti-Microsoft here, they are probably right. Therefor the Links to the two articles were added letting you look at the stories yourself. In the meantime I remember a story in April and it should be my ‘duty’ to inform SAMI that ‘BAE Systems and Microsoft join forces to equip defence programmes with innovative cloud technology’ had a nice article and with the two articles mentioned, SAMI could lay its hands on a truckload of BAE IP. Not sure how far they will get, but free IP is the way to go I say. So when you realise that a large corporation like British Aerospace with all the civilian and military hardware can be accessed, what chances do you think that Novo Nordisk (Denmark), LVMH (France), ASML (Netherlands), SAP (Germany), Hermez (France), L’Oreal (France) have? I do not know if any uses Azure, but it is a good moment for them to select one of the other companies. They could after the event sue Microsoft for damages, but Delta Airlines is already suing CrowdStrike and I am not sure how that will go. In the end it is my personal opinion that this could potentially bite Microsoft hard and it is one of the reasons I do not let them near my IP.

As I personally see it, the companies racing the be the first to launch their (fake) AI will now have a much larger impact. There were already fake data issues, but now the phishing options that are mentioned and when that gets linked to what Cyber Security News calls “UnOAuthorized” the entire IT game changes dramatically and I have no idea how that will play out. 

As my Sunday is almost over and Vancouver only just started there’s a chance we postulate that the next 72 hours will be an interesting one. Have a lovely day (when you are not on Azure).

1 Comment

Filed under Finance, IT, Law, Military, Science

A little late aren’t you?

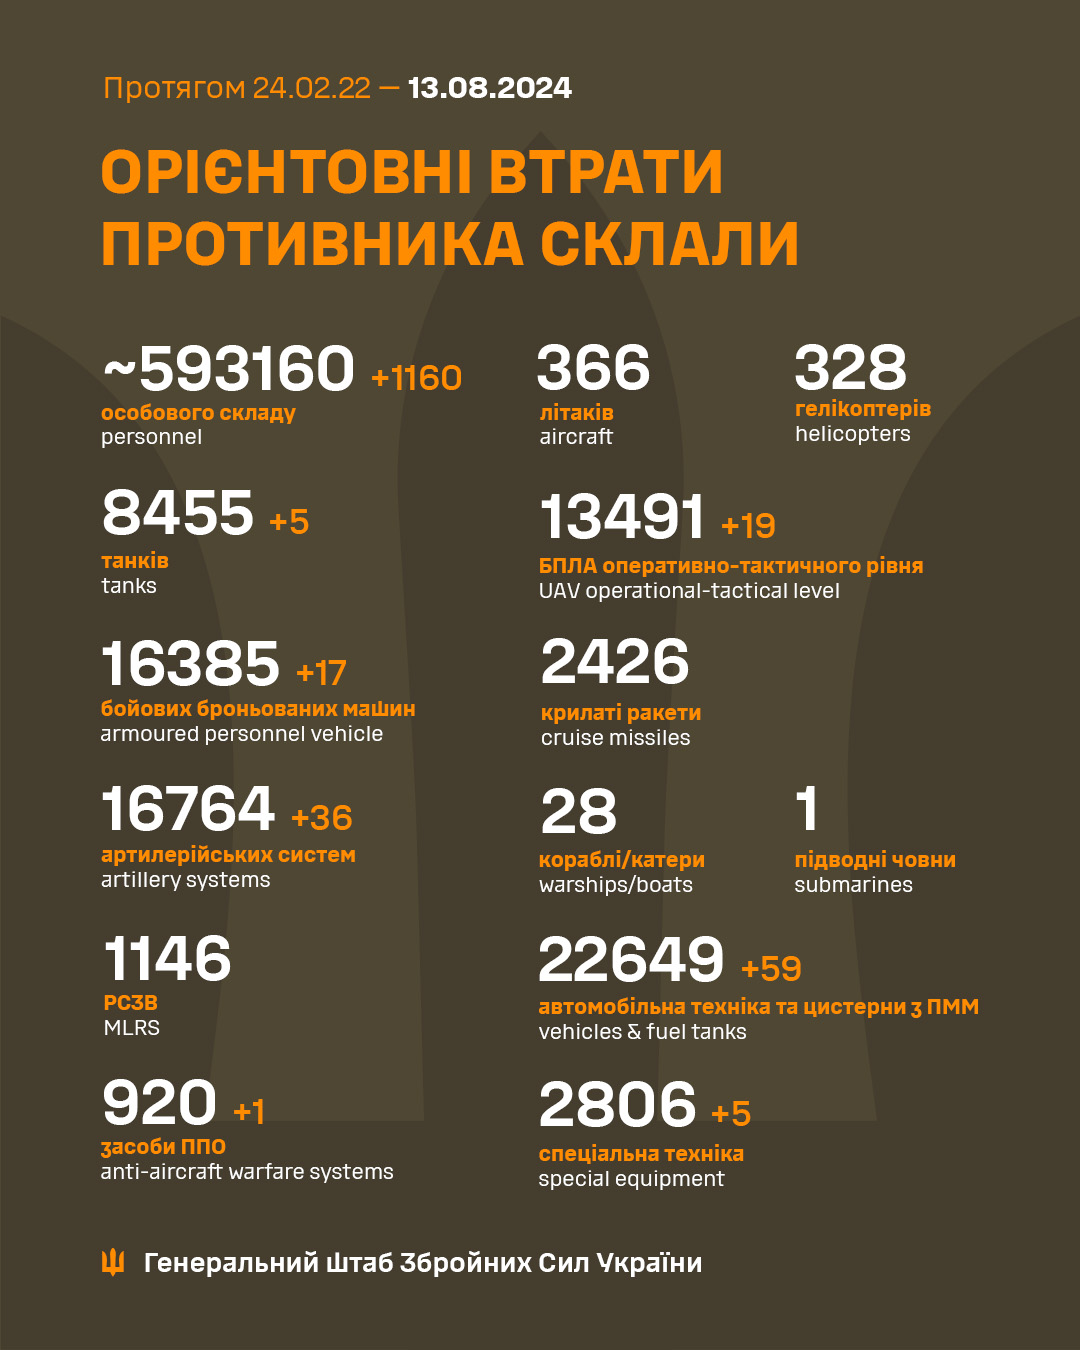
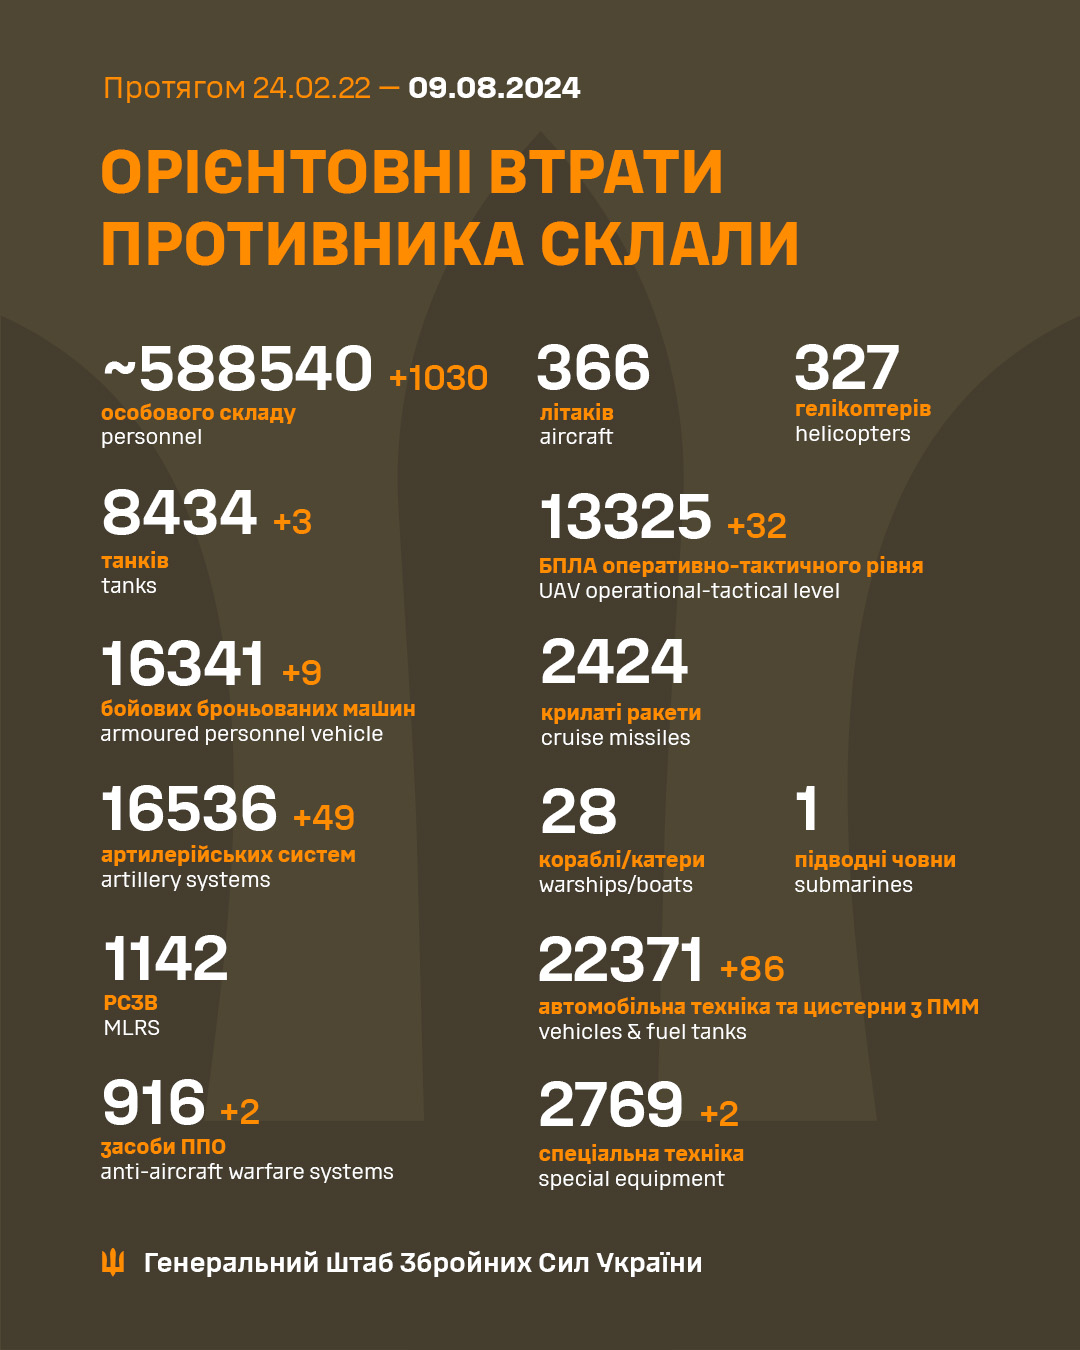
It was the setting I was waiting for. The US has given in to its economic pressures and possibly the fear that China might get to much of a headway. Reuters this morning gives me (and other readers) at https://www.reuters.com/world/us-lift-ban-offensive-weapons-sales-saudi-arabia-sources-say-2024-08-09/ the headline ‘US to lift ban on offensive weapons sales to Saudi Arabia’, which sounds nice but is possibly a little late. Colonel Turki Al-Maliki a member of the Saudi airforce had given us the goods, going all the way back to February 2021. Reuters reported on these attacks in March 2021. In this Reuters is important as they give us ‘Houthis have fired 430 missiles, 851 drones at Saudi Arabia since 2015 – Saudi-led coalition’, the setting is important because civilian targets were aimed at by Houthis amongst them were Saudi airports and structures. So the blockage by the US was weird, especially as the Houthis are a terrorist organisation. So the about turn under the guise of “The Saudis have met their end of the deal, and we are prepared to meet ours”, a little late, isn’t it? But at present the Chinese representatives of parties like the Chengdu Aircraft Industry Group is nothing to be sneered at, with the Chengdu J-20 as an optional buy which was (allegedly) discussed at the World Defense Show 2024 in February 2024 (a speculation from me) is giving the Chinese hope to gain much more from the American Defence Industry. Should the Kingdom of Saudi Arabia take that offer, the setting would open the doors (for China) to larger possibilities in Egypt and the United Arab Emirates as well. The damage to the American Industry could amount to an estimated loss of $30-$50 billion over these three nations alone. Not to mention the lucrative service and consultancy jobs. It would be the first definite slam to the value of the US dollar. China is rearing to take up that option in a heartbeat. I discussed (and partially speculated) this in ‘The next Furlong’ which I wrote on March 10th 2022 (at https://lawlordtobe.com/2022/03/10/the-next-furlong/), as such I was and am now in a stage to emphasise the term ‘told you so’. This setting was clear then and it is a speculated more clear now when we see “Under U.S. law, major international weapons deals must be reviewed by members of Congress before they are made final. Democratic and Republican lawmakers have questioned the provision of offensive weapons to Saudi Arabia in recent years, citing issues including the toll on civilians of its campaign in Yemen and a range of human rights concerns.” We are about to go into election mode and some politicians will fear for their job a lot more than the American Economy. As such China has a decent chance to crush the American Defence industry. I doubt they fear the Russian abilities as the Russians are getting clobbered by the 20th largest army in the world. The Ukrainians are still damaging the Russian, even after the Russians bombed Ukraine into the stone age. That is not a good sales talk, especially  with the current Russian losses stated below

As such we can accept the Reuters statement, because of its projected validity, yet the words we are given “Democratic and Republican lawmakers have questioned the provision of offensive weapons to Saudi Arabia in recent years”, yet the article doesn’t emphasise the attacks by Houthi’s on Saudi civilian targets, which Colonel Turki Al-Maliki showed many clearly going all the way back to 2021, many articles were drowned out by (speculatively speaking) by anti Muslim and anti Saudi voices. Now that China gets to move into a much stronger position, the American administration is taking the gloves off and do what needed to be done in 2021. I reckon that people like Stephanie Kirchgaessner will possibly raise anonymous sources to throw sand in the cogs of common sense. China will love this as this will enable them to get a squadron on Chengdu J-20 into place and optionally ‘gift’ three service teams in the mix, two for maintenance and one to train  Saudi troops. The losses to America will be vast and it will a long term loss. 

As such I think that they were over 2 years late to the party. The initial transfer settings were optionally carved (I have no clear evidence of this) in the airshows of 2021 by SAMI. That would have been the first introductions of Chinese hardware that was to replace whatever America wasn’t giving them at that time. As I personally see it, it might be too late now. You see the Russian losses as shown above are the second piece of evidence. In that setting Russia is no longer a contender and as they are now ‘acquiring’ missiles from North Korea we see a larger question mark, is it merely the lack of missiles or does Russia have a larger problem. I do not know, but Russia isn’t telling, so we are left to our speculations and the Kursk clambake of 2024 Makes things worse for Russia. And in that setting China gets to be the big winner. OK, I admit, this victory would be largely held by the Chengdu Aircraft Industry Group (and supporting parties).

Have a nice day and feel free to watch American revenues move to the far east.

Leave a comment

Filed under Finance, Military, Politics

The misaligned cogs

This is a little hard. I just read an article on the Military hacks by North Korea, it doesn’t fit. Let me explain with a little time line.

2012
The Dutch had a press tour in North Korea. The Koreans confiscated temporary their camera’s and the Dutch were howling with laughter, they still had their iPhones and Android equivalents. They kept on filming. The Korean officers had no idea what a smartphone was, as such the Dutch had all the footage.

2014
Sony get hacked and soon thereafter we get all kinds of ‘leaked’ information. In addition within a year (I have no specific date) we get an amalgamated

The FBI later clarified more details of the attacks, attributing them to North Korea by noting that the hackers were “sloppy” with the use of proxy IP addresses that originated from within North Korea. At one point the hackers logged into the Guardians of Peace Facebook account and Sony’s servers without effective concealment. FBI Director James Comey stated that Internet access is tightly controlled within North Korea, and as such, it was unlikely that a third party had hijacked these addresses without allowance from the North Korean government. The National Security Agency assisted the FBI in analysing the attack, specifically in reviewing the malware and tracing its origins; NSA director Admiral Michael S. Rogers agreed with the FBI that the attack originated from North Korea. A disclosed NSA report published by Der Spiegel stated that the agency had become aware of the origins of the hack due to their own cyber-intrusion on North Korea’s network that they had set up in 2010, following concerns of the technology maturation of the country.

The sources were the New York Times, Times magazine, The verge and CNBC. I had issues with the release of information, but my issues were speculative and based on the Dutch field trip to Korea

2017
In ‘The Good, the Bad, and North Korea’ (at https://lawlordtobe.com/2017/09/30/the-good-the-bad-and-north-korea/) I wrote “I got this photo from a CNN source, so the actual age was unknown, yet look at the background, the sheer antiquity that this desktop system represents. In a place where the President of North Korea should be surrounded by high end technology, we see a system that seems to look like an antiquated Lenovo system, unable to properly play games from the previous gaming generation, and that is their high technology?” This is my second opposition. Between 2012 and 2017 they had apparently gained the ability to produce their own smartphone. This is realistic.

2024
Now we get “North Korean hackers have conducted a global cyber espionage campaign to try to steal classified military secrets to support Pyongyang’s banned nuclear weapons programme, the United States, Britain and South Korea said in a joint advisory on Thursday.

The hackers, dubbed Anadriel or APT45 by cybersecurity researchers, have targeted or breached computer systems at a broad variety of defence or engineering firms, including manufacturers of tanks, submarines, naval vessels, fighter aircraft, and missile and radar systems, the advisory said” (at https://www.reuters.com/world/north-korean-hackers-are-stealing-military-secrets-us-allies-say-2024-07-25/).

My issue (still speculation) is two fold. In the first we get to se that the Sony Hack was apparently not North Korea, but the Guardians of peace (the Lazarus group). We see references to “links to” and a small byte that they are “Originally a criminal group”. It is my speculation that these criminal ‘masterminds’ are either Russian or Chinese. They cater to North Korea as it allows them to act freely and I would expect them to share whatever intel they get with North Korea.

Even if these formerly known criminals were behind this setting, the whole picture doesn’t add up. I reckon that we all work at our own speed, however when we see Reuters give us “one elite group of North Korean hackers had successfully breached systems at NPO Mashinostroyeniya, a rocket design bureau based in Reutov, a small town on the outskirts of Moscow.” I do not debunk that setting, but over the timeline I have seen (many might have seen it), it is possible that this last statement is a smokescreen. Was it breached or were the Russians willing to hand over that ‘victory’ to make them sound more of a threat? In addition when we see “The hackers, dubbed Anadriel or APT45 by cybersecurity researchers, have targeted or breached computer systems at a broad variety of defence or engineering firms, including manufacturers of tanks, submarines, naval vessels, fighter aircraft, and missile and radar systems” I mostly worry about the state of cyber security at our own shores. That they get breached by China or Russia is understandable, They are on par in technology with us. North Korea is not. It is like a hacker with an 80282 AT computer, a processor from 1982 coming up to a server with a Xeon processor stating ‘gimme your data’ It is like a swimmer slamming a great white shark with a BB gun. Utterly ineffective. That is merely the hardware, These hackers would have lacked at least a decade of hacking skills. The NSA and GCHQ would be running circles around them. No, I believe that this is another player making North Korea their patsy. 

Now consider that all (or some) of my speculations are wrong. I get that, this is realistically possible, we still get the stage that the time line doesn’t fit. It is like going from an Apricot PC, to an IBM Q System One in a little over 7 years, without the required resources mind you. The other, more realistic, option is that defence and engineering firms have made a booboo and failed their cyber security requirements and now all avenues are racing to hide these facts. 

Can North Korea get to this point? Yes, that is possible, but it seems to me that ‘western’ criminals are using that place to hide their actions and loot whatever they can, whilst they part time hack into places and hand these secrets over to North Korea. OK, I am still speculating. However, remember that building in Russia filled with hackers? Russian forces had to intervene there. It seems to me that these hackers would like another place to work from. It doesn’t make China innocent either. They might have the same issues and these hackers also need a place to work from. In this story, I merely come to the speculated conclusion that the term ‘North Korean Hacker’ is almost an newly seen oxymoron. 

In all this the cogs are not aligned. In 1776 native American Indians got their hands on rifles. It took time to get good with them. In 1877 Satsuma Rebellion, led by Saigo Takamori faced Japanese forces with modern weapons, it took them time to adequately use these weapons. With the complexity of a system the time line expands. The timeline expands even more when excellence of a system is required. As such I feel that these technology skills do not fit the abilities of the North Koreans. But that is merely my point of view.

Have a great Friday, another 150 minutes until I have breakfast.

Leave a comment

Filed under IT, Media, Military, Science

The Iranian ploy

I saw the article (at https://www.newarab.com/news/houthis-threaten-riyadh-aerial-footage-key-airports) stating ‘Yemen’s Houthis threaten Saudi Arabia with aerial footage of key airports’, the New Arab with the text “The video, titled “Just try it”, contained images of King Khalid International Airport in Riyadh, King Abdulaziz International Airport in Jeddah, King Fahd International Airport in Damman as well as the ports in Ras Tanura, Jizan and Jeddah” is a possible ploy. I do not doubt that the Houthi’s (with generous support from Iran) is adding a ploy of threats to their limited tactics. It is clear that Houthi forces can bring something to the table, but I believe that this is nothing more than a ploy. A ploy that could have teeth, but I do not have the required contacts or information to see how serious this is. We see an additional setting with “The threat to Saudi Arabia by the Houthis comes amid reports that the government and Houthis failed to strike a fresh prisoner exchange deal”, which is fun because this was a deal between Houthis and the legitimate Yemen government. So this is all about posturing, or is it?

You see, a few hours later I was given through Arab News (at https://arab.news/6p5tn) ‘Iran’s new president vows balance with all countries, warns US his country won’t be pressured’ where Iran apparently made the claim “He looks forward to engaging in constructive dialogue with European countries”, so there is the carrot. Iran needs Saudi Arabia in a holding pattern, whilst Iran ‘appeases’ European nations. So as I see it Houthi forces are still the barking dogs of Iran and Iran needs this, because their support of Hamas will have secondary contemplations by any nation thinking that talking with Iran is a good idea. It has not now or yesterday worked and it will not work tomorrow either. 

As Iran is hiding their hands behind terrorist organisations like Hamas or Houthi forces, we need to be weary that stability in the Middle East requires both Saudi Arabia and the United Arab Emirates, they have the growing economies, the larger setting for tourism and the options of uniting Arab nations. The problem is that Iran is a problem. They are crying like little girls as they are denied a larger seat at the Arab table. The only small friend that Iran can rely on is Qatar and they have growing issues with Hamas. How that plays out is beyond me but in this setting we have Saudi Arabia, UAE, Egypt, Bahrain, Jordan, Oman and Iraq. They are all playing nice and as I see it, there is not to much love for Iran in this. Qatar is the one successful nation that has been playing a dangerous game, so what happens with them is up in the air. I reckon that the Houthi’s are set to the threat to Saudi Arabia. In this my feelings are that if one attack on a civilian target is done, the might of the Saudi forces will bluntly retaliate against Houthi forces. This has the one complication that Iran has to either commit or desert Houthi forces. This is the ploy as I see it. Iran cries loudly towards Europeans that they are so willing to discuss peace, but they are under the hammer. It will be something like that. So the Iranian ploy is unlikely to work. Europe has enough problems with Russia and Russia could be of little use to Iran. Russia has only one carrier left and they need it in their Ukrainian tactics. But this is about Iran. They are losing ‘useful’ friends a lot faster than they are happy with. It is in that setting that the Houthi threat is (as I personally see it) an Iranian tactic. 

They have to play nice with some people because they are about to learn the lesson Hector Malot taught us with ‘Sans Famille’ and Iran is rightfully worried. You see when the coins come down Iran will have to put up or shut up and they will lose a lot of face in the entire Middle East, sitting at a table where the stabilising points come from Riyadh and Abu Dhabi. That is why (my personal point of view) Iran need Houthi, Hamas and any other player that Iran can place in the field with deniability. It is why I said that whatever Palestine comes through, it will require the eradication of Hamas. Because it will be them who will terrorise the building projects in Saudi Arabia. 

So how can I prove any of this? Well the history of Iran is one. Their actions towards Houthi forces is another and the Iranian actions are right after the threats from Houthi forces. I feel that one ploy is enabling other actions. 

But for the most in this, I am merely speculating. So enjoy this Sunday.

Leave a comment

Filed under Military, Politics

In the beginning

Two issues came to light, the first one is about an American cop. The BBC gives us (at https://www.bbc.com/news/articles/c72ver6172do) where we see ‘A Bugatti car, a first lady and the fake stories aimed at Americans’. We are given “A network of Russia-based websites masquerading as local American newspapers is pumping out fake stories as part of an AI-powered operation that is increasingly targeting the US election, a BBC investigation can reveal.

A former Florida police officer who relocated to Moscow is one of the key figures behind it.” We knew this, it is nothing new. The Dutch company Trollrensics is actively hunting down trolls and illustrating all the fake news we see (well most of it anyways). This article brought a small art to light that requires actions by both Amazon, Google and Microsoft. You see the BBC gives us “But before the truth could even get its shoes on, the lie had gone viral. Influencers had already picked up the false story and spread it widely”. This is a dangerous setting. Influencers are all about the traffic, they mostly lack integrity and have no clue on the desire to gain followers and their desire to get their golden YouTube sign. 

It is time that the United States and the European Union start to pressure these tech firms to chastise these influencers. If they cannot give ample validation of how they got the evidence how they verified the authenticity they get the full brunt of the consequences. If they are found spreading fake news, their Google rating is diminished, their video’s are all downgraded. And their video’s are skipped in searches unless a person asks for this (former) influencer by name (at which point several people can find the seekers). It is a little crude but the Russians are becoming too much of a nuisance. Oh, and by the way if they follow through on the threat to bomb the Netherlands, I will put my nuclear deterrent (a solution to make a nuclear reactor meltdown) on every BBS in Chechnya. See how they like that condition. Russia made enough enemies, if they have to protect every nuclear reactor in Russia they will lose 15% of their deployable troops protecting buildings they never had to before. Actions are needed and no one is doing them, they are all concerned with the bottom line. You see spreading fake news and false information is not a freedom. In this day and age it is a duty of everyone to not spread fake news and misinformation. Now I understand that not everyone is able to distinguish fake news from real news. I usually seek two official sources (the Guardian, BBC, Al Jazeera, Arab News, Washington Post, Boston Globe, LA Times) there are more but you get the gist. The complication is John Mark Dougan, an American ex-cop. Just questioning. Why would anyone in Florida relocate to Moscow? No matter how valid his reason is. As we are given “an AI-powered operation that is increasingly targeting the US election” we are given the notion that this is all about Trump (my speculation) and it goes from bad to worse. As such I need to do something. I am not a man of action (when you pass the 60 mark that happens) but I have a decent imagination to look outside of the box. Russia has 38 active nuclear reactors. They collectively have 200,000 people working there. Consider that the Russians would need to check them all, secure them all. That implies thousands of troops. Then they need to inspect all new arrivals. It will be a nightmare I reckon. In the mean time they face Chechnya and Pro Ukrainian Russian troops. Plenty to worry about and with the solution out in the open, the Russians get a new danger and optionally their other enemies come out of the woodwork. 

But that is another matter. For now we need to take care of the influencers. They are the first hurdle to stop traction of fake news. In this Amazon, Google and Microsoft could change the rating of anyone spreading fake news, Google especially. Put their ratings to minus 150 and the influencers seize to be a relenting problem. Remove these accounts and their flocks disperse. Now I am not sure if Google can do that. You know that any account holder of a Google/Youtube account has rights. Just changing this on the fly does not go over well. But Google can stop the fake news from spreading, they can also look at the followers of that influencer. But I get ahead of the issues. Something needs to be done and not enough (as far as I can tell) is being done. 

Enjoy the day.

Leave a comment

Filed under IT, Media, Military, Science

The unspoken call

There was a call in Reuters last week. I had seen it, however I was dealing with the intelligence I was able to lay my hands on. It seems like a simple exercise but it is not. The article (at https://www.reuters.com/world/middle-east/un-experts-urge-all-countries-recognise-palestinian-statehood-2024-06-03/) gives us ‘UN experts urge all countries to recognise Palestinian statehood’, it seems so simple. Yet it is more complex than you think. You see that setting might be acceptable AFTER Hamas has been eradicated and the west knows this. You see Hamas is a one trick pony, it resorts to violence only ad at present it does so through Iranian guidance. If Palestinian statehood is awarded whilst Hamas is still in charge, all bet are off. The west knows this and they don’t like the centrepiece of Arabian stability. There is Saudi Arabia and the United Arab Emirates (UAE). That one trick pony (Hamas) will come with its new rule. A bigger seat at the Arabian table. When they do not get it Saudi Projects will suffer. The Line, Oxagon, Trojena, Sindalah, Red Sea International Airport, Mukaab, Qiddiya and a few more will subtly be suffering set backs, optional outright sabotage. That would cost Saudi Arabia billions. In addition UAE locations like Dubai and Abu Dhabi will be hit. It will not be some case of speculation, Iran does not like the path Arabia is on. It does not allow any path where they are an inferior setting. And they now have their claws in Hamas and Houthi forces. 

As such Hamas needs to be eradicated. It is simplest if Israel does it. It could do with the win and Saudi hands will remain clean. When Saudi Arabia and the UAE are forced to act the result will be destabilisation for years to come. All what Saudi Arabia had achieved will be for naught. The UAE will likely get a hit on tourism and travel, but there too the impact will be felt. The west likes this. They are trying to rally against China and the Arabian players are part of Brics now, catering options for China. All options are largely lost to the west. So they are now calling to include Palestine into everything. A call that is too rash for words. 

We can think all we can on Palestine, but they let Hamas in and did not do anything about Hamas for 2 decades. Hamas is under their buildings, part of their infrastructure and they have grown the next generation of Palestines to be terrorists too. The west did little to nothing, they figured that Israel would deal with that problem. Now that Israel is, the anti semitic rhetoric is taking global proportions. And the media was quiet for too long on the 120 hostages and they trivialised matters. So now that the gloves come off there will be another setting. If Israel succeeds in eradicating Hamas, statehood for Palestine could follow, yet with a few clauses. Any new Hamas interference will result in economic sanctions. In support of this other economic means will be required. Also Egypt will have to show it hands and allow Palestinians through. You know, I do not think this will happen. Egypt had identified the threat that Hamas and Palestine sets. Why do you think that they put a wall there? No one is questioning that part. It is all about Israel. 

If Israel does not succeed and statehood is awarded to Palestine, Saudi and UAE intelligence will have to beef up operations. Saudi will have a lot more riding on this and whilst there are upsides for Saudi Arabia, the risks are a lot higher. In the mean time Hamas leadership is still comfortable in Qatar and Iran has lines out to them. I wonder what will come to a close first. Israeli patience, of Saudi patience after statehood is awarded. 

In the end part of this is speculation, but the premise is sound and when Iran flexes its financial muscles towards Palestine, Saudi interests in Saudi Arabia will come under pressure, and it will resolved by giving a bigger seat to Hamas, the Iranian tool. A setting that we must avoid, the west especially. The west might no longer be a global strong power, but when chaos hit the Arabian peninsula, only the greed driven parties will see it as a plus point. The rest will suffer the consequences. And in this the media will shrug it off saying they merely reported on it. But the media will be every bit as guilty as anyone else. Even more so as they decided to not inform the public and filter events to what their stakeholders share holders and advertisers required. But the media will not report on that. I wonder why. 

Leave a comment

Filed under Media, Military, Politics, Tourism

Where to spend it?

I saw a report on the CNN site a few days ago (at https://edition.cnn.com/2024/05/23/politics/senators-trudeau-letter-defense-spending/index.html) Now, I get it, every nation needs to get their defence correctly. However with the message ‘US senators write to Canada’s Trudeau asking him to meet 2% GDP defense spending commitment’ and the 23 senators may have a point, we all have to carry our weight. But I believe that the US is expecting Canada to hand that money to south of the border. I am not on that horse. I think that Canada, if spending anything that is essential will turn to the UK and Australia first for their needs. The question isn’t merely what not had been bought. They question becomes “What needed to be bought?” I don’t have those answers. And Canada does not stand alone. In all this Spain, Turkey and the Netherlands are on the same horse and the pie of revenue is dwindling down, it means that there are more hungry mouths to feed. This means that there are options is both the Commonwealth and the EU. I wonder when these 23 senators start realising that their defense revenue might be in jeopardy. In this age of economic stress, just handing it over to the US might not be the wise choice. If possible Canada should consider the UK for initial choices. The US sets up the 2% clause hoping that it will come to them, but that is not a given. No matter how this works out. These nations need to set a stronger manifest on what is needed and on what is required. Now, this is hard because defense elements aren’t really public information, but the fact that 23 senators give a letter with the underlying “they believe Canada — unlike other nations — does not appear to have a plan in place to hit the target, a congressional aide explained.” I have to ask what evidence is there? And the fact that a US congressional aide comes forth with this is secondary. So how did this get ‘leaked’ to CNN? Do Canadians know how their defense systems fare? Just a few questions that come to mind and I wonder what plans are set to those F-35 Canada ordered earlier. 

It is not enough to consider that 2% needs to be spend, the question becomes where to spend it and on what.

Leave a comment

Filed under Finance, Military, Politics