Category Archives: IT

Wanna be rich?

This is a setting that is not for me, I am not a programmer, I do know my limits. I had a need and on the iPad (first generation), I had a data vault, it worked perfectly, but not anymore, now that I have a 4th generation iPad Air, I found the funny side of Apple apps (it is an actual joke). When investigating the new apps, I found well over two dozen other ones, yet they are all copies of one another, all giving us pics of sexy ladies and the owner of the app (most likely a man), that person needs to keep the images of his neighbours daughter a secret. Most of them all having the same idea, none of them acting on business principles. 

You see, an actual data vault have 2 elements, the first is the iPad, that is the vault that needs to hold the data, the provider (any laptop) needs to synch and there the issue starts well over 50% relies on a camera roll, the rest on other means (all equally useless), then there are a few apps that require a monthly fee, none of them get it, all of them in the naughty picture mode, yet there is a whole range of consultants that need an actual vault.

As you see in the image, there is a USB stick (or network location) that the computer or laptop can access. That links to the iPad. Yet there is no good link and the links that are offered, so far none of them properly work. And there the foot becomes even more uncomfortable. You see, it is not merely images, the folder needs to contain JPG, PDF, MP3, MP4, MOV, XLS, DOC (optionally), es well as TXT files. Consultants come in many forms and directions, from accountants and actors through to X-ray Technologist, they all have projects that need to be kept ‘hidden’ only shown to a chosen few. It can be any sort of project, but the people (like me) do not trust anyone and there can be no copies out in the open, so we need a data vault, we need to load USB sticks (or network directories) and there is no trust in the cloud (not with well over 90% of cloud transgressions). 

And none of these data vaults seem to understand that, so there is not one app, there needs to be two apps, one on the computer, one on the iPad, the computer links to the iPad and that is the setting of an actual data vault, the app makers that act on cool are missing millions in revenue, I would happily pay the $10 for that and hundreds of thousands of consultants as well. Consider the tens of thousands of real estate agents who settle the deals for dozens of houses and apartments going well into the tens of millions of dollars. New York at any given time have well over 4,000 places and most of them are set to ‘Price on request’ and a few other restrictions, and those estate dealers are merely one in a very long line of consultants that have an actual data vault need. Customer and client details that they need to keep hidden, so that a stolen iPad leaves the thief with nothing. 

That is the app that is needed and no one figured that in Apple land, so who else is missing parts in all this? Oh, and I know that there are other tablets, but most of us all use iPad.

Leave a comment

Filed under IT, Science

Greed v Agony: 1-6

We see the set, we see the result, yet we do not understand the equation. The media is mulling it over, it is in despair on what to do. They have so many voices to listen too, producers, executives, stake holders and share holders, none can agree on the story and more precise, most of them are clueless on what the story is. Reuters gives us ‘SolarWinds hackers accessed Microsoft source code, the company says’, the story (at https://www.reuters.com/article/us-global-cyber-microsoft/solarwinds-hackers-accessed-microsoft-source-code-the-company-says-idUSKBN2951M9), gives us plenty, but are they giving us what we need to know? Even as we are told “It is not clear how much or what parts of Microsoft’s source code repositories the hackers were able to access, but the disclosure suggests that the hackers who used software company SolarWinds as a springboard to break into sensitive U.S. government networks also had an interest in discovering the inner workings of Microsoft products as well”, a stage that is a lot bigger than anyone knows, some cyber experts have an inkling of thought on just how bad things got, but they do not know just how bad, because we do not know what was accessed.

Back in Time
So as we consider that on December 13, 2020, The Washington Post reported that multiple government agencies were breached through SolarWinds’s Orion software. So this is when the worm got out, yet I believe that the first instances were early August, I cannot prove this, but that is when the first event took place, they were merely not seen or identified as such. As far as I can tell (through unconfirmed and slightly dubious sources), there was a mapping phase in play and it was in play for weeks. This mapping phase was not contained or limited to the US, or to governmental players. It was also not the first time it happened, but it seems it was the most complete and most successful attempt, and it is about to get a lot worse. You see, people didn’t learn from 9/11, from all these people who went to flight school just to take off and learn how to fly into buildings, they didn’t learn the first time, and they are not learning now (at https://www.youtube.com/watch?v=lZAoFs75_cs), it gets to be funnier, the ethical hacker is topped by another advertisers, offering the same with 75% discount, and would you know it, all these ‘new’ ethical hackers, what are the chances that a few have their own agenda? Now these people are not ready to take over Solarwinds yet, but they are en-route.

A lot of hackers started as ethical hackers and then didn’t end up with a decent job, they had to make ends meet, and would you know it, they had just the education to make that happen. So as they didn’t get high paying positions at Google, Apple or Sun systems, they decided to take the reins themselves. They do have their competitors, people who graduated from London Poly, or Moskovski politekhnicheski universitet an a few others, all having graduates and the world had no positions for them, so they became the new managers of another version of Ransomware, or some other solution. It was only 5 years ago that we saw “Trend Micro released a research paper about sextortion: the means through which cybercriminals obtain compromising personal images or videos of Internet users – which they then hold hostage until their demands have been met” and that was if you were lucky, the idiots that most governments have include idiots that put the national security and defence issues on a USB stick. 

Time flies when greed is in charge
Over the last 5 years we saw an abundance of issues, yet the greed driven idiots all had a bottom line and cost is not part of that bottom line, it is actually against it, that was what some of these executives were screaming. And as things were pushed back quarter after quarter, the setting became that nothing was done, so when SolarWinds was transgressed upon the bulk of all corporations had no issue to see just how screwed they were, the sales people needed their bonus structure and so do the board members, as such there was for the most no defence. And it gets to be worse, even as we all want to blame SolarWinds, we need to realise that anyone with a lack of defence only has itself to blame. This is why I took certain defence matters into my own hands and even as they are not perfect, it beats no defence at all. When the Telecom Companies start to scream murder because usage is out of control and the numbers start showing that 100,000 people used 200 GB, all whilst the numbers showed that for the most the average of 50 GB, we will see another issue, the loss of telecom data and more important, our financial records will not match up, and at that point you will see a stage where our data is up for sale and there are plenty of interested parties who want that data. A setting of 5 servers that can be used multiple times and 25 customers all willing to pay $10,000 for the usage records of 100,000-350,000 people, and after the financial data is aggregated, they can collect a lot more from another 40 customers. It boils down to $250,000 for a month of work, and that is merely one segment, once these people hit companies (especially those with underfunded IT departments), The numbers will add up larger and faster, especially when IP data is made available, by the time the companies learn just how intense the pull of data was it will be too late and for the most the global police settings will not be able to cover it, the US has an FBI who can get to the matter to some degree, but they still think that North Korea did the Sony gig, so I am not holding my breath on that one. And that is before they realise that I devised another setting that explains the inside job part and I found a new way of exporting that data, which took less than an hour, the shareholders who needed a patsy in North Korea are that much in the dark at present and for the last 7-9 years actually.

So whilst the sales people are in the push for revenue, I reckon that only the companies that have a CTO on their board of directors will have a decent chance, the rest is cannon fodder, it is basically that simple.

The greed drive looks that good, but in reality they are losing 6:1 at present, SolarWinds is merely showing the agony that is out there, it is ABC News that gives a much larger timeline, with ‘Malware may have been installed in June’, which does give voice to my timeline, but it is not enough, we see the larger stage with “the hackers piggy-backed on the company that made software running on hundreds of thousands of corporate and government networks” and in all this, where was the security of SolarWinds? I believe that the damage is much larger and the players just do not know what to trust and who to trust, and that will stay with them for the larger extent of 2021, implying that their systems will not be properly cleaned for a much larger time, because they look at the larger setting, but this pass over will hit EVERY system, and it will hit a few systems in different ways, because they will get found out in a few ways, but not in all ways and that is why the agony score is so high and all this before someone realises that their cloud system could be just as infected and that is another piece of cake entirely, one that does not clean up so easily. 

So whilst we see the trivialisation of “it says patient information was not stolen” or “there was nothing to suggest customer data had been accessed”, it is the basic defence of any company or government organisation, but in reality they are decently clueless on what data was accessed and how it was copied or positioned in a place they can get to. For example it might not show, but when you realise that a person was using 12-17 GB of data during the day, so why is that person’s account using this data on his sick day? Odd is it not? There are a few more examples, but I let you simmer on this, because 2021 has a few more surprises for all of you, perhaps for me too.

Leave a comment

Filed under Finance, IT, Media, Science

Historic view versus reality

We all seem to have views, it is not wrong, it is not bad it is not evil, it merely is. I saw in 1998-2002 how governments sat on their hands, how lawmakers sat on their hands (and optionally on their mistresses) and they all vocally agreed that hackers were nothing more than a nuisance, and as I see it the traitor Bradley Edward Manning (aka Chelsea Elizabeth Manning) gave up secrets that it was not allowed to reveal and gave it to the world. There is no doubt on guilt, there was no doubt on treason, there merely was the act and that was that, it was the first moment where governments got the first clear hint that hackers were a much larger danger. After that came Julian Assange and Edward Snowden. Julian might be many things, but technically he was not a traitor. Edward Snowden was one, and the law again disregarded the steps that were taken, he went intentionally to a place where he might get the most value out of his deeds, Russia picked him up, just to piss of the US, which they were speculatively allowed to do, yet the stage is rather large, more hackers, all under the guise that the law saw them as a mere nuisance, we all got introduced to ransomware, now we see governments hacked through a sunny breeze (Solarwinds), and the voyage does not end. Now we see less than a day ago ‘Hackers threaten to leak plastic surgery pictures’, as well as ‘National Security Agency warns hackers are forging cloud authentication information’, now I do not care for the plastic surgery part, but it is another case where personal and person inclined data is no longer free, the two elements also give a rather large stage for us to place a new premise. One could now argue that hackers are the clear and present danger to personal and corporate needs and as such they can be hunted down and put t death. So from nuisance to global danger, as such when all these mommies cry that their little boys did not know what they were doing, I have no issues putting a HK model 23 to their foreheads and executing them (optionally with silencer as to not scare the neighbours). 

I think it is time for lawmakers and government administrative types to wake up and smell the situation, and in this, perhaps some remember the words of Martin C. Libicki in Newsweek (2015) where he pushed the view ‘Cyberattacks Are a Nuisance, Not Terrorism’, well that is not really true, is it? When we see the definition of terrorism we see “The unlawful use of violence and intimidation, especially against civilians, in the pursuit of political aims”, there we see two parts up for debate, the fist is that ‘mental violence’ is still violence and the setting of intimidation is already achieved, the stage we still need to address ‘the pursuit of political aims’, not all terrorism is set to political aims, unless if you call self-enrichment the pursuit of political aims. 

And with ‘National Security Agency warns hackers are forging cloud authentication information’ we see an initial stage where commerce will come to a screeching halt. My IP does not cover for that, darn. But there is the old way (1981-1991), just kill them, be done with it. 

Now some (especially in law) will state that I am overreacting, yet am I? It is the lawmakers that could optionally be seen as cowards, hiding behind their golden calf called jurpisprudence. The law, for the most does a good job, it is not perfect, so be it, but for the most, it is OK. This covers the never trespassers and the limited trespassers, they make up for 75% of all people, then there are the criminals, 24.99%, the law takes care of them, they are repeat offenders, career criminals and as such the law was designed to deal with them, then there is the remaining 0.01%, these criminals are in it for the kill, to create a maximum amount of cadavers physically, mentally and financially, to make life for nearly all impossible, and that golden calf, the law cannot deal with them and we accept that, so we remove them in other ways. We hunt them down and put them to death, and when it is some 16 year old claiming he didn’t know what he was doing, we know, he did it to seem cool, he was willing to make all others suffer, just to look cool, to get the tits, to rub the vagina, his friends never could, as such there is a 9mm solution that solves it, if only his parents had raised him right. 

You think I am kidding?
You forget the poverty line is shifting massively because of COVID-19 and soon the insurances will not cover the impact, the media will merely snigger and cash in on all those clicks they got from the $x donation to an unnamed source, and it is now time to make the long overdue change, before governments are pushed to take away more and more of our freedoms, which will push us into the dark-web, a situation these criminals would love. And it is close to 15 years too late, but in this case it is better to be late to the party than not get there at all. 

Am I overreacting?
That would remain a fair question, I do not believe so as this step is well over a decade overdue, it is not something that was pushed to the top in the last few days, and it is partially due to governments and lawmakers not acting when they could have and especially when they should have, now the dike is levied and people are soon to be drowning and something must be done. From my point of view, to hit terrorists, you hit them harder, so the more extreme you hit these hackers, the clearer the message becomes. And a clear message is years overdue.

In this there is a two step setting, there are the “cool wannabe’s” who are mot likely teenagers, some of them are easy to find and after the first examples a lot of them will hide like cockroaches, but the second tier, the one the media and governments intentionally ignore are those in organised crime, they will be the real challenge and as most governments have nothing on stopping them, at best they can limit the damage, which is basically no solution, that gap will take time, but with ‘hackers are forging cloud authentication information’ less than a week old, there is now a chance that the NSA and other intelligence networks will realise that compromised clouds will have global commercial implications, as such governments must now act, the moment any cloud is openly seen compromised, it will be too late for well over a decade. It becomes a clearer situation  when you consider that global e-commerce was set to ‘Global e-Commerce hits $25.6 trillion’, by the United Nations Conference on Trade and Development (UNCTAD), s how much losses must global commerce endure before we act? Oh and if you think that this is the end? How much more powerful will organised crime become if they only get their fingers on 0.1% ($25,600,000,000)? It will become a sliding scale that goes from bad to worse, and governments knew that, they knew for well over a decade, but their delusions saw other non-solution, like perhaps, it will go away on its own, so tell me when was that ever a solution?

1 Comment

Filed under Finance, IT, Law, Media, Military

When a scary dream is more

A lot of people have them, I do too, I just hd one and it scared me awake for some reason, and even now, one of the elements is already gone and my mind is fighting to hold onto the other thought, even though I am wide wake. It seems like the dreams are not giving up their secrets that easy, and it is a little bewildering. 

So here I am, in my dream, I meet a nice woman, she seems really nice, friendly and confused. She is confused as people are not calling her back and that is where this part is taking us, what we are not told. Changes that are a stage of what people think we should not need to know.

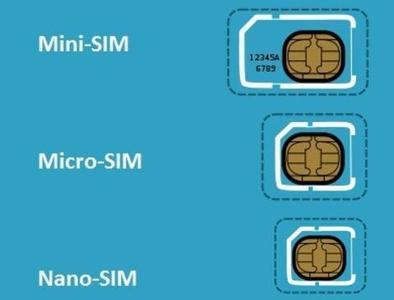
In this dream, I am learning that she has a 5G sim in her 4G phone, it seemingly works, but it only partially works, in the rear there are members of a nefarious organisation and they seemingly are aware that it would be possible to capture peoples hardware, autoforward their hardware and leave the owner unsuspected, a setting for large amounts of identity theft in 2023, as the bulk of our lives are going through a different device. You see, that thing you hold, that brick, that piece of plastic, it is not your mobile phone, not anymore. It has become your personal dat server and that is in this age a bit more powerful than you imagined and under 5G, taking a hold of finances and other means when you pump them through your mobile has consequences. So as I am pondering the dream, I see flares of the second dream. There I meet up with an old boss, he is wearing an old uniform jacket, like a bolero for men, shutting at the waist, the old Dutch uniform jacket of 1975-1980, some used to love them. The only thing I remember is that he had to remain aware in every room where the emergency exit was, it all went a blur after that, so here I am awake trying to figure out my delusions. So I started looking and through were several sources that are not worthy of mentioning, but Ericsson, with his setting gives us “The simple answer, under certain assumptions, is no. However, a complete answer is nevertheless trickier than just a yes or a no”, why can they not answer it: “Yes, if you have…. And no if you have the following situation”, why did I have to take notice of ‘a complete answer is nevertheless trickier’. 

And actually, their answer is surprisingly complete, and as I give you “While accessing the 5G system is one thing, the question we have is whether using the “new” security and privacy features of 5G requires a new kind of USIM other than Rel 99+ USIMs which could be used for 4G security. This is a valid question and something which we address below”, as well as “In 5G, subscription permanent identifier (SUPI) could be in two formats, one is the legacy format called international mobile subscriber identity (IMSI) and another is the format newly adopted in 5G called network access identifier (NAI). Furthermore, 5G provides at least two methods of authentication and key agreement (AKA) for accessing the network. One such method, 5G AKA, is an evolution of the authentication method in 4G. Another, called EAP-AKA’, is a method now widely adopted in 5G for broader use of the Extensible Authentication Protocol (EAP) framework”, which is interesting, I never knew any of this, I am literally learning this as I write the article, so why was the dream so unreal and partly scary? This is when I see “from the IdaM viewpoint, the Rel 99+ USIMs that could be used in 4G are still compatible with 5G, in that they can be used to authenticate and gain access to the 5G system. The main reason for this forward compatibility is the fact that there is no need for a new permanent security key shared between USIMs and the network”, as well as “5G has introduced significant privacy enhancements in terms of how permanent and temporary identifiers are used”, this optionally sets the stage for something really scary. What if the SolarWinds debacle is merely a test-run in getting some parts out there, optionally undetected? What if there is a run on copying all the data in some way because, as we see here ‘4G are still compatible with 5G’, I merely wonder what else is possible and why the dream scared me, more important, I knew nothing of this before now so how does my dream know? I have never seen an actual 5G sim before today, and as I see some of them, they are all vastly different, it also implies that the sim touches different points, in different cases, and I know that what I am seeing is marketing driven, but where is the reality? More important, what is the danger I dreamt of? If a person’s phone can be hijacked WITHOUT the owner knowing, what other dangers are their for their personal data servers? I worked on the IP to lower that danger, but it was merely a consumer driven IP, which aligned perfectly with something else, and here I am seeing that there is a danger, optionally merely a delusional one that is in the background, so I can pretty much kiss this night of sleep goodbye. 

Still, only 2 days left to get my groceries and most is done, but some parts I tend to leave to the last moment, that tends to be me. You see on the 24th many groceries start pricing down the stuff they cannot sell on the 25th for some reason and that is where my little profit is.

Still, my dreams seldom throw me to this degree and to be honest, when it comes to dreaming high tech and gorgeous women optionally scantily clothed, I still go for option two, even though I stopped being a teenager some time ago, well that’s me and for now I am considering something on branding for tomorrow, or the 25th, something happened and it puzzled me, but it is always a decent reason to dig into the matter and that I what I might do, yet for now, there was something on the dream that was more than delusional. It is not merely on what was done without our consent and knowledge, what happens when options like that become a larger stage of exploitation? What happens when EVERY sim is the first part of a tracker and 5G pushes us to allow for more, all whilst the evidence against us is legally not allowed to rely on data points to help prove our innocence? I will leave you to ponder on that element of the equation.

Leave a comment

Filed under IT, Science

Once more for the whiners

It started in 2018 when I wrote “A certain play performed by adjusting to the notion of stupid and short sighted whilst the captains of industry have been getting their A-game in gear and others never did. It is merely another stage of the impact of iterative exploitation and profit founding, that whilst Huawei, Google, Apple and Samsung are no longer going iterative, they are now making larger leaps over the next 5 years as they want the largest slice of 5G pie possible and in an iterative setting the others can catch up and that is where we see the clash, because these hardware jumps will also prevail in software and data jumps and some players are in no way ready to play that game”, there was a malleable situation that came to fruition 2 years later. I saw it coming, and whether it was Google Cloud, Microsoft Azure, or Apple iCloud (that selfish title), one would reap the benefits. Of course there will always be the negative shouts (on how nut I am), yet less than one hours ago, we see Reuters give us ‘Aramco to bring Google Cloud services to Saudi Arabia’, a stage that was always going to happen and it serves my IP as well, so I merely have to wait, like a spider in the middle of his web. Two years of anticipation about to pay off massively. The article came as ‘Clueless to the end’ on that October 12th and now we get the setting where Microsoft and Apple are basically second to all. 

So as we now see “Aramco said Saudi Arabia is being added to the global network of Google Cloud Platform regions, as part of a strategic alliance agreement signed between the company and Google Cloud this month”, this also means that it can test apps in 5G at full speed in a national setting, implying that the advantage of Google makes more and more headway, this is not about the foresight of Google, it is for the most the lack of foresight to all the other players that scream that they are treated unfair and the large tech companies must be broken up, here we see a stage I foresaw 2 years ago, several people were all up in arms how I didn’t see it right, larger tech companies in a lack of action and here is the advantage that Google now has, and more importantly well deserved has.

So when we see the New York Times 21 hours ago and see in one part ‘The Antitrust Case Against Big Tech, Shaped by Tech Industry Exiles’, as well as “Regulators are relying on insiders like Dina Srinivasan, who left her digital ad job after concluding that “Facebook and Google were going to win and everybody else is going to lose.”” We see a stage of people in  stage of whatever (aka: lack of insight), this is further set in “before she became an antitrust scholar whose work laid the blueprint for a new wave of monopoly lawsuits against Big Tech, Dina Srinivasan was a digital advertising executive bored with her job and worried about the bleak outlook for the industry”, which is great, because as she was looking at the bleak prospect I came up with a new piece of IP for 5G, and it is something she could have thought of, but no she didn’t and now I have it (and she does not), so does it make me a genius and her average, or me creative and she a mere advantage seeker with no prospects to advance over, I would like to think it is one, but reality will probably set me in camp two. As such a larger stage is not merely the lack of foresight, it is a whole range of people in a stage of seeing what Google can come up with and how it fits their need for profit seeking, something that was decently clear in every attack on Google and its three tech accompli, a stage that the media milks but seemingly does not care to understand, but that is my take on the matter. As such, does Google matter, or was Google always the martyr? I think both, but the advantage seekers wanted google to suffer their non profits (they call them losses). Yet the stage is seen as per today that these players never looked beyond the length of their nose (we are excluding Pinocchio and Cyrano de Bergerac from consideration). Or in the language of Sergey Brin (Google’s own Papa Smurf), If we smurf what we smurf all the smurf, the smurf we smurf will be better than any other smurf.

So as we see (at https://www.nytimes.com/2020/12/20/technology/antitrust-case-google-facebook.html) “With no background in academia but an insider’s understanding of the digital ad world and a stack of economics books, she wrote a paper with a novel theory — that Facebook harmed consumers by extracting more and more personal data for using its free services”, no one is considering that whilst she had the advantage she was quiet, when the advantage went away she started to cry (well sort of) and now we see “she argued in another paper that Google’s monopoly in advertising technology allowed for the type of self-dealing and insider trading that would be illegal on Wall Street”, yes that is what the whiners say (as I put it with diplomatic eloquence), yet the truth is that there are two stages, what the people want, what WE seek and what advertisers push WHAT THEY THINK WE WANT, two very different settings and as they REFUSED to listen, because it was not a contribution to their bottom line, and as some of these digital weavers left things unsettled in 1995-1998 Google had an option and created a search system, one that simpleminded people could not conceive, in addition, in 1998-2000 the digital advertisement players sat on their hands, on their asses and kept on faltering, because their short sighted approach was making them rich and in 2000 Google Adwords came and changed it, they actually LISTENED to those who needed advertising and gave them options and choices, something the others never did, they had the conceited approach like the yellow pages and we merely had to shut up and pay the bill, Google Adwords gave options and choices and a massive way for us not to be taken advantage off, we only paid one cent more than the one before us, so if number 4 paid $0.37 for an advertisement, number three paid $0.38 (regardless of bid), number two paid $0.39 (regardless of bid) and number one, el jefe de advertencia paid $0.40 (regardless of bid), that as something the others NEVER offered.

So cry me a river, now Google Cloud is also in Saudi Arabia (via Aramco) and hopefully son my system will deploy for consumers and small businesses, all whilst the whiners say they are treated so unfair, I got an optional entire technology arm launched, so how we consider “they can articulate the specifics of what they worry about”, which they are allowed to do, but in that same time I came up with a new 5G technology, at that point, are the whiners really helping us, or stopping us from reaching innovative greatness, merely because they cannot fathom the options?

So whilst w might notice ‘The Facebook Antitrust Case Is a Vital First Step. But More Needs to Happen’ and accept words of a Smoking Gun, is there an actual progress by these whiners? Let’s not forget they were at the helm and let it slip, these executives were riding high and falling asleep whilst Chinese companies hungry for that much revenue are waking up and nipping at everyones heels. This might be a good thing, but those same whiners complaining about actual innovators is taking it one step too far, and as I am showing, that progress started to come in 2018, now that the Google Cloud is going there the others will wake up and wonder why they never thought of it. Well, I can tell you, it was the lack of vision that did not get you to Vision 2030, which was launched well over to years ago.

So there!

Leave a comment

Filed under IT, Politics, Science

Not for minors

OK, this is not the most subtle article I have ever written, but at times subtle just doesn’t do the story any justice, it happens. So this is a question to parents “If you have a daughter between 22-32, and she looks like Laura Vandervoort, Olivia Wilde, or Alexina Graham. Can I please fuck the bejesus out of her vagina?” To be honest, I don’t really need to, but it has been a while, so there. 

Are we all awake now? So consider ‘Facebook and Apple are in a fight. Your browsing history is in the middle’ (at https://www.nbcnews.com/tech/tech-news/facebook-apple-are-fight-your-browsing-history-middle-n1251612), apart from all the hackers getting access through Microsoft, we see another stage develop. The headline might not get you on board, so perhaps the by-line will “Facebook on Thursday ran its second full-page newspaper advertisement in as many days, attacking Apple’s plans to tell iPhone and iPad users when apps are tracking them online”, which implies that Facebook does NOT want you to know that apps are tracking your every move, and Apple does. It seems to me that Apple is in a stage to put awareness and security at the centre of your digital life, Facebook not so much. Now, I have no problems with Facebook keeping track of my actions ON FACEBOOK, but dos their ‘free’ service imply that they are allowed to do that anywhere I am? I believe that this is not the case and the money Facebook is getting is starting to feel tight around my digital profile, their actions had already made it important to delete Facebook software from my mobile phone (it was draining my battery), but the stage is larger and that is seen in the NBC News article (and a few others too).

So as the quote “Facebook on Thursday ran its second full-page newspaper advertisement in as many days, attacking Apple’s plans to tell iPhone and iPad users when apps are tracking them online” is given, how many of you are considering the following:

  1. A full page ad in the newspapers is pretty expensive.
  2. Facebook is seemingly untouched that multiple apps are following us.
  3. We are seemingly not allowed to know all the facts!

This is the big one “attacking Apple’s plans to tell iPhone and iPad users when apps are tracking them online”, so why are we not allowed to know what is being done to us, that we are being followed in a digital way and Facebook does not want us to be aware? This is where we see my (not so) subtle hint regarding your daughter and “fuck the bejesus out of her vagina”, how many fathers will be slightly less than enthusiastic? I get it, your little princess (your consenting and adult) little princess needs a knight on a white horse and always bring flowers and chocolates, have honourable intentions and to set your mind at ease keeps your daughter a virgin until the day she marries. It is not realistic, but parents are allowed to be overly protective of their princes and princesses. Yet Facebook seemingly does not want you to be in that park, they want you to be unaware of what is going on, and Apple drive it to the surface. So when we see “Apple is planning to roll out a new feature on its devices that will alert people when an app such as Facebook is trying to “track your activity across other companies’ apps and websites.” People will have options such as “Ask App not to Track” or “Allow.””, they did something really clever, if Microsoft (after they resolve all their hacks) does not follow suit, Microsoft stands to lose a massive slice of the consumer pie and that will not make them happy. I for the most am completely on the Apple side when we see “Users should know when their data is being collected and shared across other apps and websites — and they should have the choice to allow that or not”, I personally am realistic enough to see that Apple has an additional side to this, not sure what yet, but this is about a lot more than mere advertisements, I am however not too sure about what that is. When we see “Facebook uses data such as browsing history to show people ads they’re more likely to want to see, and to prove to marketers that its ads are working”, we need to realise that I would have no issues with any link opened within Facebook towards whatever we were going to in any advertisement. For example, if Facebook opens up a browser window, within Facebook and tracks the clicker, I would not completely be opposed to it, but Facebook realises that the data it I tracking is a much larger stage and I feel that this is not merely about “prove to marketers that its ads are working”, I believe that these trackers keep tabs on a lot more, keep tabs on what we do, where we do it and how we do it. I believe that it is a first step in the overly effective phishing attacks we face, Facebook might not be part to that, but I reckon the phishing industry got access to data that is not normally collected and I personally believe that Facebook is part of that problem, I also believe that this will turn from bad to worse with all the ‘via browser gaming apps’ we are currently being offered. I believe that these dedicated non console gaming ‘solutions’ will make things worse, it might be about money for players like Epic (Fortnite), but the data collected in this will cater to a much larger and optionally fairly darker player in this, I just haven’t found any direct evidence proving this, in my defence, I had no way of seeing the weakness that SolarWinds introduced. It does not surprise me, because there is always someone smarter and any firm that has a revenue and a cost issue will find a cheaper way, opening the door for all the nefarious characters surfing the life of IoT, there was never any doubt in this.

And in this, it was for them NEVER directly about the money, in this look at the ‘victims’:
The US Treasury Department, The US Department of Commerce’s National Telecommunications and Information Administration (NTIA), The Department of Health’s National Institutes of Health (NIH), The Cybersecurity and Infrastructure Agency (CISA), The Department of Homeland Security (DHS), The US Department of State, The National Nuclear Security Administration (NNSA) (also disclosed today), The US Department of Energy (DOE) (also disclosed today), Three US states (also disclosed today), City of Austin (also disclosed today) (source: ZDNET). It was about the information, the stage of a more complete fingerprint of people and administrations. It gives the worry, but it also gives the stage where we can see that Apple has a point and we need to protect ourselves, because players like Microsoft will not (no matter what they claim). In this I name Microsoft, but they are not alone, anyone skating around margins of cost are potential data leaks and that list is a hell of a lot larger than any of us (including me) thinks it is.

So whilst we look and admire the models, actors and actresses and we imagine whatever we imagine, consider that they are not a realistic path, a desirable one, but not a realistic one and that is the opening that organised crime needs to claimingly give you ‘access’ to what you desire whilst taking your data. It is the oldest game in the book, all wars Arte based on deception and you need to wake up, the moment your data is captures and categorised you are no longer considered an interesting party, you are sold and they move onto the next target. So whilst you get trivialised, consider that Apple has a plan, but whatever they plan, it seems you are better off on that side, than the one Facebook is planning. When was the last time that you were better off staying in the dark on what happens to your data, on what happens when others keep tabs on you?

And in this consider “Facebook is making a last-ditch effort to persuade Apple to back off or compromise with industry standard-setters.With offline ads in newspapers such as The Washington Post and The Wall Street Journal, the social networking company is trying to rally to its side the millions of small businesses who buy ads on Facebook and Instagram”, so in that quote where do we see any consideration on the people or us as the consumers? When we see “millions of small businesses who buy ads on Facebook and Instagram” where is the consideration that they should have for the customers who walk into their business? When you get in any shop what do you hear? How can I be of service? Or do you hear: What do you want? I let you consider that whilst you consider the position Facebook needs to have and consider that non digital advertisement never kept track of what other newspapers you were reading. 

We seemingly forgot that there is a price for the presence of IoT, Apple is making us aware of that. I am not silly enough that Apple is holier than though, but at least they created the awareness and the greed driven players are not looking too good today, are they?

1 Comment

Filed under IT, Law, Media, Science

Thanks for the support

We all have to say thanks, I in this case to the BBC, they were just able to give support to two issues that I put out in the open over a year ago (too tired to find these articles, they are at least a year old and it is 33 degrees Celsius at present (at 21:30), The first is the lacking approach to Common Cyber Sense within the US Administration, I found that failing in the Pentagon in 2018, I found Cisco routers still carrying the password Cisco123 in at least two sensitive areas and there was the use and abuse of non secured USB sticks in more than two sensitive places and on top of all that, the US ends up with an idiot in the White House relying on a password like MAGA2020, how bad do things need to get? I agree that the man Victor Gevers did everything right, including alerting the proper players, but this is a much larger problem. So when we see “The president’s account, which has 89 million followers, is now secure. But Twitter has refused to answer direct questions from BBC News, including whether the account had extra security or logs that would have shown an unknown login”, the quote forgets to give a larger part, you see, this was all on the user, when the user is thick as molasses and equally stupid, can we blame Twitter? And this now also reflects back to ‘6 simple questions’, which I released on February 3rd 2020, there we see the simple setting that the Daily Mail, the Daily Mail of all sources that there was a way to infect accounts yet no way to establish by who or how. It gets us back to the original question ‘Where is the evidence that Saudi Arabia infected ANY phones?’, a question that FTI Consulting and the United Nation essay writers can not inform us. It shows a much larger lack of cyber security and proper cyber defences, all whilst these so called investigators are happy to accuse whomever is a political and not a true target, is that too much?

I ended that article with question 6 ‘Why on earth is the UN involved in an alleged Criminal investigation where so much information is missing?’, now we see a new page turned, can any criminal investigation hold any water when the users are that thick? MAGA2020, really?

So when we consider “Mr Gevers also claimed he and other security researchers had logged in to Mr Trump’s Twitter account in 2016 using a password – “yourefired” – linked to another of his social-network accounts in a previous data breach”, in all this the need to employ Common Cyber Sense is a situation that becomes more and more essential and we need to catch on quicker than we are, because it is people like that who will claim things against Russia and China, whilst letting their security services in at their leisure because they cannot be bothered with Common Cyber Sense. 

As I see it, President Trump will optionally get two additional Christmas cards this year, one from 76B Khoroshevskoe Highway, the other from 14 Dongchangan Avenue, Dongcheng District, Beijing. Both will be stating “Thanks for the support”, what a lovely way to end a presidency and probably the first time that a US President gets a Christmas card from both locations.

Leave a comment

Filed under IT, Science

A political stage of nowhere

Less than an hour ago the BBC gave us ‘EU reveals plan to regulate Big Tech’, apart from the discriminatory nature of the stage, are they doing anything else than merely fuelling their own gravy train? Consider the news from last July, there we were given ‘Apple has €13bn Irish tax bill overturned’, a case that started in 2016, had Apple and the government of Ireland in a twist, when you consider “The Irish government – which had also appealed against the ruling – said it had “always been clear” Apple received no special treatment”, I am on the fence, and in this the European Commission wasted 4 years in going nowhere, in the light of that revelation, can we even trust the approach the EU has? When we look at the first option, we see ‘Online harms law to let regulator block apps in UK’, this means an almost immediate blocking of Twitter, Facebook, WhatsApp and a few more. Local laws have been ‘accomodating’ to large corporations for such a long time, that social media is caught in the middle (and yes they benefitted too), so they re now pushing for changes that end privacy, because that is a conclusion. If we hunt down the perpetrators, we need to coat the materials in identity revealing codes, in addition, the EU government will have to adjust laws to make the poster responsible for what they post and that will lead to all kinds of privacy adjustments (that does not worry me), yet when insurance companies will use that setting to see transgressions on social media and they demand adjustment by handing over the posted evidence, how long until people like Margrethe Vestager start realising that they were clueless from the start? The BBC article gives us “The law would give local officials a way to ask Airbnb and other apps to hand over information or remove listings”, which now puts some players on the dark-web and the chaos (and organised crime involvement) merely increases. For example, when we see “not use data gathered via their main service to launch a product that will compete with other established businesses”, how will that be proven and tested? By handing all data over to the government? How many frivolous cases will that grave train launch? How is it impossible to stop advantage seekers a stage where they use Margrethe Vestager and her gang of idiots to do the bidding of (optionally) organised crime?

Even though I spoke of the Accountability Act, a legal direction that could thwart a few issues from the start in June 2012, 8 years later and this group is hardly even on the track of resolving anything, only to get their grubby greedy fingers on data, the new currency. And in this, the tech companies have their own games to play as Facebook shows with “Apple controls an entire ecosystem from device to app store and apps, and uses this power to harm developers and consumers, as well as large platforms like Facebook”, what Apple does, IBM did for decades, what Apple does Microsoft did for decades, so where is that train station? So even as we see “And they may influence other regulators – in the US and elsewhere – which are also planning to introduce new restrictions of their own” we also need to realise that after a decade, the local and EU laws have done little to nothing to hold the poster of information to criminal account, it seems to me a massive oversight. And in all this there is no view that the EU will wisen up any day soon. 

So as I see it, this will soon become a political stage that goes nowhere and in all this these layers merely want their fingers on the data, the currency that they do not have. How is that in any way acceptable?

Oh and when we see the blocking of apps and localisation, how long until people find an alternative? An alternative that the EU, the UK and the US have no insight over? Will they block apps that interact with data centres in China, Saudi Arabia and optionally other locations too? I raised it in other ways in ‘There is more beneath the sand’ in 2019 as well as some issues in 2018, a setting that was almost two years ago, as such is it not amazing that we see a shortsighted approach to this issue, whilst I gave the option EIGHT YEARS AGO and the laws are still not ready? They are ready to get the data from Google, Facebook, Apple, Amazon and Microsoft, as such when the trial goes wrong, hw will these people be compensated for the loss of uniquely owned data, data that they collected over the decades? Will the stupid people (Margrethe Vestager et al) compensate per kilobyte? How about $25,000,000 per kilobyte? Perhaps we should double that? What will be the price and in this, we should demand that Margrethe Vestager and her teams will be criminally liable for those losses, or will the gravy train decide that it is a little too complex to hold one station to order, and let face it, that gravy train has 27 stops to make, all with their own local needs, their local incomes and their local digital wannabe’s.

When a setting like that goes nowhere, you better believe that there is someone behind the curtain pulling strings for their own enriching needs, that is how it always has been, as such, let me give you the smallest example from January 2020, there we see “‘DIGITAL CROSS-BORDER COOPERATION IN CRIMINAL JUSTICE’ CONFERENCE”, with the nice quote “The e-Evidence Project led by the European Commission, DG Justice and Consumers, provides for the e-Evidence Digital Exchange System that manages the European Investigation Order/Mutual Legal Assistance procedures/instruments (e-Forms, business logic, statistics, log, etc.) on European level. The Reference Implementation Portal is the front-end portal of the e-Evidence Digital Exchange System and is also provided by the EC”, yet this is only step one. In all this we can also include the EC (at https://ec.europa.eu/home-affairs/what-we-do/policies/cybercrime/e-evidence_en), where we see: “However, present-day solutions too often prove unsatisfactory, bringing investigations to a halt”, I get it, you will say, will this not resolve it? Well, consider “provide legal certainty for businesses and service providers: whereas today law enforcement authorities often depend on the good will of service providers to hand them the evidence they need, in the future, applying the same rules for access to all service providers will improve legal certainty and clarity”, in this we need to look in detail at ‘provide legal certainty’, which at present under privacy laws is a no-no, and the poster cannot be identified and cannot (and will not) be held to account. As well as ‘applying the same rules for access to all service providers’, still the poster remains out of reach and the local and EU laws have done NOTHING for over a decade to change that, as such, when we consider this, why should Google, Facebook, Apple, Amazon and Microsoft suffer the consequences, in addition we see the absence of IBM, why is that? Does it not have data collection software, it has data centres, it has cloud solutions, so why are they absent?

And in light of earlier this year, as we were told ‘Google starts appeal against £2bn shopping fine’, how will that end? The law remains untested in too many aspects, in this the entire data stage is way too soon and in that the blowback will be enormous, all whilst the EU (UK too) is unable to do anything about data driven organised crime, other than blame state operators Russia and China, consider the Sony Hack of 2011, I was with the point of view by Kurt Stammberger (before I even knew about Kurt Stammberger), North Korea lacks infrastructure and a whole deed of other parts. I also questioned the data, like “former hacker Hector Monsegur, who once hacked into Sony, explained to CBS News that exfiltrating one or one hundred terabytes of data “without anyone noticing” would have taken months or years, not weeks”, I even considered an applied use of the Cisco routers at Sony to do just that, all issues that North Korea just could not do and in that environment, when we see these levels of doubt and when we get “After a private briefing lasting three hours, the FBI formally rejected Norse’s alternative assessment”, which might be valid, but when we see a setting where it takes three hours to get the FBI up to speed, can we even trust the EU to have a clue? Even their own former director of German Intelligence, gave us recently that they did not fully comprehend Huawei 5G equipment, and they will investigate the data owners, al before the posters of the messages are properly dealt with? I think not!

Leave a comment

Filed under IT, Politics, Science

Within the mind

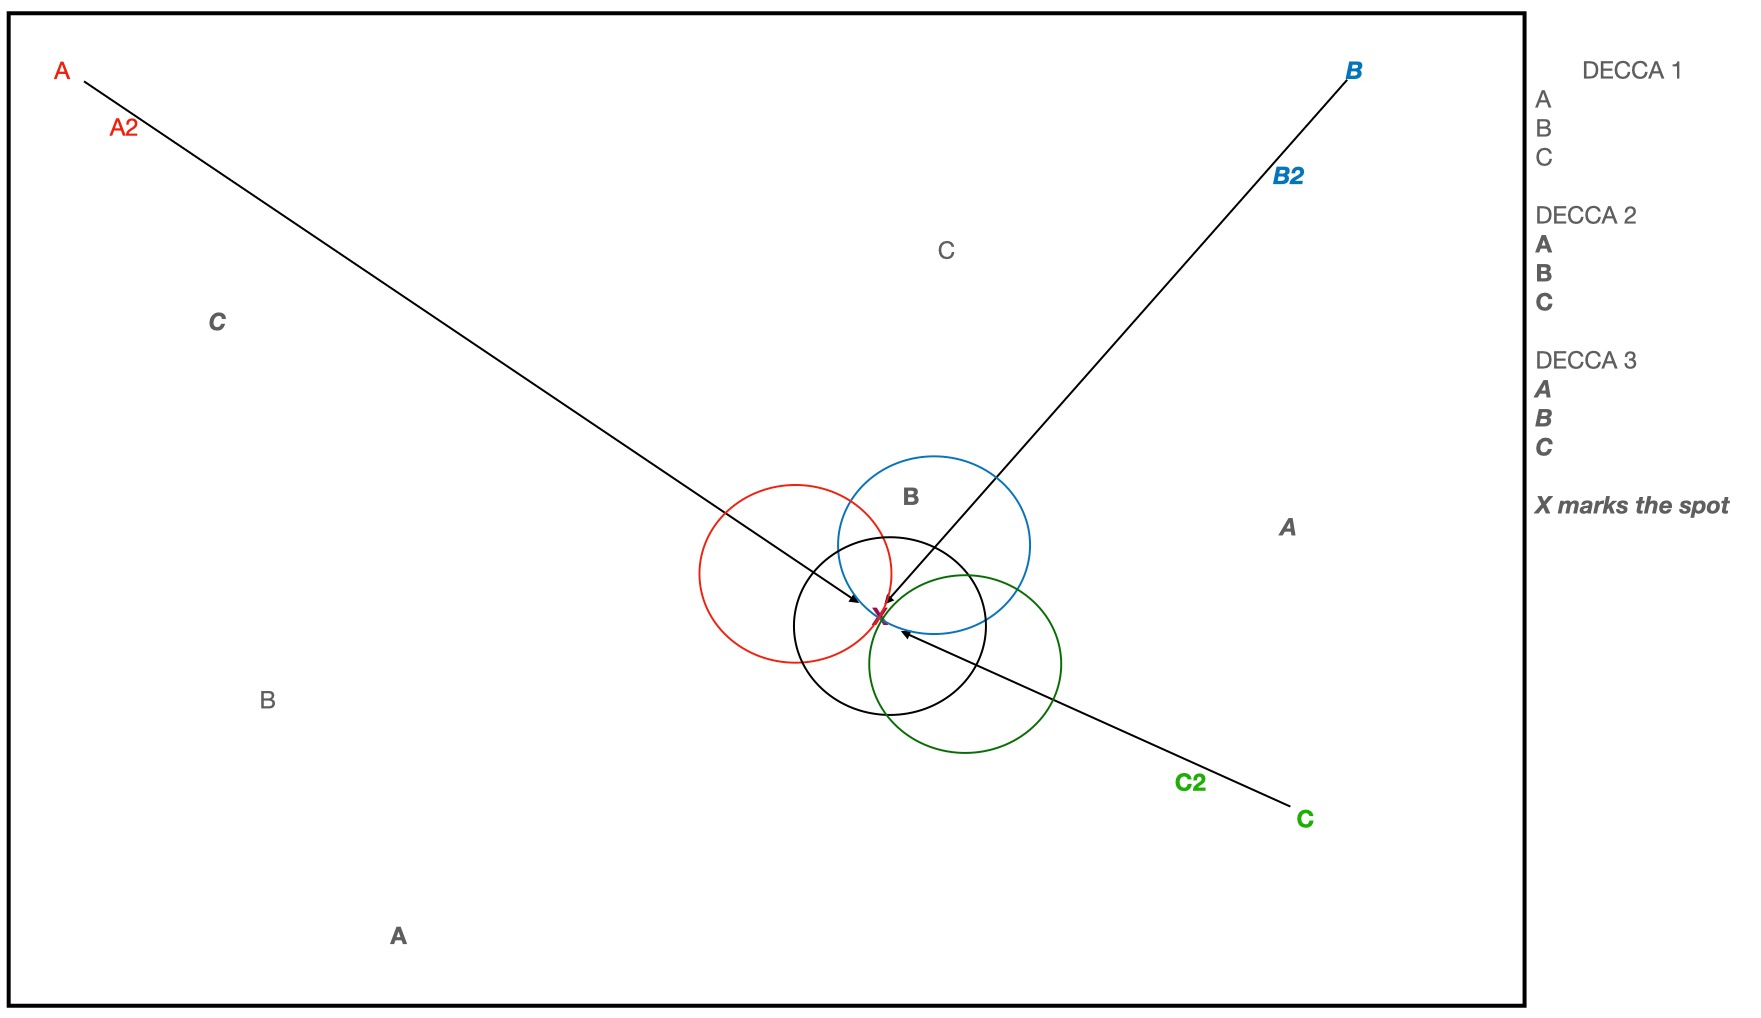
Within the mind there is a setting we forget, it is pondering, we ponder thins, we always do, at times not ever conscious or frontally aware, but we do. It is a part of us and my part would not let the previous story ‘Intent or Not?’ started something that would not let go, most likely to the stage of my youth, in this, my idea of DECCA gave me another optional idea. Consider any map, as such the map I drew has no features, it has however has three DECCA options and the clever station uses one signal of each to create a 4th option. So the three stations 1, 2, 3 create a new option, there would be the optional advantage of internal checks, as such it is harder to decipher how the data is concluded, there is also the need to find a larger amount of numbers to optionally hack, but how? 

The idea is to create an offset, of all the 9 stations, each in different ways to create a new set of locations, optionally an offset the size of the circle, giving is A2, B2 and C2. It is hard to see the precise location, and if the offset is done, it needs to be the offset of the circle, and all three need to receive the same offset, the station is to create a second location that fits within the application of error towards the home and new DECCA configuration. My mind sees part of the solution, but I do not completely get what I see. If we change the signal according to one, we should change them equally to all, it gives (for now) the setting that the target could not be hit but in this configuration, the best we can hope for I that the missile hits somewhere in the circle, the close to the rim, the more accurate the missile was, but can we direct it exactly in the way we want it? If so, the three coloured circles would set the optional new location, if so, it will be in the area of the intersections where blue and red, or green and red connect, optionally in the space between the two, as such there is some way to guide the missile away from harm if a GOLIS approach is used in these missiles. If the missiles is using GOLIS DECCA, there remains two problems, how to find what and which one they use and second how to offset the received signal. Yet as I see it these are seperate matters, what matters is that I am (again) awake and my mind will not stop pondering. Perhaps this idea is merely between my ears and it would never work in real life, but one can only wonder where innovation drives us towards, it is not always a reachable destination, we can only hope it is.

Leave a comment

Filed under IT, Military, Science

Stage light or lime light?

This morning I had to mull things over. I saw ‘Suspected Russian hackers spied on U.S. Treasury emails – sources’ (at https://uk.reuters.com/article/us-usa-cyber-treasury-exclsuive/suspected-russian-hackers-spied-on-u-s-treasury-emails-sources-idUKKBN28N0PG), I saw the news early this morning, but the stage was not clear. You would think that when you see a title like this, the stage is pretty clear, is it not? But in all this, two sentences were out, or perhaps they were off was more apt in this line of consideration. 

The first sentence that waved like a hammer and sickle flag was “according to people familiar with the matter”, this was not some official brief by the FBI or the DHS, it was some anonymous setting and as that nations current president is mad as a hatter (or in possession of less common sense then the Court Jester entertaining Reniero Zeno) gives rise to worry. Now, let be clear, I am not stating that this isn’t happening. Consider “but three of the people familiar with the investigation said Russia is currently believed to be responsible for the attack. Two of the people said that the breaches are connected to a broad campaign that also involved the recently disclosed hack on FireEye, a major U.S. cybersecurity company with government and commercial contracts”, so now it is not from one source, but one journo has access to ALL THREE? Then there is (the secnd one) “cyber spies are believed to have gotten in by surreptitiously tampering with updates released by IT company SolarWinds”, which also affects the military, and in this, we grb back to the earlier statement “they asked the Cybersecurity and Infrastructure Security Agency and the FBI to investigate”, really? Military integrity is in play and you think that none of the Defence intelligence groups, or cyber command is invited? Then we get the end which gives us “The hackers are “highly sophisticated” and have been able to trick the Microsoft platform’s authentication controls, according to a person familiar with the incident, who spoke on condition of anonymity because they were not allowed to speak to the press”, that and the consideration (not fact) that “Hackers broke into the NTIA’s office software, Microsoft’s Office 365. Staff emails at the agency were monitored by the hackers for months”, consider that and set the light towards a transgression on the Microsoft Azure cloud that makes their cloud useless, or turns it into a public domain Bulletin board, something EVERY industrial wants to hear. You think that this was not out in force and Microsoft was on every channel on the PLANET explaining to the people that there was no cause for alarm? All this and some Christopher Bing has three sources? Anyone else concerned with the quality of news? And the last line giving us ‘because they were not allowed to speak to the press’ did it for me. 

Is this a ploy to avoid the limelight, or make sure that the stage lights are pointing somewhere else? Now, I reckon that the Russian government is forever trying to get its fingers on all kinds of hush hush details, the CIA does pretty much the same thing, yet in this we see “highly-sophisticated, targeted and manual supply chain attack by a nation state”, what evidence is there? This is important, because it could well be organised crime or a super rich singular player who wants the low-down on deals that syphon his or her money more efficiently and that has been done before as well. In this the entire approach is one of chaos, even if the chaos seems organised. The fact that it was allegedly possible to “Staff emails at the agency were monitored by the hackers for months” with the mention of Microsoft 365 and the news was limited to one person at Reuters? That and the fact that it as seemingly ‘months’ is a larger cause for concern, the fact that this was going on for well over a week and not every Christmas light would shine brightly red at 2624 NE University Village St, Seattle, WA 98105, United States is a first, the fact that not every siren is blasting on EVERY Microsoft 365 and Azure data centre is a second. But no, we get “there was a breach at one of its agencies and that they asked the Cybersecurity and Infrastructure Security Agency and the FBI to investigate”, yes because dimensionality in alarms and corporate dangers are passed on forever to the FBI in such a blasé way.

So I have several issues on the matter and in all this I can in all honesty not determine whether the light shining is a limelight to give visibility to someone else, or a stage light to make the people look to the left all whilst the people on the right are running off the stage, hoping no one will notice. It can be either or both, but the picture they are painting for us does not make sense and lust like that Italian dude (read: doge), the 45th no less, had his own battles to fight (mostly with Genoa), it was set in one quarter, but had underlying conditions (like Michael VIII Palaiologos) and in this certain nobility members profited greatly, I wonder why that never got properly investigated. And as such I do not oppose the pointing fingers at the Kremlin, but doing so before we see “the Cybersecurity and Infrastructure Security Agency and the FBI to investigate” deliver a finished report is a little fast, so fast even McDonalds cannot compete. All whilst cybercrime has a much larger reach to a great deal many more people and still Microsoft remains silent. 

There is a bright light over yonder, yet what it is used for, I cannot tell.

Leave a comment

Filed under IT, Media, Military, Politics, Science