Category Archives: IT

Burning out your life

Yesterday’s news in the Guardian is skating on an interesting side. Yes, there are more games awards coming, there are new releases and there are all kinds of events coming into play. So when I read ‘Crunched: has the games industry really stopped exploiting its workforce?’ (at http://www.theguardian.com/technology/2015/feb/18/crunched-games-industry-exploiting-workforce-ea-spouse-software), I read it with a different set of eyes.

The first part is “EA relied on vagaries of American law that classify some IT professionals as exempt from overtime pay. The settlement in the second case featured a quid pro quo: employees would be reclassified in order to get overtime but would give up their stock options“, I can guarantee you that I have been in the same set of shoes, Market Research is at times as caring as a steamroller driving over Miss Daisy. It is nice to see the claim ‘stock options‘, yet that flavour of reward tends to be for the managers and the heads of development, not for all the programmers. They tend to get an evening of free food and booze. Take 35 programmers each having done 100-250 hours of extra time, getting paid off with a $300 meal, works out great for the manager getting his 25,000 stocks at $0.50, not so great for others. I am not stating that this works exactly like that in gaming, but I have seen it in other areas of software.

“The most common theory is that the industry is simply too young and too fast-moving to integrate proper management techniques. “Our project was huge and our overall quality assurance process at the time was very basic and waterfall-esque,” recalls one quality assurance worker at EA“, is the second part. This has been shown in several games of late, if we look at the flawed releases of 2014, we can clearly see a lacking scale of QA. It then refers to the work of Fred Brooks on how company size influences efficiency. There is no denying that. Proper management is required, especially when the group grows faster than projected. A special mention of the honour guard must be given to the Marketing department who then also changes the timeline, to get that extra revenue, like marketing COULD have figured that part out at the very beginning. All this will add to the burden of quality delivery and the stress of the workers.

This quote is important, as I consider this to be a stronger part of the sliding quality scale “I was a quality assurance tester at Rockstar, and at its worst, we worked 72 hours a week“, a decent reason for quality to slide (irritating that Rockstar still pulled of a 90% plus rating, although they had a few start-up issues), especially when you consider the following quote “if you had issues with it, you were told ‘Well, you can go stack shelves at Tesco instead or answer phones at a call centre’. You were treated as disposable“, not an entirely unknown event for some in the IT pool. When we consider ““Developers and managers should never have to work more than 40 hours a week,” he says. “It’s a fun job, but it shouldn’t be an exploitative one. Everyone has a life. Let them live it, it’s short enough as it is”“, that sounds partially as a solution, but only if it affects the entire range of staff.

I personally see this all as a reason on why there has been a sliding scale of quality. Is there a chance that Ubisoft has been on this track? This is NOT an accusation! You see, too many hours result in burnout, burnout influences creativity and resolve, crunch time, might give a little extra resolve, but in the end it costs more then it brings. I think that the power of innovation will always win, if balance and rest (to some extent) is made available to revive the soul and the mind.

I think that the next quote sounds nice, but is it enough? “Over the past 18 months, EA has been making significant investments in new quality assurance tools and automation technology, implementing ongoing testing right from the beginning of game conceptualisation. These changes are ultimately improving game quality, as well as reducing the need for the crunch periods”. These tools need proper implementation, they need proper assessment and the people need to properly use them. It tends to add a strain to all levels for a little while. More important, it is only one side of the game (pun intended). For example Mass Effect 4, the engine, the locations, the interface, all are under stress to be made. What if a solution throws the gaming experience? What happens then? What happens when the initial reception is ‘average’, what will marketing do then and more, what will the size of crunch become at that point? You see, the article ignores one little part. For all intent and purpose, games tend to surf at the very edge of technology.  In some cases the makers will attempt to get the max of a system that is at times a little buggy and when you try to use 99% of the system, things tend to go pear shaped really fast. We can offer that the danger of being over ambitious is a bad thing, but this is how some games came into existence. The very first Unreal and Unreal tournament were both chartering the maximum of graphical capability when they were released. Some people invested hundreds of dollars to get a Diamond Labs Graphics card to get the maximum of the game. This is only the tip of the iceberg, when we see consoles there is less manoeuvrability, yet getting the maximum of a game has never stopped the developers. That part is not addressed and that part is every bit as important in dealing with the timeline and QA of a game.

Yet, it is not as much as it was (or so they say), but making the great hit at the E3 or another main release date is the main drive of crunch, especially when the final piece of the development puzzle does not quite fit. That part might be addressed in the management charter, but we must also be realistic that a great game takes time to develop, which made a statement given by Ubisoft “We are able to offer people a new Assassin’s Creed every year because they want Assassin’s Creed every year” nothing more than a joke. Especially if they wanted to rule the gaming industry. In addition I would like to raise that the next big thing is supposed to be ‘No Man’s Sky‘ which will arrive in 2015. We must realistically anticipate that the hype gets away from us all, but it is still seen as the big thing. It took several years, which gives additional view to the hilariousness of: “Ubisoft: No Annual ‘Assassin’s Creed’ Would Be ‘Very Stupid’“, it is such an issue because true innovation takes time, consider on how certain glitches had been around in AC2, AC2B, AC3 and AC Revelations. I can understand that some of these glitches were around in the second game, but to still have those issues 2 games after that is just a laughing matter. There is a reason for me to mention Ubisoft, not because I am ‘so’ against them (I truly am not), but their track record speaks for themselves. So will 2015 be an EA year? That part remains to be seen, however, as I see it at present, there is enough indication that Ubisoft had been hit by burnout staff (assumption on my side). Will a change of atmosphere give us better games? I certainly hope so, because games thrive on the creative and innovative mind, a state that crunch time seems to destroy. This is not just my view, there are loads of views out in the open, some scholarly, some less so, most of them all agree that crunch time and creativity are opposites, so why rely on it? My personal view is that in several cases, these companies (the big ones) didn’t choose the wrong style of management, they choose the wrong sort of manager altogether.

If you doubt my words (which is always fair enough), then consider which games were the true big hits and how they were made. The age old example remains the strongest one. Minecraft was never a big project, yet Microsoft regarded it to be worth over 2 billion. a simple low res game, addictive as hell is worth more than the bulk of the gaming industry, you see, Ubisoft and Electronic Arts both made the same mistake, as they ‘relied’ on a business approach with BI solutions and spreadsheets, they forgot their number one part. If a game is no fun, you lose all your customers really fast. They both made that mistake in huge ways. Both forgetting that their games rely on innovation and creativity, both have ad massive losses in that regard. Will Ubisoft recover? That is hard to say, the EA machine is claiming improvement and it seems that Mass Effect 4 will be their greatest test. EA got hurt badly by Sims 4 and Battlefield, we should also look at ‘Dragon Age: Inquisition is great, but here are 8 things it could do much better‘ on GamesRadar, because when we read that this is a 100 hour game and it loses momentum, we can agree that $100 for a game that could be played within 2 weeks is a little demotivating. It goes back to long before Infamous: Second Son (which is just one of the games that could have been legend), I think that the makers need to retrace their steps on how many hours a game should offer. No matter how good the graphics are, I finished Tombraider in one weekend, which is not good mojo money, especially when you consider that the initial edition (on PS1, 19 years earlier) took a lot longer and was riddled with juicy little challenges. Aren’t games supposed to go forward on more sides than mere graphical resolution?

So as we judge those who make the games we desire, we see that those thinking that they are pushing towards what we desire, only end up delivering a lessened product due to pressures from too many sides, not in the least pressures that they internally created. Even delays (Watchdogs and Elder Scrolls Online) end up not being solutions, in case of the Elder Scrolls, with so many delays that the latest tells us June 2015, has been the reason for many people to just cancel the order altogether. The fact that Elder Scrolls has dropped the subscription part shows just how dangerous their position has been. Here I do want to brag a little, because I came up with an entirely new Elder Scrolls almost two years ago, one that could have saved them many issues as they tried to ‘fix’ their MMO approach. Just as consoles require great games to survive, great games require the right people, people who need to be well rested to get them that golden idea that will make legend. Watchdogs did get a lot closer due to the delay, but what if the difference between 84% and 93% was two weeks of rest? That one golden idea that drove the game to legend status? Is it realistic? You see in hindsight that is all good and well for me to claim, but that is AFTER the fact. I believe my view is the right one, they just needed the right manager to inspire them a little further along, but as always, it is a personal view and it is a debatable one, I do admit to that part.
 

Leave a comment

Filed under Gaming, IT

When the offer is free

Try this for free! This is the commercial teaser we all see when we are offered a dozen of options. There is LinkedIn Premium, Spotify, Salesforce and the list goes on for a very long time. It is a way to get interested in a service or product. I myself tried ‘Today Calendar’ for free, than I upgraded, trials are to some extent a great solution. Try before you buy is a way to get into it. There are games that let you download their Demo, DLC’s that work for a week or two, then you decide, buy or fly!

It is an old marketing option that costs little and bring great reward for those employing the situation. There is however the detail. This we see in the article ‘Why are Amazon Prime customers angry?’ (at http://www.channel4.com/news/amazon-prime-charges-anger-customers-online). Several sources had the story, but Channel 4 read the clearest. The sub-line gives us the goods “Amazon defends a free trial of extra benefits, which ends in an automatic upgrade to paid membership costing £79 a year“. Amazon additionally responded with “Amazon says everyone who signs up to Prime gets an email telling them the duration of the free trial, how to avoid continuing to paid membership and how to cancel membership“. This seems clear enough. So when the guardian gave us ‘Giles Coren declares war on Amazon Prime over free trial‘ (at http://www.theguardian.com/money/2015/feb/16/giles-coren-declares-war-amazon-prime-free-trial-subscription), the impression was left with me that someone did not read their e-mail properly, now that person is crying wolf.

There is however another side to this debate. Should silent transfer be allowed, or should there be a mandatory change to an opt-in transfer? So, should the trial be auto cancelled after 30 days and in addition should we see a second confirmation after 30 days that the continuation is no longer free? This option is the one we usually see in software, when a trial is over, we see that the software no longer functions unless you start paying. On the other side we could consider that some consumers are too stupid to be allowed to have a credit card. The man considers himself an adult. He signed up for a trial, if we accept the response from Amazon that confirmation e-mails have been send, with the explanation on how to cancel it, he himself got into this scuffle by ignoring the message. The Guardian also shows another side that people seem to ignore. The two items involved is a tweet by Giles Coren “I mean, @amazon, offer a free trial in 2012, then quietly start charging £79 and never tell me. That’s what sicko porn sites do! I’ve heard“, so he has been charged for membership in 2012, 2013, 2014 and perhaps even 2015 and only now he ‘wakes up’? Now, this can happen, it has happened to many people, including me, yet 79 pounds is not a costs you easily oversee. To some it amounts to the 6 months fee from your internet provider, which should be taken into account. The second piece of information from Amazon is “Customers who sign up to a free trial of Prime receive an email informing them of the duration of the free trial and how to avoid continuing to pay Prime membership. Customers who become full Prime members can cancel their membership at any time and we will refund the full membership if the customer has not made any eligible purchases or used any Prime benefits“, which gives us the second part. So from that it would seem that Giles Coren must have used some of the services and now he is miffed on having paid for it. That conclusion I get from him not getting a refund, which means he had used the Amazon Prime services.

The article is not just an Amazon or an e-Commerce article. It is also an article that shows the unjustified demand of continued free services after the free trial ends. The two sides pulling on this are Amazon as well as pragmatic realism, as one Tweeter replied to Giles with “Shocking indictment of Oxford and private education as former student doesn’t understand the words ‘free trial’“, which pretty much sums up the ignorance people are showing when they accept free trial whilst not looking at the conditions. The one part I will also illuminate is the complaint we saw from a man called Richard Brown: “Regardless of the legality of the transaction and the stance that Amazon will take that it involves selection and a follow up email each year, the structure of this service is clearly designed to benefit from the customer’s lack of attention“. That too can be seen in two ways. I do agree with Richard on that Amazon should send a follow up e-mail on the subscription every year. These places can send you marketing mails until your hard drive has zero space left, but then shows a lack of ‘tenacity’ to inform their ‘customers’ via e-mail on the payment made, which I see should be a mandatory act in the first place (perhaps that happened, but no one mentioned it in any of the articles I saw).

It is the second statement from Richard Brown that bothers me “this service is clearly designed to benefit from the customer’s lack of attention”, not whether that is the case or not, but in regards to the consideration. This reminds me of the initial marketing when we saw the presentation from Microsoft on the launch of Windows 95. The slogan was ‘without even thinking‘, it was brilliant to some extent. Windows 95 was the first step towards people and true intuitive use of computers. Now, many (pretty much most users) are using their devices intuitive, but there is the added part we see that is at the core, marketing is all about getting a foothold, now we see part that implies (emphasize implies), is that consumers are either getting dim (not that unheard an idea), or that we are faced with two new elements, the first is ‘intuitive buying‘ and ‘intuitive marketing‘, the second one is the holy grail of achieving revenue. When used correctly it is seen as ‘Achieving influence without persuasion‘, there is an interesting article (at http://intuitiveconsumer.com/blog/intuitive-marketing-achieving-influence-without-persuasion/ ). It talks about the six mechanisms of influence used by intuitive marketing. They are ‘Trust: Intuitive marketing builds trust and relies on trust‘, ‘Consistency: Intuitive marketing is consistent and therefore communicates reliability‘, ‘Fluency: Intuitive marketing is easy on the mind‘, ‘Emotional reward: At the opposite end of the spectrum from high aspiration is the realm of small emotional rewards‘ and there are the final two ‘Aspiration‘ and ‘Aligned intent‘. As you see (especially after you read the linked article), the Amazon Prime situation seems to address 4 of the 6 elements of intuitive marketing, so when we see the Amazon Prime issue, is there deception? I personally say no! Amazon offered an agreement, one that gives you a cool down period of 30 days. The definition can be seen as “offer, acceptance, and consideration (payment or performance), based on specific terms“, this is what is at the heart of it all. The emotional response of Giles Coren with the reference to ‘that’s what sicko porn sites do!‘ which in my view holds no value, yet ‘the structure of this service is clearly designed to benefit from the customer’s lack of attention‘, the mention by Richard Brown is much better and decently more apt, but is it valid? ‘Lack of attention’ sounds nice for sure, but does that make the consumer less responsible? Especially when Amazon offers, “Customers who become full Prime members can cancel their membership at any time and we will refund the full membership if the customer has not made any eligible purchases or used any Prime benefits“, which is a decent counter offer, which was part of their offer as I see it. So first, the person gets a 30 day cool down and if the person has not used the service at all, they could get a refund. It seems to me that Amazon offers a decent service, so why do these events cause such a strong reaction?

The part I have not touched upon is ‘intuitive buying’. One vendor had this little slogan with their product ‘intuitive buying just like in an internet shop’. Now we get back to the initial Windows 95 slogan, this gives us in the end ‘buying without even thinking’. So we have a complete picture, but what neither article skates on is when will we see the accountability of the consumer. The person who was given a credit card, an adult who was supposed to be of sound state of mind. The person buying, was notified and then did not react. Intuitive buying does not make a person unaccountable, is that what the articles are steering to? No matter how many complaints we see, the clear indication is given that Amazon gave up front and it allows for correction in hindsight.

Hidden under this is the issue, not on the side of Amazon, but on our side, we consumers need to consider the clear truth that nothing is free! Should any internet offer be treated the same way trial software is? That remains valid, but if so, is that because consumers are no longer to be considered ‘adult’ or accountable, or is it because of another path of reasoning?


Leave a comment

Filed under Finance, IT, Law

A coin with more than two sides

Let us take a look at two of many more sides. The first side is given in this article: Google’s Vint Cerf warns of ‘digital Dark Age’ (at http://www.bbc.com/news/science-environment-31450389). The initial quote is “Vint Cerf, a ‘father of the internet’, says he is worried that all the images and documents we have been saving on computers will eventually be lost“. This sounds nice, but is that not the same as we have had forever? If we did not take care of our old photographs and our old negatives, than those pictures would be lost forever, so how is that different?

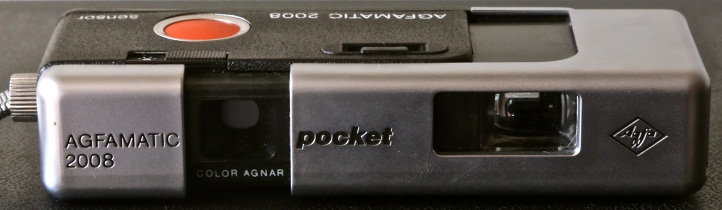
110mm_Agfa

See here, the picture of an Agfa Instamatic. It is almost identical to the camera I had in the late 70’s. So, how will you get those negatives developed? Where to buy film? Most will not care about it, many have bought new camera’s, but where to print the negatives you have? Nowadays with digital images, almost any printer will print it, almost every system will show them. How is that different? So are the words of Vint Cerf anything else but a sales pitch for some new ‘forever’ saved option, likely one that Google will offer and not unlikely in a way that gives Google shared ownership. Is that under the current feelings of ‘data collection’ such a sceptical view to have?

Now, I will state, that not unlike those old prints, the owner has the responsibility to keep the images safe, just like in the old days. Even if the originals (the digital negatives) are lost, as long as a print still exists, the image remains, just like the old photographs. Yet, his quote “But as technology moves on, they risk being lost in the wake of an accelerating digital revolution” holds truth, because that is not unlike the 110mm film issue. So as long as you have a data option that survives, like the 110mm negative holder, you can always get another print. So, CDROM’s in a writable version came in the late 90’s, so we only started to have a backup option for 20 years, yet affordable digital images would still need several more years. Yes, that market has grown exponential and now, we see the application of Common Cyber Sense in another way. Now, people will get confronted with the need to back things up. As the Digital disc evolved, so has the quality of these solutions. Now the discs last a lot longer, so backing up the old discs on new discs does make a whole lot of sense, so there is a side that makes perfect sense, but is that enough?

That part is shown in the following quote: “’I worry a great deal about that,’ Mr Cerf told me. ’You and I are experiencing things like this. Old formats of documents that we’ve created or presentations may not be readable by the latest version of the software because backwards compatibility is not always guaranteed’“. This is at the heart of what Vincent Serf is getting to, so he is definitely onto something. How many of you can still access all the WordPerfect files you created in 1992? Who can still access their FRED applications and their Ashton Tate’s Framework solutions? That list is slowly and surely getting close to zero. This is what Vincent is getting to and there list the crux, because this would have gone beyond mere images and what we currently still access. Consider the Digital VAX/VMS systems, the collected data that spans decades from 1982 onwards. The IBM series one (those 64Mb mainframes with 10 9” floppies), so Vincent is perfectly correct (as a man with his experience would be), but what solution to use? Yes, his idea is perfectly sound, but the issues that follows is the one that I have to some degree an issue with, you see, sometimes things get lost, which has happened throughout history, would our lives have been better if the Library of Alexandria survived? Would it be better, or would there be more and more incriminations? There is no way to know, but the issue can be explained in another way. This is a myth I heard in school a long time ago. The story is that a person could ask whatever he wanted for a created chess game. He asked for a grain in the first square, two in the second square and so on. By the time the board was half way through, the person paying for it would owe the person 2,147,483,648 grain seeds and that is just half way through. Now think of today’s world, where we collect everything. Like the chess board we collect every part and this just increased the junk we collect and that at a premium price. So what to keep? That is the hard part, it is interesting to keep on the side that sometimes we need to allow to lose things, but Vincent has a case. Now we look at one of the last quotes: “’Plainly not,’ Vint Cerf laughed. ‘But I think it is amusing to imagine that it is the year 3000 and you’ve done a Google search. The X-ray snapshot we are trying to capture should be transportable from one place to another. So, I should be able to move it from the Google cloud to some other cloud, or move it into a machine I have’“. Yes, there is the sales pitch. “Google search” and “move it from the Google cloud“, so there we have it, the Google cloud! Still, even though there is a sales pitch in here, does that make it a bad approach? Are we better because we save EVERYTHING? That is at the heart of this little conundrum. Now, those having their data on the old Cray might consider their data worthy, so do many who had their data on UNIX mini’s, but now consider every Novell edition, every desktop, now, it will be arbitrary if people decide to take these steps, yet what happens when all data can be baked up like this, what happens when some start ‘offering’ this for ‘free’? Who then co-owns that data, those solutions? Is that such a crazy thought to have?

Here is the last part: “And that’s the key issue here – how do I ensure in the distant future that the standards are still known, and I can still interpret this carefully constructed X-ray snapshot?” This is the part that is interesting; his concept of Digital Vellum is an interesting one. Yet, how should we move forward on that? What happens when these snapshots link up, when they connect, perhaps even interact? There is no way of knowing; perhaps this would be the beginning of a new evolution of data. Is that such a weird concept? Perhaps that is where we need to look at other sides too. Consider our insight, into our memories, our ‘wisdom’ and our ability to filter and extrapolate. Is this solution a primal step from near ‘artificial-intelligence’ to possible cyber/digital intelligence? The question becomes, if intelligence is grown from memories, what do we create when we give it everything we ever collected? I have seen the stories, the way some people think that the dangers of an artificial intelligence is so dangerous. We might consider the thoughts from the ‘Cyberdyne’ stories (Terminator series), but in the end, what if the digital intelligence is the beginning of our legacy? What if we learn to preserve ourselves, without leaving a carbon footprint, without being the deadly blight on nature? At some point we will stop to exist, we die; it is a simple consequence of nature, but what happened, if our wisdom is preserved? Many come with stories and nightmares of the loss of identity, but what happens if we can store intelligence? What happens if the next century Albert Einstein would be there to help us create progress, inspire innovation for all time? Is that such a bad thing? Some of these questions are beyond my ability to answer but there is a dangerous dark side too, what happens when this becomes commercial Intellectual Property? I am all for IP, yet, should cloned intelligence become the property of anyone? I feel that I might be alive long enough to actually see that question go to court. I hope that those making that decision are a lot wiser than I currently feel.

This now gets me to story two, which also came from the BBC (at http://www.bbc.com/news/technology-31440978), the story here is ‘Cybersecurity: Tech firms urged to share data with US‘, which gave me the initial scepticism regarding the Vint Cerf story. So, I am not linking them perse, they are separate stories. The initial quote is “Private tech firms should share more information with government and with each other to tackle cybercrime, according to US President Barack Obama“, I do not disagree with this thought, however, there is a side to this that is not addressed. The given quote is “Senior Google, Yahoo and Facebook executives turned down invitations to the summit, held at Stanford University“, so is this about not sharing, or about keeping the data non-sharable. There is part that we see when we look at the quote “Mr Obama is backing the creation of information sharing and analysis organisations (ISAOs) to help firms and government share material on potential threats“, yes, if we consider that Snowden fellow there could be issue, but is that a valid path? You see, consider how some do NOT want the cyber threat to reduce for the largest extent, consider how many software ‘solutions’ are out there, for viruses, phishing attacks, identity theft and several other parts. There are two dangers, at one part we have a possible solution to theoretically start solving and decently diminish the danger, the other side is on how all that data gets linked, that part in the wrong hands is a lot more dangerous than many could imagine.

The following quote adds to the worry: “Government cannot do this alone. But the fact is that the private sector can’t do it alone either because its government that often has the latest information on new threats” My issue is that this should not in the hands of any private part, it could be seen as the execution of the premise ‘absolute power corrupts absolutely’, those who face that lesson will not have an option. I would see a solution if there was collaboration between NSA, GCHQ, DGSE and a select few more. Reasoning? Cybercrimes have a distinct impact on national income and also national tax donations. They have all the drive to get it resolved. I have less faith in private companies, their allegiance is to profit, their board of directors and more profit. This is the issue as they will do what they need, someone falls on a sword and many get extremely wealthy, the data goes everywhere and many become exploitable, classifiable and re-sellable. I have been in data for decades, I think that governments can do what needs to be done, and it is time to change the cycle of re-iterated profit. Governments have made themselves the bitch of the private industries, the three mentioned initially is not enough, consider the quote down the line “Facebook, Yahoo, Google and Microsoft have all sent less senior executives to the conference“, so why was Microsoft not mentioned earlier? What is going on? The interesting part is that Bloomberg mentions Microsoft several times, the BBC article just twice. It is clear that something needs to be done on several levels, but it takes a different scope and a different approach, I feel decently certain that keeping the private touch out of this will be essential, for the reason that private companies have a mere commercial scope. I feel uncertain that this approach will work, it has not worked for a long time; I have seen ego and political play and personal reasoning interfere with results, in more than one nation. Whatever is done, it needs to be done, it needs to be done a lot faster than many consider and even though taking the politician out of a government seems to be impossible, we need to make sure that an approach is considered that does not allow for political exploitation, but how to get that done is another matter entirely.


1 Comment

Filed under IT, Law, Military, Politics

Supporting exploitation

This time, there is a different issue in play, this time, I have felt the consequence of both crime and scheming, all in one nice package. Part of this is set in the article ‘Robbed of a mobile, but we have to pick up the thief’s phone bill. Why?‘ (at http://www.theguardian.com/money/2015/feb/11/robbed-mobile-thiefs-phone-bill).

Now, my mobiles has been stolen, it has been broken and a few other issues have gone my way. Now in the first, I have to admit that I was with Optus at the time, stolen mobile, we had a business account and to my surprise, a new mobile and no hassle (just a small fee). This was great, the doom feeling of what had happened was a feeling that some places are great to be connected to. Now in the article we see the following quote: “it’s worth pointing out that you are not liable for any charges once you’ve reported a phone lost or stolen. But there are often good reasons why this may not be immediately possible, and during the briefest of delays, thieves can run up catastrophic charges“. Yes, this is true, but there is also an initial solution. You see, no matter how important you are as a business person, your ego is getting in the way fast. You see, disabling International calls on day one, in addition to 1900 and 1902 numbers stops massive costs coming your way. There is also the embarrassment you have when your boss asks you which distributor had 1900-blow-my-mobile is also worth the day one blocking action.

The next paragraph is the kicker: “In 2012, Ofcom gave service providers until that summer to present plans to cap customers’ liabilities and declared they would face enforcement action if they failed. Nothing happened. In December 2013 the government announced that six of the big providers had finally agreed a cap, and that, from spring 2014, customers – like victims of bank card theft – would not have to pay more than around £50 for thieves’ phone calls. Nothing happened. A year on, only Three has introduced protection – customers are liable for only the first £100 before a phone is reported missing, provided they report it within 24 hours“, so when you are on holiday or on business abroad, and your phone gets stolen, the chance of you notifying your stolen phone in time is not an option.

The paragraph becomes even more interesting if you Google the following “Ofcom spineless useless“, you get 32,000 hits. So we can say that whatever Ofcom pretends to be, which by their own statements is “Independent regulator and competition authority for the UK communications industries” (at http://www.ofcom.org.uk/), we can state with some certainty that it has failed the British people close to 100%. This view does not evolve in any positive way when we look at http://stakeholders.ofcom.org.uk/enforcement/competition-bulletins/complaints-disputes/, where we see ‘Ofcom’s Approach to Complaints and Disputes‘, the text on that page is “This page provides links to guidance that Ofcom has produced setting out our powers and processes we will follow in conducting investigations into adherence with regulatory rules, consumer protection issues, competition issues and resolving regulatory disputes“, with a few PDF links, so how useful is Ofcom?

Well, the Guardian had this to say: “It would seem Ofcom is waiting for the government to do something and the government is waiting for the phone companies to find a solution“, which is not even close to the actual part, it seems that Ofcom is all about sort of regulating issues, but awaiting feedback from stakeholders in regards to these actions (which are likely to be phone companies and when we see the Telecoms Complaints Bulletin on Ofcom, we see a few charts on silent calls and unwanted marketing calls. So is Ofcom basically a report valve that gives the telecom companies a signal when marketeers and phone companies have to simmer down a little bit?

So when we see the claim “Ed Vaizey, the digital economy minister, met the big players last month. Once again they promised a code of practice, but, strangely, still haven’t agreed on the details. “We expect the networks to confirm shortly details of liability caps and when they will be introduced,” says the Department of Media, Culture and Sport“, we must wonder if Mr Vaizey is actually seriously looking into an issue that has played for many years now.

The next part involves Vodafone (or Vodafail as some call it) and opens up an entirely new can of worms, one that I myself have been privy to.

“Vodafone says it has agreed to “explore” a cap but the sticking point is how to do that without destroying the incentive to report a phone missing. “We do not want to create an environment where it is even more attractive for criminals to focus on theft,” it says“, you see, that is not the Vodafone I have been experiencing!

So, last year I had a heart attack, this happens, as it happens I had a sim for my iPad with Vodafone, which is a data only thing. Now, I admit, I was late with paying, which is my own fault and whilst in hospital, they had cut me off. With that I had no issue; I was late, my own fault, as I stated before. Now comes the kicker, whilst in hospital  and after that in recovery, I learned that even though cut off, I am still liable for ALL COSTS, so that means that whilst cut off, I am still due all monthly expenses, even when disconnected. The fact that I had had a heart attack did not interest them. So I am still in a legal fight with Vodafone, I accept the initial costs, but the months after that I refuse, so it is due to go to court at some point. Vodafone might state it is exploring, yet its main need is to stay afloat, which makes them close to desperate. That part is seen with ‘Mobile users flee Vodafone Australia‘, which started in 2013. The quote “Vodafone Hutchison Group lost 600,000 customers in the three months ending September 30, even as its British parent first-half results showed a return to profit” is only the tip of the iceberg that will sink the ‘Vodafonic’ (that event filmed by James Cameron, where you see Leonardo DiCaprio drown in icy cold water at http://www.businessspectator.com.au/news/2013/11/13/technology/mobile-users-flee-vodafone-australia). The fact that Vodafone is still linked to a class action brought by Piper Alderman should indicate that Vodafone has a league of issues, capping is not even close to their essential need to solve.

But we go back to the issue at hand regarding phone bills. The article ends with the realisation that in an election year these issues will not be addressed, which means that this issue will stay around until at least 2016, which is odd as we consider the article ‘Bankrupted by a mobile phone bill‘ (at http://www.theguardian.com/money/2013/dec/07/mobile-phone-bill-cap-theft), which is 14 months old. The issue, that was raised and gave way for the quote “culture secretary Maria Miller told journalists in Beijing this week that a deal had been struck to introduce a bank card-style limit to a consumer’s liability – possibly as low as £50“. In my view as a Tory, both Maria Miller and Ed Vaizey need to wake up fast and start a few fires in the halls of telecom corporations. You see, it is after all an election year and should Labour or Ukip achieve that what the conservatives could not, the fallout will be, as I see it a conservative unpopular one (well over 80% of the population worries about their mobile bill), because governing from the opposition bench is not governing at all, it is merely spouting critique to those who govern. The first course of action, as I personally see it, is to shake up the Ofcom executive committee by replacing Steve Unger, Polly Weitzman and Jonathan Oxley. I reckon the signal that the chief executive, the general council and the group director for Competition are replaced by individuals with bite, who will hunt issues for the victims and the general audience, might give the signal to the Telecom companies to act now, or accept a much harsher deal soon after the elections are done. The reality is, that when that signal comes, they will all quickly agree with the Three policy, which means a £100 cap and possible a reporting extension to a max of 72 hours, which would be fair.

Yet, this is not even close to the only thing in play, you see, last month Google made an announcement to no longer support any Android version before KitKat (v4.4). This means that not only are people almost forced into new mobiles, the flaws, gaps and other issues that might pop up are at the heart of what follows and that what is already happening to the current mobile user base (including myself). First there are the iPhones. Apple is already experiencing the class action in that regard. The fact that IOS is taking up around 20% is just bizarre. Apple could have saved itself a lot of hassle by just having the 64Gb phone at a 16Gb price, I was told (from an unconfirmed source) that the parts involved costed no more than $49. So how ridiculous is the entire issue that Apple is forcing upon Apple? Let’s not forget they have around 170 billion in loose change. Now, I am not stating that they had to pay for it, but to just set the 64Gb edition at $799 would have saved them a boatload of hassles. In this Android is not without faults either. The new phones, with 2Gb ram and 16Gb storage drops down a lot in Android. There, of the 2Gb you are only left with 1Gb and you lose an easy 30% of your 16Gb. Now, that is still a decent amount, but to consider that my old smartphone, which was 1Gb with 4Gm storage has now dwindled to a 250Mb phone (so I can run 2 apps at the most), with just 2.4Gb storage is not what I signed up for. As Google became too clever for its own good, adding more and more trash I never want or need, setting dozens of updates which no longer let my phone work is now at the core of my problem. I cannot even deactivate most, it shows up at EVERY update, selecting what I actually need and not what Google thinks I might like is at the core of my growing resent of Android. And with every app pushed out, there is additional danger that the security of my phone gets compromised, especially as Jellybean is no longer supported.

Yet there is more. I am now looking at a new phone, whilst I know the limitations I face. The strongest was the Huawei Mate7 premium. Now, here is the kicker, the 3Gb phone with 32Gb storage will only get you 1.7Gb RAM and 25Gb from day one, Android takes the rest and this is close to the strongest phone that a limited budget can buy. In Australia the smallest iPhone starts at $1000, the 64Gb, which would be a minimum choice is 20% more expensive, whilst these phones only have 1Gb RAM. This all seems as short-sighted as the developers of Xbox One showed to have. Yet, it must also be said that 1Gb seems to suffice for Apple, that is shown in this small article (at http://www.phonearena.com/news/Why-Android-phones-need-3GB-of-RAM-and-iOS-gets-by-with-1GB-of-the-stuff_id62901), yes IOS is more efficient, but as IOS evolves, so will the need for RAM, which when it starts to be too little would of force us to upgrade again. Was it such a jump to set the iPhone RAM to 2Gb? When you become a penny pincher, you face class actions and that is exactly what Apple faces now. Although I remain (for now) Android minded, and When we compare the Nexus 6 (the very latest), we see that it only almost equals the Huawei Mate7 premium. The Nexus is however $100 more, whilst the screen resolution was a lot more impressive on the Huawei, but that could just be the Jazz screensaver. This shows that Huawei is not just the Android player, with the P7 and Mate7, Huawei is now the contender that makes Google sweat. Like Apple, Google could have saved themselves a lot of hassle by not skimping on resources, which could have pulled the customers in like a magnet, now in the margins they will see customers slip through their fingers, which will be an unsettling feeling for whomever misses out on commission.

All this as the providers supported exploitation; we see that the massive losses are now showing as the margins are not worth considering for some. The same could be said for the upcoming Samsung S6, it looks amazing, but as they fix one issue by being a 4Gb RAM player, they waste it on bringing a 32Gb version, which might suffice for now, but what in 2 years? Getting the 64Gb version makes sense, but then it becomes a $1240 millstone around your neck. So as I see it, Huawei is the budget choice, which still gives you a top of the line contender, iPhone and Nexus are slowly pricing themselves away by offering the entry option, which is a joke as we see space used.

All this now links back to the issue of phone theft and the inactions of Ofcom. If stolen bandwidth and phone time is all there is, than you are gravely mistaken, these smartphones are not just a connection, they are a link to your diary, your details, your credit, your access and your future. Soon, we will see that organised crime will not just call their mommy in Samarkand, Zhengzou, Davao or Vung Tao. Soon they will transfer your data and access and see what else is under the hood. That is the added danger of the smartphone, because you had one more mail to read, one more file to see or one more connection to make, all that in applications that were never closed and accessed be merely starting the application. You see, what we ‘need’ to have, came first, and we all seem to forget the consequences of such choices. Ofcom cannot be held responsible for this, but they should have set up several parameters a long time ago, as they remained inactive in the phone charges issue, they also did little to nothing into changing certain parameters in connection monitoring and non-repudiation, all that left to whomever else, that is the danger we will face in 2015 and 2016. Unless there is a drastic event that shakes up the media, there is every indication that nothing will be done until it is too late.

History taught us that there is nothing as effective as taking away someone’s cushy job to make the next person consider showing their teeth from day one, but that might just be my imagination.


Leave a comment

Filed under Finance, IT, Law, Media, Politics, Science

The virtual reality of it all

Well, I would have expected my gaming ideas to come from many places, the Guardian was not one of them to be honest, but there you have it, we find information in all kinds of places. reason here is the other BAFTA, not the one eloquently mentioned by Stephen Fry (aka Reaver to gamers), but by the Gaming BAFTA, which will be awarded on March 12th (at http://www.theguardian.com/technology/2015/feb/10/alien-isolation-2015-bafta-video-game-award-nominations). There are many titles that will be mentioned, many will become non winners, and remain nominees none the less and one will stand out. Let’s take a look at those categories and some of the games mentioned.

Artistic Achievement

This is the only place where we see Ubisoft shine, to be more precise their graphical teams, no matter how I spoke out against Ubisoft and how they neglected Assassins Creed, their graphical teams did not. These graphical gurus did show a level of excellence that has been from out of this world. No matter how many bugs we see in Unity, the graphics were unreal, as were they for Black Flag; it is a well-deserved nomination and a possible winner, although they will compete with their own title Far Cry 4 here.

Audio achievement

There is one title that stands out, more important, the title itself is an achievement that many will have waited for, for a long time. It is Alien: Isolation and it puts the SEGA logo back on the screen in a most wonderful way. This alien game is not about blasting, it is about staying alive. This is the one perfect horror survival game that places the genre in a new light whilst remaining true to the atmosphere of the original Alien movie. The Evil Within scratches the surface of this genre, Alien: Isolation breaks through the skin and leaves you sweaty with possible heart problems, just like the original movie from 1979. The game truly takes you to the nerve wrecking ordeal of sharing a spaceship with an alien in the most unwanted way. The audio is every bit as important as the graphics and the audio team delivered like nothing you ever faced before.

Best Game

Is always a hard nut to crack, many games stand out in their own way, for various reasons, SEGA is the strongest nominee here, but a truly exceptional game delivers on many fronts, as such all titles deserve to be there, personally Destiny is as I see it, the least likely title to win, as it depends too much on multiplayer events, yet, this does not take it out of the race, I wonder how the silent title in the back (Monument Valley) will do. It is a silent gem, the use of the masterpieces of M. C. Escher are not to be ignored. There is a mesmerising element in this game that is as addictive as a game like Minecraft ever will be. As I mention addiction, I must warn you to stay away from nominee handheld game ‘Threes’. what seems like a simple game of addition, will turn from one second into the next into a game of addiction and your next set of threes is only one little swipe away. I reckon that in this category it will be a fight between Monument Valley and Threes and either should be seen as a worthy winner.


I can go on but you will have to take your own look and see what you think should be the right one to win. The important element here is that we see two parts of gaming that are now clearly impacting business. The first one is quality, yes, I started with the good side of Ubisoft as their graphical teams truly deserve it, but overall Ubisoft bungled the ball and an event like this, where they should be in domination, they are only attending in the most minimalistic of ways. The critique on several levels for Far Cry 4 and the massive failure Assassins Creed: Unity has shown to be, should be a clear indication that Yves Guillemot needs to clean up his divisions and he needs to do it no sooner than 5 minutes after the gaming BAFTA’s have ended.

The second part in all this is originality in gaming. SEGA is showing that in no small matter, in addition, we see Minecraft mentioned a few times, but the stellar part is that silent achievement Monument Valley, developer Ustwo under guidance of fearless leader Neil McFarland shows that independent developers are the future in more ways than one. The Creative Assembly (those behind Alien: Isolation and the old EA sports games) are not indie as such, but they are a far stretch from a massive developer like 2K and Ubisoft, which in addition show those larger developers that the true gems are in the mind of a person and not in the massive visibility of a division.

It will be interesting to see who is elected winner in these BAFTA’s for the mere reason that those who decide might not be the group that largely play these games, the one part that will be interesting to see is that the audience might see the real Ellie (Ashley Johnson), it is always nice to meet the person you kept safe in a digital world, even if she looks nothing like the digital character, an issue Jonathan Irons who will be portraying Kevin Spacey won’t face any day soon. I am eager to see Cliff Martinez on the stage, hopefully for winning the BAFTA for Far Cry 4, which was an excellent piece of work. I have been a fan of his work since Solaris and Contagion, two of his many created master works. As a debut game, Hitman Go definitely takes a shine. They changed a shooting assassin into a tough puzzle game with pawns shaped like Sebuteo figurines, but in the style of Hitman 47 and the goons he goes after. However, in that same category we see Shovel knight, a true retro game, based on the best of the best old style console games, whilst looking new fresh and fun to play. It is a fun achievement for both the new and the seasoned gamer.

So we will all be looking forward, or in some cases dreading this awarding evening. The only worry might be that the people who casted their votes and enjoying a horror survival stealth game is too low, which might impact SEGA to get a decent amount of the 6 nominations it received. We will see it all on March 12th and no matter who wins, I feel certain that the winning views will entice several players to take a look into nominated and winning games they had not considered playing before, that in itself will make the gaming BAFTA a great event for nominee, winner and gamer alike

The full nomination list can be found at http://www.bafta.org/sites/default/files/uploads/baftagamesawardsnominationslist.pdf

Leave a comment

Filed under Gaming, IT, Media

The next cyber wave

The news is almost two weeks old. There was no real reason to not look at it, I just missed the initial article. It happens! This is also at the heart of the issue on more than one level. Consider the quotes “The first 13-week programme for Cyber London (CyLon) will kick off in April, with a group of startups drawn from industries including defence, retail, telecoms and health services” and “On the one hand, the government is keen to invest in cyber-security startups: witness chancellor George Osborne’s announcement that GCHQ is investing “£3bn over nine years into developing the next stage of national cyber intelligence”“. So is this just about getting your fingers on a slice of this yummy slice of income? You see, this issue skates on problem that I (many others too) saw that Common Cyber Sense existed, but the bulk of companies treated it as an overhyped requirement. Yes, those managers were always so nervous when they got introduced to ‘costs’. I reckon that the Sony hack will remain the driving force for some time, in addition several business units are more and more in need for some better up to data encryption, so this cyber wave is getting some decent visibility. So as we look at the title ‘Cyber London aims to make the UK a launchpad for cyber-security startups‘ (at http://www.theguardian.com/technology/2015/jan/28/cyber-london-accelerator-cyber-security-startups).

There is no denying that the call of 9,000 million is a strong one, especially in this economy. More important, as more companies are gripped by a decent amount of fear regarding their own future, this event will be at the foundation of several longer running projects and corporations. There is of course question on what is real. That question becomes an issue when we see that even now, rumours still emerge on what happened in regards to who did the works on Sony and how it was done, especially in light that the article in Business Insider claims that the hackers still have access. The latter part will be speculated on by me later in this article.

For the most, the next cyber wave is a good thing, especially when thousands of data holders realise that their corporate future depends on keeping these systems decently safe. I use the term decently safe, because ‘complete’ safety is not something that is achievable, not on budget levels that many depend upon. Yes, security can be better and a lot of companies will invest, they will raise the threshold of many companies, yet will they raise it enough? That is at the foundation of what is about to come.

I predict that these startups are all about consultancy and some will offer products, some on safety and some on encryption. Encryption will be the next big thing, the question becomes how will encryption be properly managed? There are plenty of people who enthusiastically encrypt files and after that forget the password. So what then, all data lost? So, you see that clever solutions are needed, which will bring forth a new wave of solutions, new barriers and new bottlenecks. I wonder if these new startup firms have considered a trainings division, not one that is all about ‘their’ solutions and ‘their’ products, but all about raising proper awareness for Common Cyber Sense.

Training that is meant to give long term knowledge to people working at a firm as well as setting a proper initiation of knowledge with these companies, so that a wave of change will not start a rollercoaster of people jumping from firm to firm, a risk many companies will predict to hit them.

Now it is time for some speculation. I have been thinking on how Sony was hit. I came up with a possible idea on New Year’s Eve. When I wrote this part: “In my view of Occam’s razor, the insider part is much more apt”, my mind started to wander on how it was done.

Speculation on the Sony Hack

The inside story is on the hack of Sony, yes, there was a hack at some point, but, in my view, that is not what actually happened. a destruction was started, but that is not what started it, that is how it all ended. When I did my CCNA (2011), I had the initial idea. You see, hacking is about data at rest, so what happens when the hack is done when data is in motion? That part is often not considered, because it seemingly unmanageable, but is it? You see, when you buy the Cisco books on CCNA you get all the wisdom you need, Cisco is truly very thorough. It shows how packages are build, how frames are made and all in great detail. That wisdom can be bought with a mere $110 for two books.  Now we get to the good stuff, how hard is it to reengineer the frames into packages and after that into the actual data? Nearly all details are in these CCNA books. Now, managing hardware is different, you need some decent skills, more than I have, but the foundation of what is needed is all in the Cisco IOS. The hack would need to achieve two things.

  1. The frame that is send needed to be duplicated and ‘stored’.
  2. The ‘stored’ data needs to be transmitted without causing reason to look into spikes.

I think that ‘hackers’ have created a new level (as I mentioned before). I think that Cisco IOS was invisibly patched, patched, so that every package would be stored on the memory card in the router, in addition, the system would be set to move 2% during the day to an alternative location, at night, that percentage would be higher, like 3-5%. So overnight, most of the data would arrive at its secondary location. Normally CCNP technologists with years of experience will look into these matters, now look and investigate how many companies ACTUALLY employ CCNP or CCSI certified people. To do this, you would need one insider, someone in IT, one person to switch the compact flash card, stating 64Mb (if they still have any in existence) and put the sticker on a 512Gb Compact Flash card. Easy peasy! More important, who would ACTUALLY check the memory card for what was on it? The Cisco people will look at the startup file and only that one. The rest is easily hidden, over time the data is transferred, in the worst case, the culprit would only need to restart the routers and all activity would be completely hidden, until the coast is clear, afterwards the memory cards would be switched (if needed) and no trace of what happened would ever be there. What gave me the idea? Well I wondered about something similar, but most importantly, when I did my CCNA, the routers had 64Mb cards, I was amazed, because these suckers are no longer made, go to any shop and I would be surprised if you can even find any compact flash card smaller than 16Gb. Consider a place where Gb’s of data could be hidden under the eyes of everyone, especially as Cisco IOS has never been about file systems.

When the job was finished, the virus could be released damaging whatever they can, when cleanup starts, every aspect would be reset and wiped, whatever the culprit might have forgotten, the cleaning team might wipe.

So this is my speculation on how it was done, more importantly, it gives credibility to the claims that the hacks are still going on and the fact that no one has a clue how data was transferred, consider that this event was brokered over weeks, not in one instance, who else is getting their data syphoned? More importantly have these people involved in this next cyber wave considered this speculated path of transgression? If not, how safe would these systems end up being?

Let’s not forget that this was no easy feat. The system had to be re-programmed to some extent, no matter how enabling Cisco IOS is, this required top notch patches, which means that it required a CCSI or higher to get it done, more important would be the syphoning of the data in such a way that there would be no visible spike waking any eager beaver to prove themselves. That would require spiffy programming. Remember! This is all speculation; there is no evidence that this is what happened.

Yes, it is speculation and it might not be true, but at least I am not pointing the finger at a military force that still does artillery calculations with an abacus (another assumption on my side).

There are a few issues that remain, I think upping corporate awareness of Common Cyber Sense makes all the sense in the world, I reckon that the entire Cyber Security event in London is essential and it is good to have it in the Commonwealth. This industry will be at the foundation of growth when the economy picks up, having the UK play a centre role is good strategy and if it does evolve in the strongest way, a global financial node with improved cyber protection will lead to more business and possible even better business opportunities. This event also gives weight and view to my writing on January 29th and a few other occasions “As small innovators are given space to proceed and as larger players are denied blocking patents to force amalgamation of the true visionary into their moulding process that is the moment when economies will truly move forward. That is how you get forward momentum!“, this is something I have stated on several occasions and I truly believe that this will be the starting pulse to a stronger economy. It seems that the event creators Alex van Someren of Amadeus Capital Partners, Grace Cassy and Jonathan Luff of Epsilon Advisory Partners, and advisors Jon Bradford of startup accelerator TechStars and Eileen Burbridge of venture capital firm Passion Capital are on such a path. No matter how it is started, they are likely to get a first leg up as these startups will truly move forward. As the event stated: ‘No equity taken’, but it seems to me that on the receiving end of implementing working solutions, finder’s fees and linked contracts could be very very profitable and let’s face it, any surfer will tell you that being at the beginning of the wave gives you the best ride of all.

Let’s see what 2015 brings us, startups tend to be not too boring. Not unlike startups, so will be more waves of speculations on how Sony was hacked, the US government will likely continue on how North Korea was involved and at the centre of it all.


2 Comments

Filed under IT, Media, Politics, Science

How it should be

I have had my issues with the latest released games. No quality previews, no quality exams, just after released reviews. In that regard Gamespot has lost a lot of respect in the eyes of many gamers. An example is Dying Light released on January 27th (Digital copy) and reviewed by Kevin VanOrd on January 30th, 2015. It is at present debatable what value Gamespot has left for the gamers at large.

In opposition to this is the review by ‘the RadBrad’ Published on December 10th 2014 (at https://www.youtube.com/watch?v=RLHR5smxbsc).

To be honest I have never been too much for Zombie games and Zombie movies. I have seen a few good ones, but it was never my cup of tea. Why tell you this part? Because this game, as far as shown by RadBrad blew me away! This game looks beyond awesome. The graphics are smooth and it looks pretty detailed. When I took a second slow look, there were a few little ‘glitch’ like parts, but they were minimal. The graphics in the houses and rooms were top notch. This was the PC edition, so I am curious regarding the PS4 edition, time will tell. The video is a must if you are interested in this game. So now I get to the second issue. Kevin rated the game 7 out of 10 with as one bad mark ‘Too many missions are either boring, frustrating, or just plain bad‘. The first hour video (by Radbrad) shows a clear intro on how to play the game, which was pretty amazing. So, the question becomes how this game was just set to 7/10 (partially questioning Kevin’s reasoning). The game is very open world, but still scripted into missions, all in Zombie style. The approach is not unlike several RPG games, now in a modern setting. Here I get my first issue, Infamous: Second son, a game that started good, but then declined in many ways gets a rating higher than this game. So far this game is all full on great, so let’s take another look at the game. When I looked at the smooth Gamespot view, I did see the critique given, there is however an issue, these glitches seem to be PC glitches, were the consoles not compared? That is all a factor, especially as PC, Xbox One and PS4 are all separate consumer markets. YouTube also had a review by Playstation Access (at https://www.youtube.com/watch?v=0AyhZyOMX6A), showing that the PC version had superior graphics, yet the PS4 version still looked really good. So as such, it seems that Dying Light is a different challenge for those into RPG’s and a passion for watching the waking dead, Dying Light seem to successfully combine the two.

Now for the timeline, what was shown by RadBrad, which was not a finished version showed a lot more quality than the Gamespot version. There is of course a difference, Gamespot covers quickly in 5 minutes, what RadBrad takes an hour to show, which gives you a better overall view, but of course, seeing the actual first 2 missions are at that point a massive spoiler. Considering that the first two missions are all about getting the feel of the game, it is not a biggie.

For the most, my biggest issue is that RadBrad covered better and more in depth almost 6 weeks before Gamespot could be bothered to do so. I do not care about the reasoning, they are supposed to be the big boys, and all sponsored up by Ubisoft no less, so the delay and lack of view is not excusable. I am not attacking Kevin on the review, glitches and issues. They are his view (and he is entitled to them), and in the movie he clearly shows the glitches. It is so interesting that the consumer was denied this insight with Assassins Creed Unity until after the game was released in the shops. Dying Light will arrive in stores in 3 weeks; the digital copy is available now (for those who cannot wait).

So, how should things be?

That is at the core, when I was a reviewer; I had access to games usually 3-4 weeks before release. In a few instances that gap was a lot less, but it did not happen too often.

Should we allow for reshaped originality?

That is the question that is linked to all this as new markets are starting to open up. It seems that Sony is finally seeing the light. Perhaps better is the fact that they are seeing the light they initially ignored and now, a year later we are slowly seeing ‘new’ versions appear, new version of previously released games. This is not a bad thing or an issue. Is borderlands 2 any less original now on the PS4 when it was released on the 360/PS3 over a year ago? The game was amazing fun and will give loads of pleasure to the new additions on nextgen systems. The linked issue to all this, is how it will be reviewed. Even it is a transfer, even if it is a combination of the game and DLC parts, will it be properly looked at?

The next step reviewers should investigate is what I would call a ‘redundancy level’ of gaming. To ‘accommodate’ the marketing divisions to optimise their path, some companies have done away with massive levels of quality control. Halo: The Master Chief Collection, Far Cry 4, Assassins Creed Unity, GTA5 and the list seems to go on, all have the same problem, when you buy the game, you are again forced online to download a day one patch, many of them well over 1Gb. It seems that for the most offline play is a thing of the past. Sony and Microsoft needed their data and they will take whatever path they need to get it. So is the last part true, or is it a path that is only in my imagination? For Halo that patch was not 1Gb, it was 20Gb, which means that for some the patch represents no less than 30% of their download bandwidth, which also makes it over 10% of the total hard drive space of the Xbox One, a little excessive, isn’t it? In addition, when looking at the Gamespot review (at http://www.gamespot.com/reviews/halo-the-master-chief-collection-review/1900-6415958/), we see that not only was the review done 4 days after release, but the day one patch issue (the mandatory 20Gb download) did not get any mention, yes, the game did not get a decent rating (6 out of 10 is not that good), but when looking at the ‘bad’ points, the mention of the day one patch is blatantly not there either. So whether we like a revamp of a game, it seems that reviewers need to up their game by a fair bit, a side Gamespot has not been on par with.

These events all link to another issue, which is now getting more and more negative visibility to the audience at large. That negative view only became stronger when Sony got hacked again, and even though not deserved, Microsoft is getting hit by this negative paint to some degree as well. It seems a little too simple to call this ‘conspiracy theory’, yet from their own site we get “Collection and use of your information by Sony Online Services is governed by the SNEA Privacy Policy, which can be found here: http://www.qriocity.com/us/en/legal-privacy“. The link throws you to a generic page where we see a menu and no privacy policy. How interesting such an oversight, whilst this was a direct link, perhaps the privacy policy was removed? In addition, no matter how much we protect our system, no matter how strong our passwords were, the fact that at Sony we find the following: “We do not require that website visitors reveal any personally identifying information in order to gain general access to our websites. However, visitors who do not wish to, or are not allowed by law to share personally identifying information, may not be able to access certain areas of our websites, participate in certain activities, or make a purchase from the PlayStation®Shop“, which is nice, because that is where the patches seem to be, so again, your data is collected, which is than downloaded because of failing security measures and shared with the world. This also has influence on gaming as such, the fact that a less than acceptable version is sold, means that the gamer is not getting value for money. No matter how great the update is, we need to be online and lose time downloading the patch and installing it, with all the additional loss of hard drive space.

This is however not about data collection, but there was a reason for the mention. As we go to ‘reshaping originality’ and ‘how things should be’, we see that even though PS4 started a relaunch with ‘The last of Us‘, which was the last gem on PS3, it is not close to being the only one. The Russian based game Metro is another ‘re’-launch. The question then becomes, will the reviewer take their time to take a proper look at these games? We have seen lack of reviewing with true new titles, how much more lacking will a relaunched title be?

Time will tell, but there is definitely a little less time as gamers are less and less positive about the quality of the latest launches, I also suspect that as the ball is fumbled in both places (reviewer and game maker) that people are less inclined to buy and more inclined to get to a place like Pirate Bay to get the goods and properly test the game, however, there will be a definite drop in revenue for the game maker here. They partially only have themselves to blame, because this has happened before! We saw similar steps when the CBM-64 and Atari-800 were out and even more issues in the time of the Commodore Amiga and Atari-ST. The consumer demands a decent quality game and they want it when it is released (a global thing), not 6 months later on a local market. The second issue has been successfully fought in the past, and it is not as bad as it used to be, but as digital copy and physical copy are too far apart in price and release dates, people will resort to other means, the fact that digital copies tend to be well over 40% more expensive in Australia then in other places is another matter that is angering the gamers and as such, the move towards a place like Pirate Bay is slow, but also slowly but surely is getting a lot more profound.

So how should things be?


Leave a comment

Filed under Gaming, IT, Media

Double standards, no resolve (part 2)

Part two is not about Greece or the Greeks, it is about what has been behind several parts for a long time now. Yet, the visibility of certain events is now forcing another large change to the surface. First let us look at the events as we see them in the Guardian (at http://www.theguardian.com/technology/2015/jan/25/wikileaks-google-staff-emails-us-government).

The title ‘WikiLeaks demands answers after Google hands staff emails to US government‘ calls for a few thoughts, but I think you should consider a few quotes and then reconsider how you feel. The first one is “Google revealed to WikiLeaks on Christmas Eve – a traditionally quiet news period – that it had responded to a Justice Department order to hand over a catch-all dragnet of digital data including all emails and IP addresses relating to the three staffers“. The second one is “Harrison, who also heads the Courage Foundation, told the Guardian she was distressed by the thought of government officials gaining access to her private emails” and then we get “The investigation followed WikiLeaks’ publication, initially in participation with international news organisations including the Guardian, of hundreds of thousands of US secrets that had been passed to the organisation by the army private Chelsea Manning“. So this was specific! Let us not forget that this person (Manning) should be regarded as guilty of treason! This is nothing less than an intelligence analyst going beyond rogue! Manning was a simple E-1 private with no comprehension of the complexity of wars, especially the war the US found itself in, a theatre that is hard to grasp for some of the brightest generals (you know these highly educated, passed their middle age point individuals with a few decades of military experience, in the US seen wearing stars on their shoulders). No, Manning decided on the safety of hundreds if not thousands of lives. In addition US diplomatic efforts were thrown out of the window, setting economic options back for up to a decade, if not longer.

So when we see the response by investigative editor Sarah Harrison “Knowing that the FBI read the words I wrote to console my mother over a death in the family makes me feel sick“, seems a little hollow. For one the FBI does not care about her mommy, two, what did you expect to happen when you access unauthorised data to the size, scope and extent as Manning had transmitted?

I think Harrison is overreacting, if we accept chapter 13 in the Art of war, both the spy and the receiver of information should have been put to death. Is it not a good thing that it was merely investigated by the FBI?

Yet, there is a side that many are ignoring; many do so in an unintentional way, mainly because it tends to not hit us in any way. For that we need to take a step back to Forbes 2013 (at http://www.forbes.com/sites/robertwood/2013/08/06/excuse-me-apple-google-starbucks-h-p-irs-wants-to-tax-stateless-income/), here we see the following parts: “U.S. companies are said to have more than $1.5 trillion sitting offshore. Most claim that they must keep the money there to avoid the taxes they would face by bringing it back to the U.S.“, “the money at stake is enormous. Plus, the companies involved have treasure troves of cash for many war chests. Big and protracted battles seem inevitable. Still, some big companies may be in for battles that are even larger than they think. They may even need to think different” and “The OECD plan claims that companies like Apple and Google avoid billions in taxes. The G20 is made up of 19 leading world economies plus the European Union. It too has voiced support for a fundamental reassessment of the rules on taxing multinationals“. These thoughts all sound nice, but there is an additional element to all this. You see, as I stated more than once, currency is slowly on the way out (loosely approached). The nations that are left with manageable debt are now slowly but surely diminishing to zero. Greece may be the first one, but at minus 18 trillion, the US is the clearest one to end up with nothing, especially as those large US firms have become stateless. You see, now we get to the good part, the new currency will be IP, but here is the kicker, most (including me) seemed to forget that IP is more than Patents and Trade Marks, it includes data! Now we get to the nice stuff, you see, Google adhered to a situation, Twitter and a few others did not, or at least in a delayed way, but the new currency will include massive amounts of data and many players are now catching on that data is at the core a stateless, virtual and duplicable currency. No matter how Sony called its hack attack, does it now look a little clearer that those having a copy of that data are preparing for more than just a data dump? This is what McKinsey & Company had to say in August 2014 “Indeed, the analytics performed by actuaries are critically important to an insurer’s continued existence and profitability“, as well as “While the impetus to invest in analytics has never been greater for insurance companies, the challenges of capturing business value should not be underestimated. Technology, as everyone knows, changes much faster than people. The key for insurers is to motivate their highly skilled experts to adopt the newest tools and use them with creativity, confidence, and consistency” and finally there is “The proliferation of third-party data sources is reducing insurers’ dependence on internal data. Digital “data exhaust” from social media and multimedia, smartphones, computers, and other consumer and industrial devices—used within privacy guidelines and assuring anonymity—has become a rich source for behavioural insights for insurance companies, as it has for virtually all businesses. Recently, the release of previously unavailable or inaccessible public-sector data has greatly expanded potential sources of third-party data“. Yes, it sounds nice that there is public-sector data, but the one part no mentioned is how the analytics is not driven by those, but ascertained through private-sector data fields. You see the data that Sony had on its employees and on the actions of 70 million customers is a lot more insightful when you link it to medical records. Consider how much profit a company gets if it could ascertain more precisely the risk 7 million of its own customers are. If the connection of medical (obesity) and the gamer data of one person results in a $12 per month surcharge, what happens when we see the US having an obesity rating of around 32%? Now we have 70 million accounts and their gaming behaviour. So if we do the following math 32% of 70 million (falsely assuming that they were all American gamers), then we now get the number of people confronted with a $144 a year additive. So in one swoop, this data set gives way to an additional $3.2 billion for insurance fees. Data is going to be that simply applied sooner than you think. With the cloud being forever virtual (as one would think), people forget that a personal space is linked to a real location (wherever that drive is), but what when the data set is beyond massively huge? What if it is spread over several locations? How do we think then? You see Stateless data is not a new concept, but until recently it was never a realistic concept. It is interesting how tax dodging makes engineers a lot more creative.

At the foundation of all this is not the Wikileaks part, that part just illuminates the nutty side of data. Consider the amounts you as the reader had shared in the last 72 hours via Facebook, LinkedIn, SnapChat, Instagram and such. You freely distributed that, you gave up your privacy rights for whatever you openly published. Now consider that whatever you shared got collected. Several people were on vacation (so someone knows that their house is empty and possible unguarded), some revealed that they were sick (health data) and some revealed other details like parties attended and such.

Now the empty house is the most direct one, but not the most important one. Consider the times you updated your status that you were at home with the flu, or something else. Under normal conditions you just had a sickie, or perhaps another way. Now consider that someone now automatically collects the times you were sick, how does that affect your premium? How will your health cycle be analysed if you are shown to have attended 15-30, or even 50-100 parties a year? How long until this shows as detrimental on your health chart? Weirdly enough not having that does not lower your premium, but there is every evidence that doing it will increase your premium.

Do you think that this is over the top?

Then see the following (at http://www.qbe.com.au/Personal/Home/Managing-Your-Risk/Insurance.html). Here we see “Importantly, reducing the likelihood of making a claim helps protect your No Claim Bonus, helping to keep the cost of your insurance premium down“, which has been a truth for a long time. Yet when we consider the mention ‘Don’t alert people you are going away (including on social networking sites)‘. How long until someone combines the two? At reputation.com we see the following “Life insurance companies are increasingly turning to the Internet to determine a potential customer’s risk“, so if you like extreme sports, you might pay for that passion in other ways too. In addition, the one most disturbing was “Donating to charitable causes is a noble gesture, but if you show too great an interest in any particular medical-focused cause, say breast cancer research or prostate cancer awareness, it might indicate to insurance companies that you’re at a higher risk for certain illnesses“, that gives a possible (implied, but not proven), connection that your social responsibility comes at an insurance price. Did you consider that? And this is not starting this year, or next year. Some of these events started no later than 2010.

This all was nothing but to pave the way for that what comes next. You see, there are several sides to Google and Facebook. They are all about bandwidth and several nations are now seeing that even though Facebook is too large, there is a clear path that data is currency, so how long until we see a growth of radicalisation through localisation? This is not radicalisation in the violent way, but in the opposite way. You should see radicalisation of data, attained by washing all the data markers in local server environments. You can’t wash all the markers, but you can make access to it a lot less available. This is the fear Google (possibly Facebook too) has had for some time. As these privacy acts, that data acts and data collection rights of the US grew in a need for compliance, people become falsely fearful of what is dangerous and what is not. The US government ascertaining whether you are a terrorist is not a danger. An insurance company upping your fees by $150 through collected data is a direct danger (to your cost of living). Now we see the link as it gets us to the first story that included Greece.

There will soon be a higher need for localised connected providers. Localised forms of Hushmail (www.hushmail.com), where the people get encrypted mail accounts that can be accessed online, through the web. How long until mobile users will select encrypted android apps, that do not connect to Google, but to local Hushmail providers. We still have the internet, but it will now go through national portals. The fact that Sony happened was only a matter of time. The fact that people now want that there data comes with actual privacy is a growing wave. The Wikileaks issue was the most visible and the most harmless one (for us citizens at least). The world is changing a lot faster than last year and many are now getting clued in that the things of value have not been guarded in the right way.

We will soon see new options on cheaper internet, cheaper mobiles and on package deals, this is what was skated around when this so called IP hearing was going on. Yet, when we look at an earlier statement by Mr Turnbull, in regards to IP, who said at the time. “It is very, very, very difficult if not impossible for someone that is just selling connectivity, just providing bandwidth to then be monitoring what people are doing“.

This is at the heart of the problem, they live of bandwidth, because bandwidth implies data, and the more used, the more data collected, which leads to the better their lives are. This is why they do not want monitoring. I am fairly certain that as their bandwidth falls away, as people move to localised solutions, which remain at the core local, these providers will ‘suddenly’ opt in a ‘possible’ solution. Only at the end of the tether will an industrial give in. Oddly enough, with fear of privacy and the dangers of insurance exploitation on the rise that tether will end up a sudden two inches shorter and now those providers will have to share that what they never had to share before.

Greece has changed the way they play the game; now perhaps we can change the game that is played and make a first monumental change for all!

2 Comments

Filed under Finance, IT, Law, Media, Military, Politics

Pussy versus Tiger

This was my first assessment when I looked at the Guardian regarding the article ‘Barack Obama and David Cameron fail to see eye to eye on surveillance‘. (at http://www.theguardian.com/us-news/2015/jan/16/barack-obama-david-cameron-surveillance-terrorists). As we see America slump more and more into the weak excuse it is on an empty wallet, it must have been quite the surprise for Prime Minister David Cameron, to go to the ‘leader’ of the free world, hoping for a decent lamb chop (which you actually can only get in either Australia or New Zealand) and he ends up having dinner with someone who prefers Purina as a meal.

You see, I am not buying his ‘civil liberty’ approach for one second. In an age where Google is demanding more and more privileges to access your mobile data, where Google search gets transparently pushed into your android phone on top of your functions. In that era HE is proclaiming ‘civil liberties’?

Where we see Facebook where we would have to consent to allow access to our religious beliefs and that of our friends for access to a game. What is this, ‘Gaming for Catholics’? Here we see discord on what is needed to keep the citizens safe?

I particularly like this part “As Cameron warned the internet giants that they must do more to ensure they do not become platforms for terrorist communications, the US president said he welcomed the way in which civil liberties groups hold them to account by tapping them on the shoulder“, tapping on the shoulder? Yes, with Bing, Google, Amazon and Yahoo all in America, he definitely wants the power of collection to be ‘unhindered’ for now. There is of course the thought that President Obama has no control and it is Google and Microsoft telling Congress how it will be for now, which means unmonitored access.

That part is also a requirement to keep the financial sector running uncontrolled until it is too late (a point which might have passed already).

So, is this all rambling? Let us look into the evidence!

The first part comes from the Trans-Atlantic Consumer Dialogue (at http://www.consumersinternational.org/media/1396104/tacd-resolution-on-data-flows-in-the-transatlantic-trade-and-investmemt-partnership.pdf), an organisation not too visible, but it is loaded with high profile participants (at http://tacd.org/about-tacd/whos-who/), the PDF had nothing really new to tell me, but this part is important “The actual extent of these data collection practices, whether they were lawful, or the range of activities involving companies such as Google, Facebook, and Yahoo are still unclear. Until the new US and EU joint group of experts tasked with examining privacy in the light of the National Security Agency’s PRISM Internet data program and related disclosures makes a report to the respective governments and the public, it would be unwise for the negotiators to address data and e-commerce-related trade matters at all. The public on both sides of the Atlantic deserves a full and frank discussion of what actually transpired, and what policies or safeguards should be required as a consequence“. Even though we were confronted with the Snowden fiasco, the massive part that is kept silent is what non governments are collecting, they have been collecting data every second, of every minute of every key press you made these last few years. Data that is valued, without oversight. So ‘yes’, as I see it, the President (or the Democratic Party) is very likely getting told that with oversight, the fat checks will disappear.

This is at the heart of the matter, David Cameron (and several others) needs to keep their civilians safe, whilst as I see it, America is about the bottom dollar at the expense of everyone’s safety. Should you doubt the latter part then consider the next bit “US trade policy requires radical reform, not only to the flawed certification process, but also to the secrecy of trade negotiations in general, the lack of accountability to the public, and Fast Track proposals that insulate trade agreements even from the scrutiny of Congress itself“, which we get from Electronic Frontiers Australia. So, as we see the push for ‘free trade’, how can there be ‘free trade’ without civil liberty? It seems that in the US ‘free trade’ is synonymous with corporate trade, specifically the corporate trade of big business. So as we see that areas are drowning in corporate oversight (by the corporations), we see the term ‘civil liberties’ being cast in a voice to keep big business out of oversight. So, how does your Purina taste today Mr President?

Now the intelligent person will state, what has one thing to do with the other? How did we get from some data discussion to the TPP? This would indeed be a decent question and my answer is that it is all linked. You see, the big data collectors can only continue if it is unhindered by policy. Google’s fortune comes from the data of millions each day. So once the data starts getting holes as the rights of those from the UK, the Netherlands, Sweden, Germany and Australia are set to boundaries, the collected data will show holes, which means the value goes down by a lot. Over 30% of the internet has business, which lands roughly 40% of ALL profits in the hands of US firms. I am precise in my statement here, US Firms! Not US government or the IRS, just US firms who will syphon billions via Ireland and like-minded places where taxability is at 0.1% (or some other ridiculously low number). If this oversight changes, so will the profits dwindle to a much lower percentage, now suddenly it will be a fair game for internet companies on a global scale, which is NOT what the US wants at all.

When we consider “The prime minister adopted a harder stance on the need for big internet companies such as Facebook and Twitter to do more to cooperate with the surveillance of terror suspects“, that fear will hit many and suddenly there are more holes in the collected data, downgrading businesses, the economy and heaven forbid, the DOW Jones Index, hence kitty goes into ‘UCLA’ mode.

But many in Europe are now a lot more awake, the events in Paris did that, when an actual terror attack hits a place like Paris, people suddenly notice and their fear for their safety spring into action, which is counter-productive for these US firms (as the terror attack is not happening in the US), corporate greed takes a front seat on what needs to happen, all under the guise of ‘civil liberty’.

As the president came with “In a sign of the concern in the US at the threat posed by extremists in Europe and in Syria and Iran, the president said disfranchised Muslims were one of the greatest challenges faced by Europe. “It is important for Europe not to respond with a hammer with law enforcement,” Obama said at a press conference with Cameron as he contrasted the way in which US Muslims had integrated and regarded themselves as wholly American“, really? How did Americans react on September 12th 2001? They couldn’t get the DHS started fast enough! In addition, let’s take a look at the Guardian in 2012 (at http://www.theguardian.com/commentisfree/2012/dec/29/fbi-coordinated-crackdown-occupy), ‘Revealed: how the FBI coordinated the crackdown on Occupy‘. It seems that ‘civil liberties’ are not an issue, when profit (read: banks) are in play. If we accept the quote “The document – reproduced here in an easily searchable format – shows a terrifying network of coordinated DHS, FBI, police, regional fusion center, and private-sector activity so completely merged into one another that the monstrous whole is, in fact, one entity: in some cases, bearing a single name, the Domestic Security Alliance Council. And it reveals this merged entity to have one centrally planned, locally executed mission. The documents, in short, show the cops and DHS working for and with banks to target, arrest, and politically disable peaceful American citizens“, now apart from the Snowden issue, I regard the Guardian to be a good paper, this gives a clear view that ‘civil liberties’ is not an issue in the view of profit and in the view of those depending on thus stated profit.

So here we see the clearer view of Kitty (Oval Office) versus Tiger (10 Downing Street). David Cameron needs to get a handle on the terror fear which goes a lot further then ‘commercial interests’, he needs to actually address and deal with these fears, hence the need for data. In this matter he had to speak to the President, let’s face it, getting GCHQ to download Exabyte’s of data (whilst permission is pending), without a meeting first is just bad form. On the other hand we could ask that data set from North Korea, apparently that is where the top hackers are today (according to US officials).


Leave a comment

Filed under Finance, IT, Law, Media, Military, Politics

Exploiting mobile users

Is it not amazing that in an age, where we all move into areas where things getting cheaper and cheaper, we see that mobile phones is the one article that remains into the top priced push. Yes, when you move to the post office, or to some ‘budget’ place, the only ‘cheap’ phones are the ones that are the ones that are basically in the bottom part of functionality, phones that have less than 6 months of decent quality usage before Google pushes for more updates, more android and the applications will add towards the maximum RAM.

This is my situation, I got a new phone in 2012, I needed a new one, and the one I bought was ‘decently’ priced at $299. I never regretted buying it. It still has a good screen, I have one game and a few applications, yet over the last two months the push has shown that when I have more than 2 apps running (including the dialler) the lag, the jittery screen, it all starts getting slightly wobbly, so I lock the phone, unlock it, remove all apps except the one I need and it all works fine again. Yet, my phone needs replacing not due to the hardware, but purely due to software. Looking around has been quite the revelation.

Looking at those options, I see that the $99 phones are less and less useful (specifically the smartphones). So as I started to dig, I am seeing a new change. If you want to find the price of a phone, it is often harder and harder to get clear pricing, more important, we can find less and less about how prices were and how the prices devolve.

Is it not strange that there is such an abundance of buy now places, but less and less information on the devices, the price and how long these articles are set to be for? The mobile is the new field for the technological armistice race and there are too many parties willing to make certain that the people cannot be properly informed. You see, this field has evolved for control. In the 90’s and the decade after that, it was relatively simple to get information on what graphic card one needed, which soundcard would be best. But not unlike the gaming industry, the information places are given less and less information. Is it not strange that Ubisoft (a gaming company) did not give a testing sample of Assassins Creed Unity weeks in advance? Especially when literally billions are riding on it? This is at the core of the issue, at the core of some ‘technology’ pages that are less and less information, more and more ‘typed’ marketing, not for their readers, but for the prospective buyers of the product. The media has been changing more and more and many readers remained asleep whilst reading. I must admit that the last description might not be accurate. Many will not realise this faltering until they are confronted with the fact of change (not unlike me).

If you’re looking for a console you can Google ‘PS4 price console’ and you will get pricing information on the very first page, even price drops, all localised. For mobiles it is a jungle out there and no matter how many ‘suddenly’ appear, when you want to look for that actual good deal (like the ZTE ZMAX) you will suddenly find that no one has such a good deal in stock (finding a decent site is also a challenge). They have cheaper (ad therefor useless) smartphones (I will dwell on that shortly) and of course the really ‘up to date ones’ which are not that much better than a ZTE, but will cost you 275% – 450% more. It is all about the money in the end!

You see those who choose Android (like me), will now learn what the cost of alleged abandonment is. (at http://www.zdnet.com/article/google-stops-providing-patches-for-pre-kitkat-webview-abandons-930m-users/), we saw early this week that Google is now stopping the update of the older versions. This means that as we see the headline ‘Google stops providing patches for pre-KitKat WebView, abandons 930 million users‘. This includes the bulk of the people who bought their mobile before Q4 2013. What a fine android web we weave!

You would think that it is a simple matter for updating, don’t you. Well that is not entirely correct. In my case Motorola was pretty decent in giving the information, however, when I press system update, it tells me that I am up to date, so I cannot get beyond 4.1.2 Android. This is now at the heart of several problems.

Who knows what version they are on and more important, when we consider the following text from ZDNet “In other words, the next time a researcher or hacker finds a way to exploit WebView on pre-KitKat Android, Google won’t create a patch for the vulnerability itself. However, if anyone else builds one, Google will incorporate those patches into the Android Open Source Project code“, more important, as long as this is not fixed, an increasing population will be at the mercy of forced upgrades through buying new phones outright, or chaining themselves to a new contract.

There are two sides. In fairness, should Google keep on fixing their ‘flaws’ ad infinitum? Yet on the other side, if my 2 year old mobile is now a security risk, what on earth am I paying for? More important, in this economy we would keep on paying premium just to be connected? The math does not balance out towards the need of the user. So are we witnessing a start from smartphone, back to normal phones? Let’s face it if smartphones are charged to your account and after that abandoned to this extent, what should we do?

Some will push for Apple, but there to some extent, the danger is changed, not necessarily removed. A normal phone will less likely have these issues, or change to the new player. Even though the brand leaves (from past events) a bitter taste in my month, Samsung has taken a new direction with their mobiles called Tizen OS. The following parts are known at present “It is Linux-based platform built from Nokia and Intel’s ditched MeeGo“, open source means many views, so perhaps better patches. The fact that it is Linux based is not bad either. The fact that Tizen is using HTML5, it means that we will get a wave of content that is state of the art, slim and memory efficient (no flash needed). You can look for yourself to some results (at http://www.creativebloq.com/web-design/examples-of-html-1233547), so it seems that the new road that Samsung is taking is also changing the perception that they are getting. From these upgrades, Samsung could evolve from ‘player’ to ‘top contender’. It will definitely bring the fire to the ankles of Apple, which is never a bad idea.

Tizen is not new or just a gimmick, it had been announced before and more important, it has been in development for years, yet with the Google decisions and with the issues that mobile users might be facing sooner rather than later, the timing for Tizen is pretty good and Samsung could benefit greatly, they will get additional benefit as people realise that patches are no longer coming for their less new mobiles, which will hurt consumer confidence.

If you have any doubts then the clarity from Greenbot.com should help. “Google drops Lollipop on November 3rd 2014,  if you have the right device“, which makes us wonder, do I have the right device? “Maybe you don’t have a Nexus phone or tablet. Well, then the situation gets a little murky. If you have a phone purchased in the last year, odds are good that you’ll get an upgrade to Lollipop…eventually“, which gets us, what if your phone is older than one year? Then what? Which gets us the last part “Manufacturers like Samsung, LG, HTC, and Motorola have promised swift updates (typically within 90 days of release) for top devices, but those have to go to carriers to be tested before release, too“, knowing I am ‘up to date’ with my version ‘4.1.2.’ does not inspire confidence! How many people asked questions about versions of Android when they bought their phone? I am a technologist and I never gave it too much thought (other than that I wanted an Android phone). Now, it seems that my Motorola is will remain on Jelly Beans (4.1.2) and now, we have ourselves a ball game, because as this unbalanced approach is pushed from both the desire to remain free (not chained to a provider) and as the life cycle of a mobile phone is now in danger of staying under two years due to the Google changes, we now see the need to not just chastise Google, but to make it clear (actually demand) that consumers are properly informed on the limitations that they are buying at $300, if we regard that patching is done to undue the lacking security of a product sold, we get a new game where the consumer must be informed clearly in a shop regarding the purchase they make.

A costly jump that might not have been needed! This year will bring changes to the mobiles and the shops selling them, I wonder if Google considered that, or perhaps they never cared. Especially when the people get told that they will not face any issues, if they had a Nexus phone (Google’s mobile). Samsung is not without options either, as they progress towards ownership of Blackberry, they might drill into a new mobile market that revolves around data and communication security, which is another mobile hot potato, and it instantly gets them huge chunks of the financial sector for reasons not here speculated! Tactically both Google and Samsung have made brilliant moves, for the consumers not the worst move but likely a costly one this year!

Will you remain in a Google mind or move to Tizen?

Will Eva choose to try the Apple in the end?

Time will tell!


1 Comment

Filed under Finance, IT, Media, Politics, Science